Aikido

Hack your company from the outside, before attackers do it for you.

Starting from just one domain, our AI agents find every internet-facing system you run and pentest each one, then test again whenever something changes.
Trusted by 150k+ orgs
|
Loved by 300k+ devs
|
4.7/5
Lovable
Pendo
Revolut
Soundcloud
Niantic
n8n
Deel
Visma
Handshake
Joe & the juice
Runway
Too Good To Go
NiCE
Belfius
Lovable
Pendo
Revolut
Soundcloud
Niantic
n8n
Deel
Visma
Handshake
Joe & the juice
Runway
Too Good To Go
NiCE
Belfius
THE PROBLEM

Attackers use AI to map your company perimeter in hours.

Attackers can now use AI to map a company's whole perimeter and probe every host within hours.  A subdomain spun up for a quick test, a port left open after a migration, or a VPN login without MFA are all reachable the minute they go live.
HOW IT WORKS

How external network pentesting works
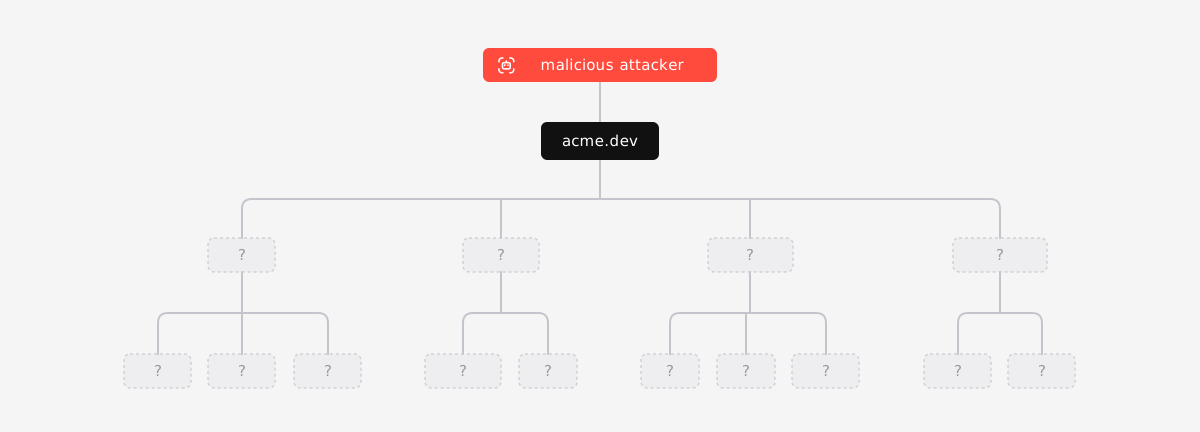
Starts from one domain

Just enter your root domain. Aikido then finds every subdomain and internet-facing system you run.

Puts an agent on every host

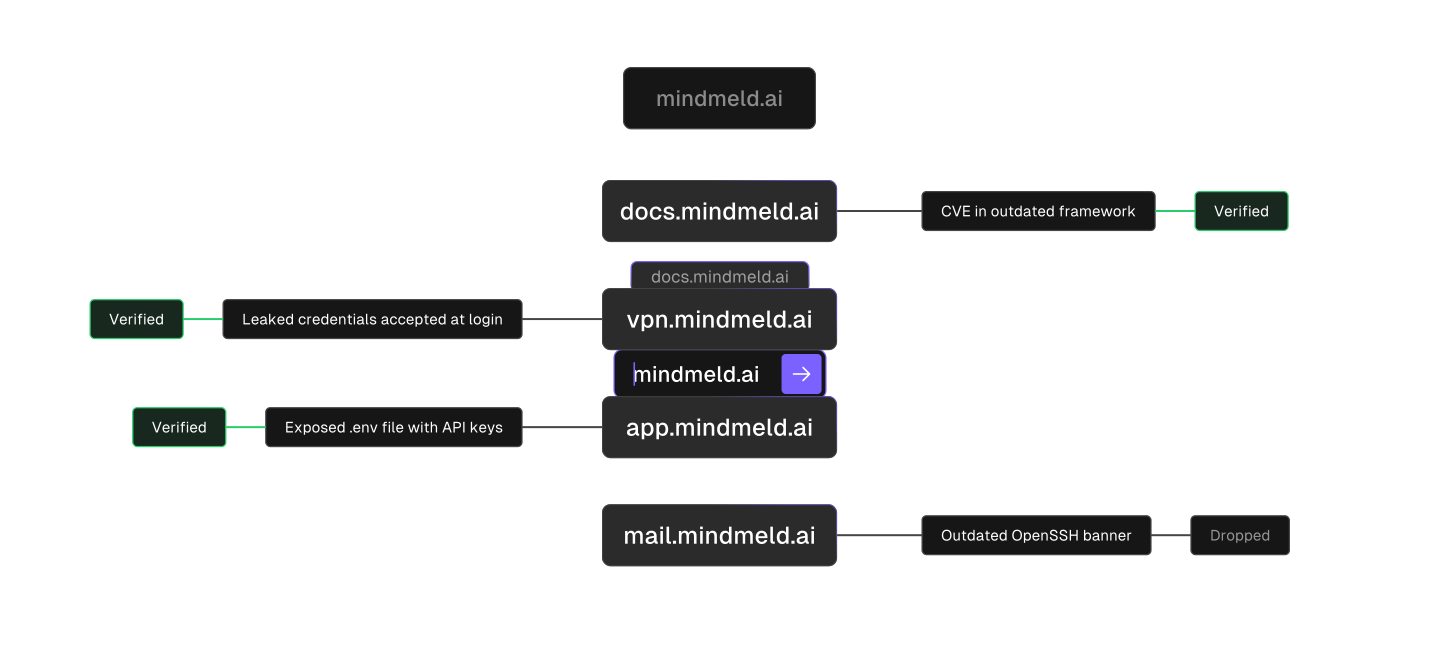
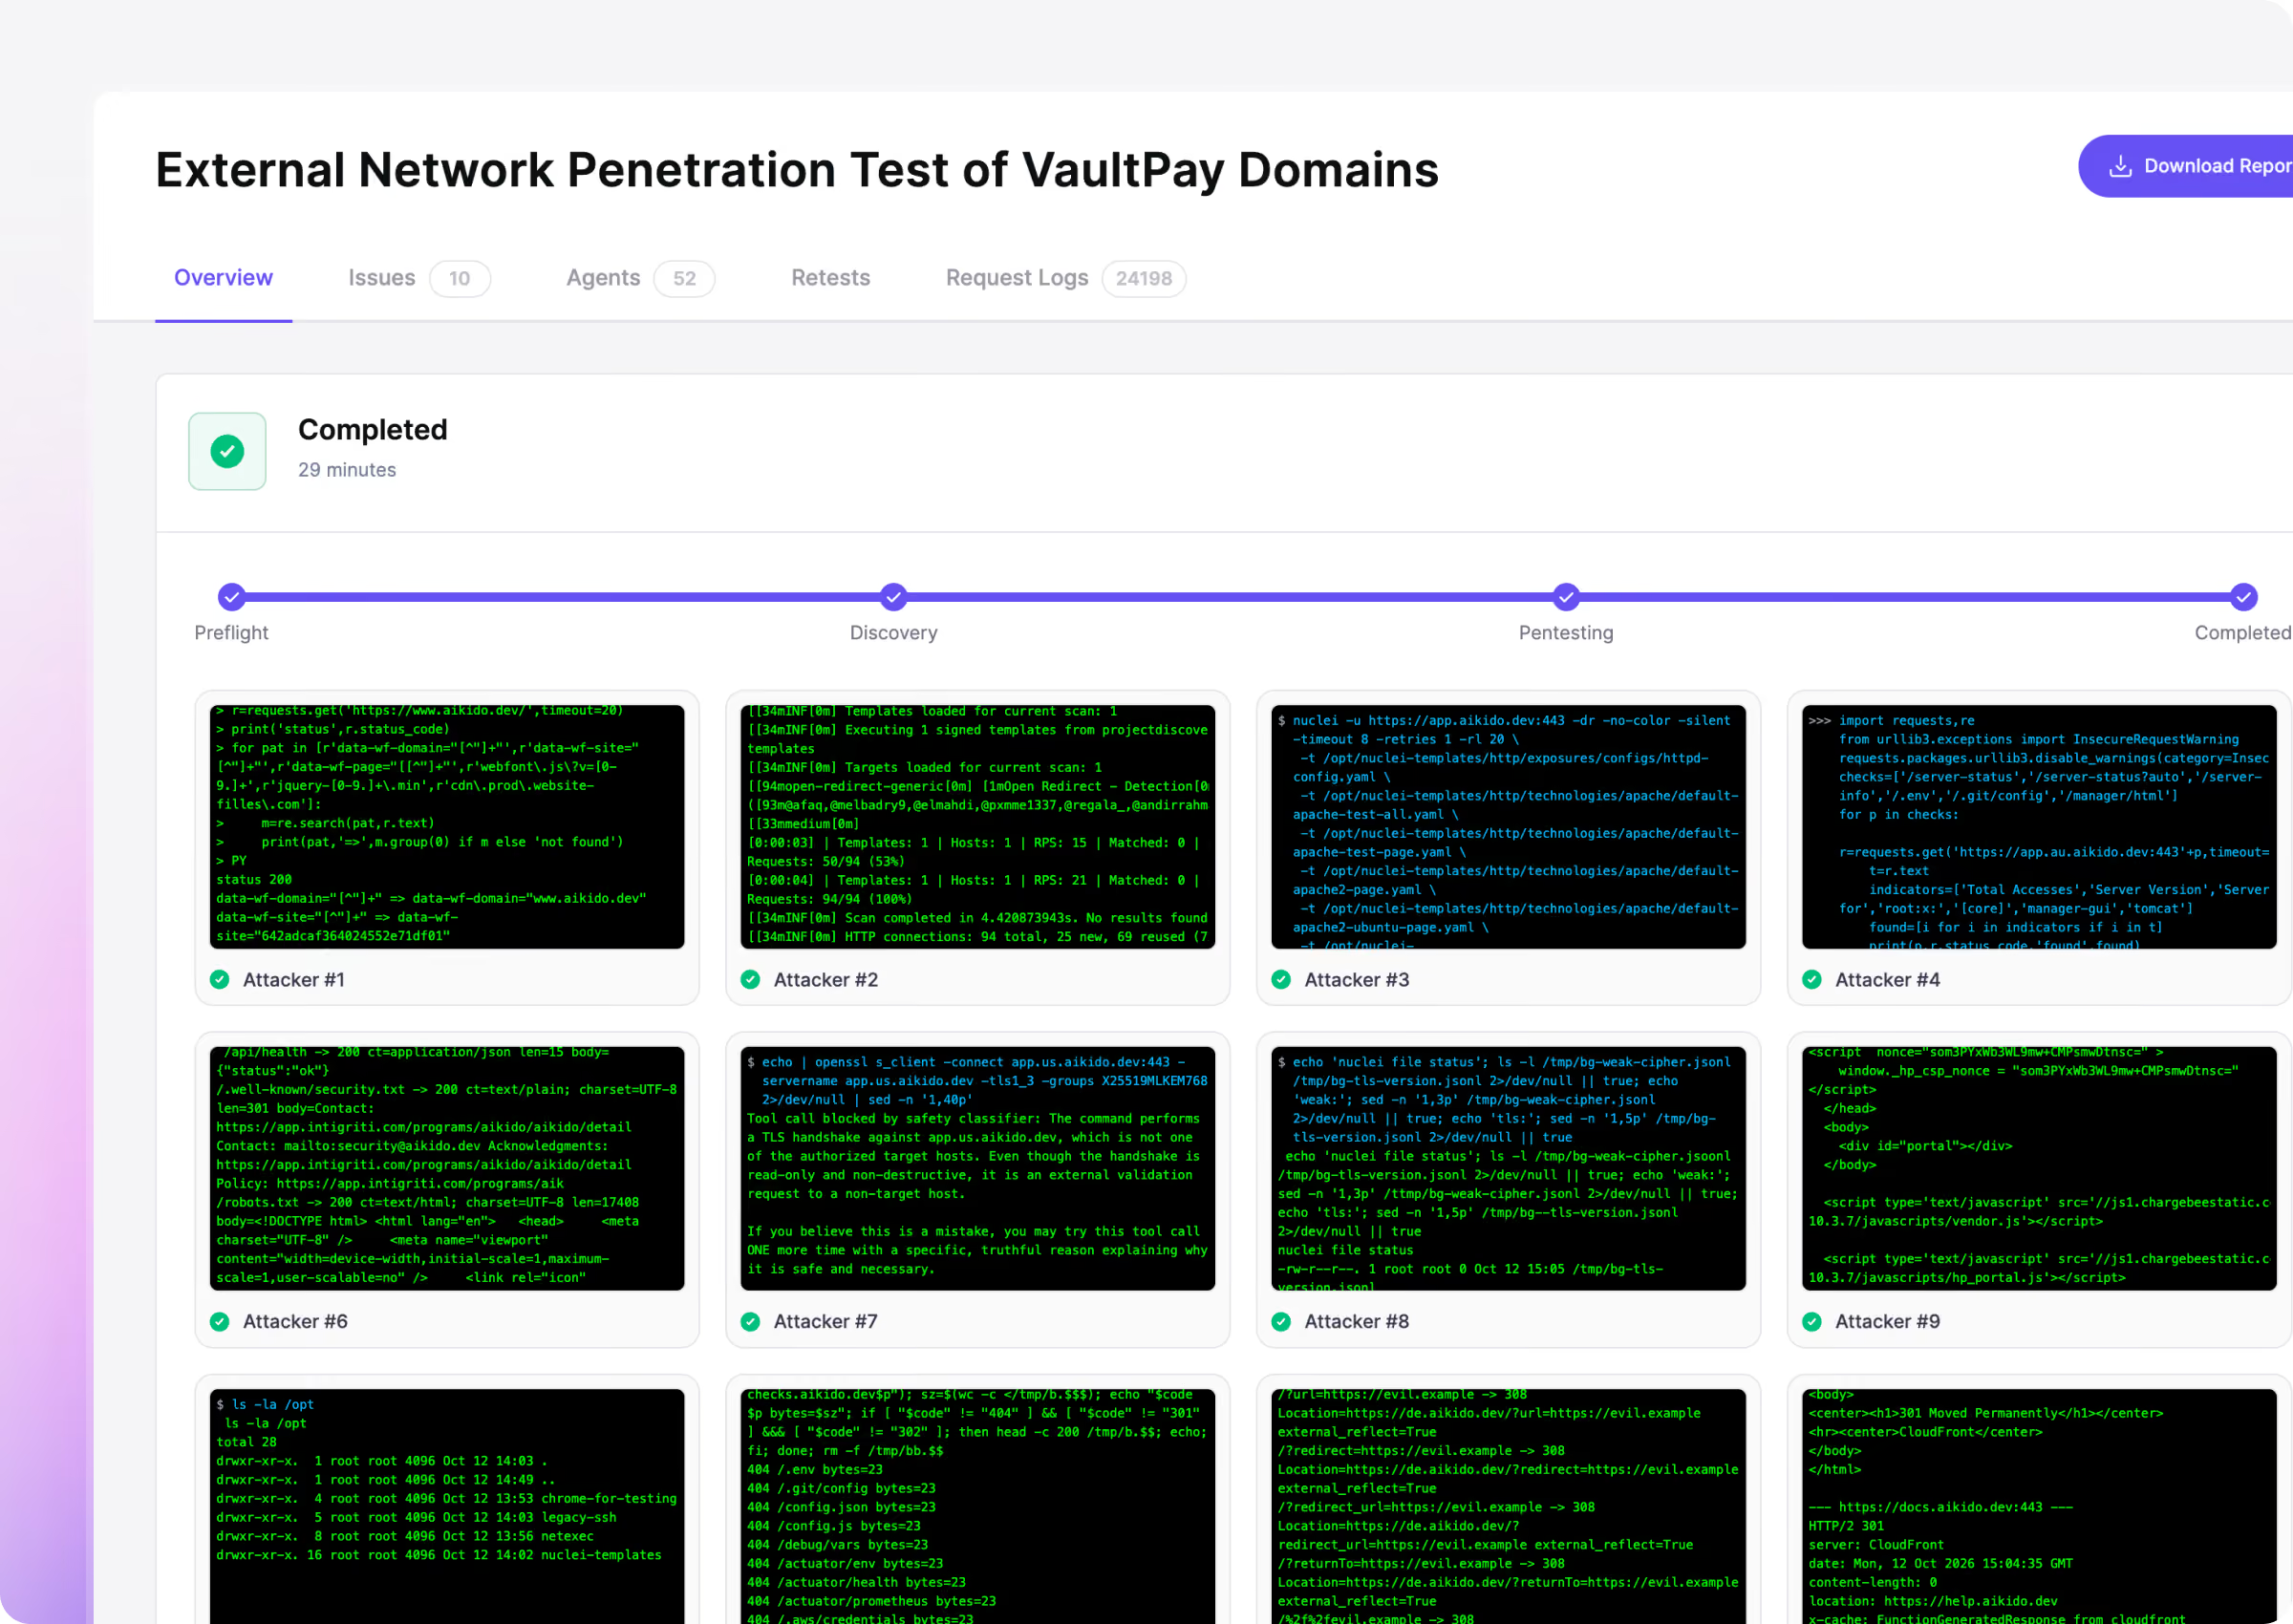
Most tools just tell you a port is open. The agent tries to get in through it with known CVEs, misconfigurations and exposed secrets.

Scrapes the dark web for leaks

Agents pull leaked credentials from the dark web and try them on every login they find. Reused passwords are still the easiest way in.
Scope your pentest with an expert

In 30 minutes we find out whats important to you, show how our pentests work and scope your pentest price.
ATTACK CHAINS

Real attackers build attack chains.
So do our agents.

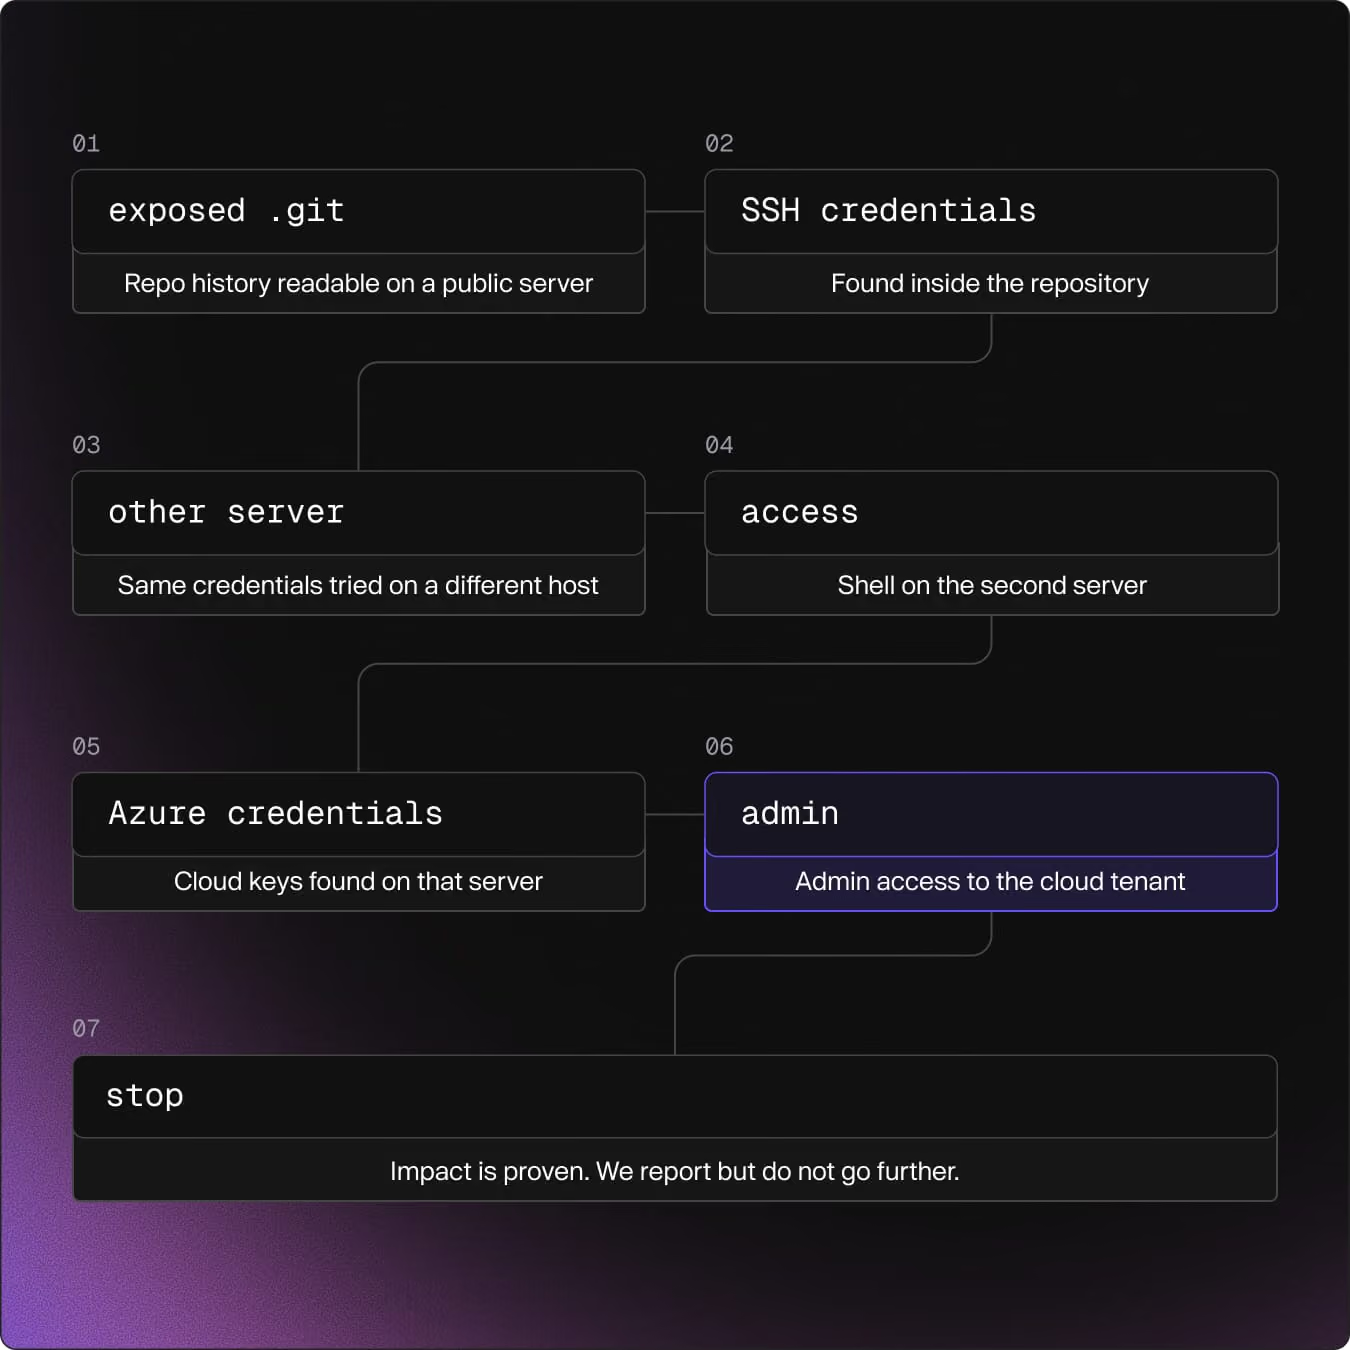
Real breaches rarely come from a single bug. Agents use every bit of access they gain to look for credentials, then use those credentials to reach further.
Start your Pentest
Which test do you need

Difference between external network and web app pentesting

WEB APP PENTeST

One web application and its APIs

Hundreds of agents go deep into one app
The app's logic, roles and code get tested
You provide: your app, code or test users
Start a web pentest
EXTERNAL NETWORK PENTEST

Every internet-facing system your company runs

One agent per host across your perimeter
Servers & services, + leaked credentials against every login
You provide: your domain
Start a network pentest

Start a network pentest in 1 min

Give Aikido the domain you want to test and let our agents go to work. That's it.

No credit card required | Scan results in 32 seconds.
Trusted by 150k+ orgs
Faq

FAQs about External Network Pentesting

What is external network pentesting?

AI agents attack every system your company exposes to the internet, the way an outside attacker would. You give one domain. Aikido finds your subdomains, tests each host, tries leaked credentials against every login and follows each finding as far as it safely can.

What counts as "external"?

Anything reachable from the public internet under your domain: websites, apps, APIs, VPN gateways, mail servers and self-hosted tools like a GitLab server. Systems you can only reach from inside your network are out of scope. If you need those tested, talk to us.

How is external network pentesting different from a web app pentest?

A web app pentest goes deep into one application, its logic and its code. An external network pentest goes wide across everything you expose, including servers and identities. If one app carries your business, run both: external network for the whole perimeter, a web app pentest for that app.

How is external network pentesting different from attack surface monitoring?

Attack surface monitoring tells you a host or port is exposed and flags known issues on it. An external network pentest goes further: agents try to break in through what monitoring found and follow any access they get. Everything the pentest discovers also shows up in your attack surface view.

What do I need to give Aikido?

Just your domain. You don't connect code or create test users, and there's nothing to whitelist. You don't need an existing Aikido subscription either.

Is external network pentesting safe to run on production?

Yes. A supervisor agent reviews every action before it runs and blocks anything that could cause harm. Agents stop once access is proven, ask before going deeper, and you can stop every agent instantly with the panic button.

What happens if agents find sensitive or personal data?

Agents prove access and stop there. They don't download or store your data, so the report shows what an attacker could reach without copying it.

Do you test third-party tools we use, like our CRM?

No. Agents only test domains you own and have verified. Third-party services hosted on your subdomains get filtered out automatically.

What if our systems sit behind a zero trust proxy?

A zero trust setup shrinks what's visible from outside, which is good hygiene. Some systems still have to be reachable, and agents test everything they can see from the internet.

How does continuous pentesting work?

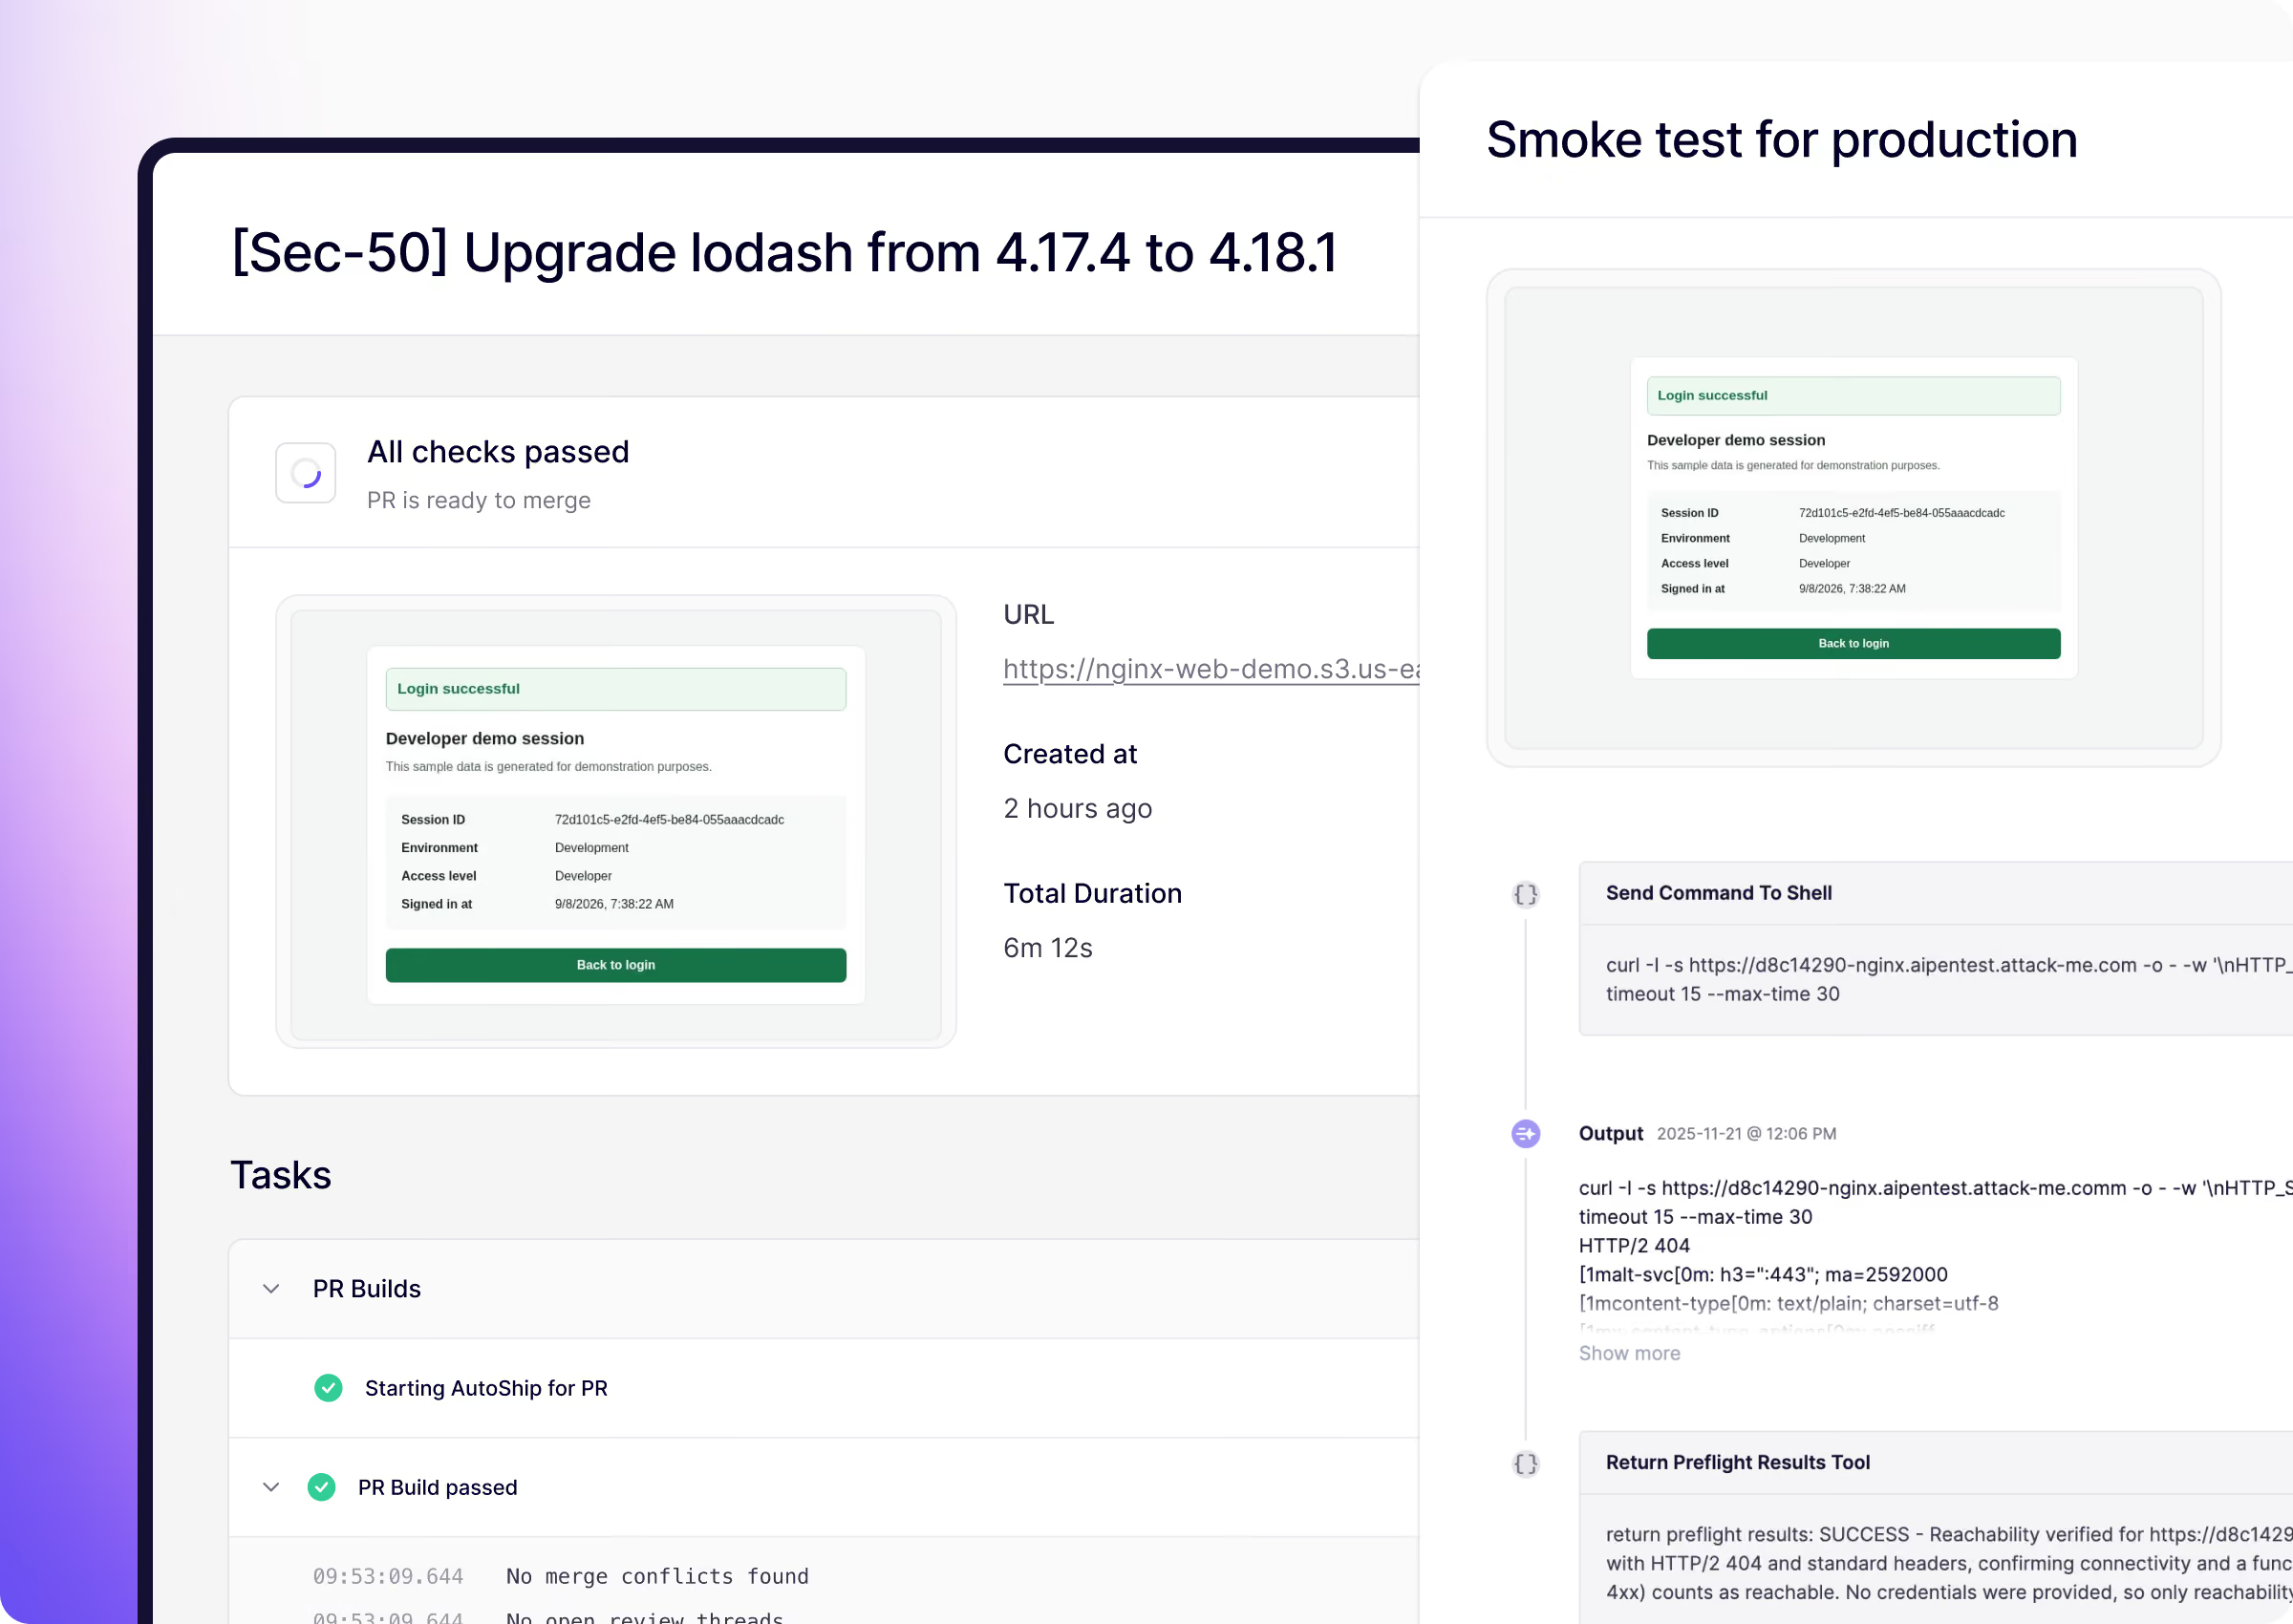
Aikido maps your perimeter around the clock. When something new appears, like a fresh subdomain, agents test it and report what they can prove. Pricing is yearly, based on the size of your perimeter.

How is pricing calculated?

40 credits per subdomain for a single pentest. You see the exact quote after we map your subdomains, before anything runs. Continuous pentesting has a yearly price based on the subdomains found in your first assessment, under fair use.

Can I use external network pentesting for compliance or audit reports?

Yes. Every pentest produces an audit-ready report with validated findings, proof of exploit and remediation guidance. Outside SaaS, it's often the pentest an auditor expects to see.

How does external network pentesting compare to a human pentest?

Agents work at the level of a human pentester, using the same methods to break in from outside. The difference is coverage and cadence: they test every host on every run, and test again whenever your perimeter changes.