
Software Security for FinTech
From compliance-heavy banking APIs to high-speed crypto exchanges, Aikido helps FinTech teams ship fast, stay compliant, and safeguard their SDLC, without slowing development.
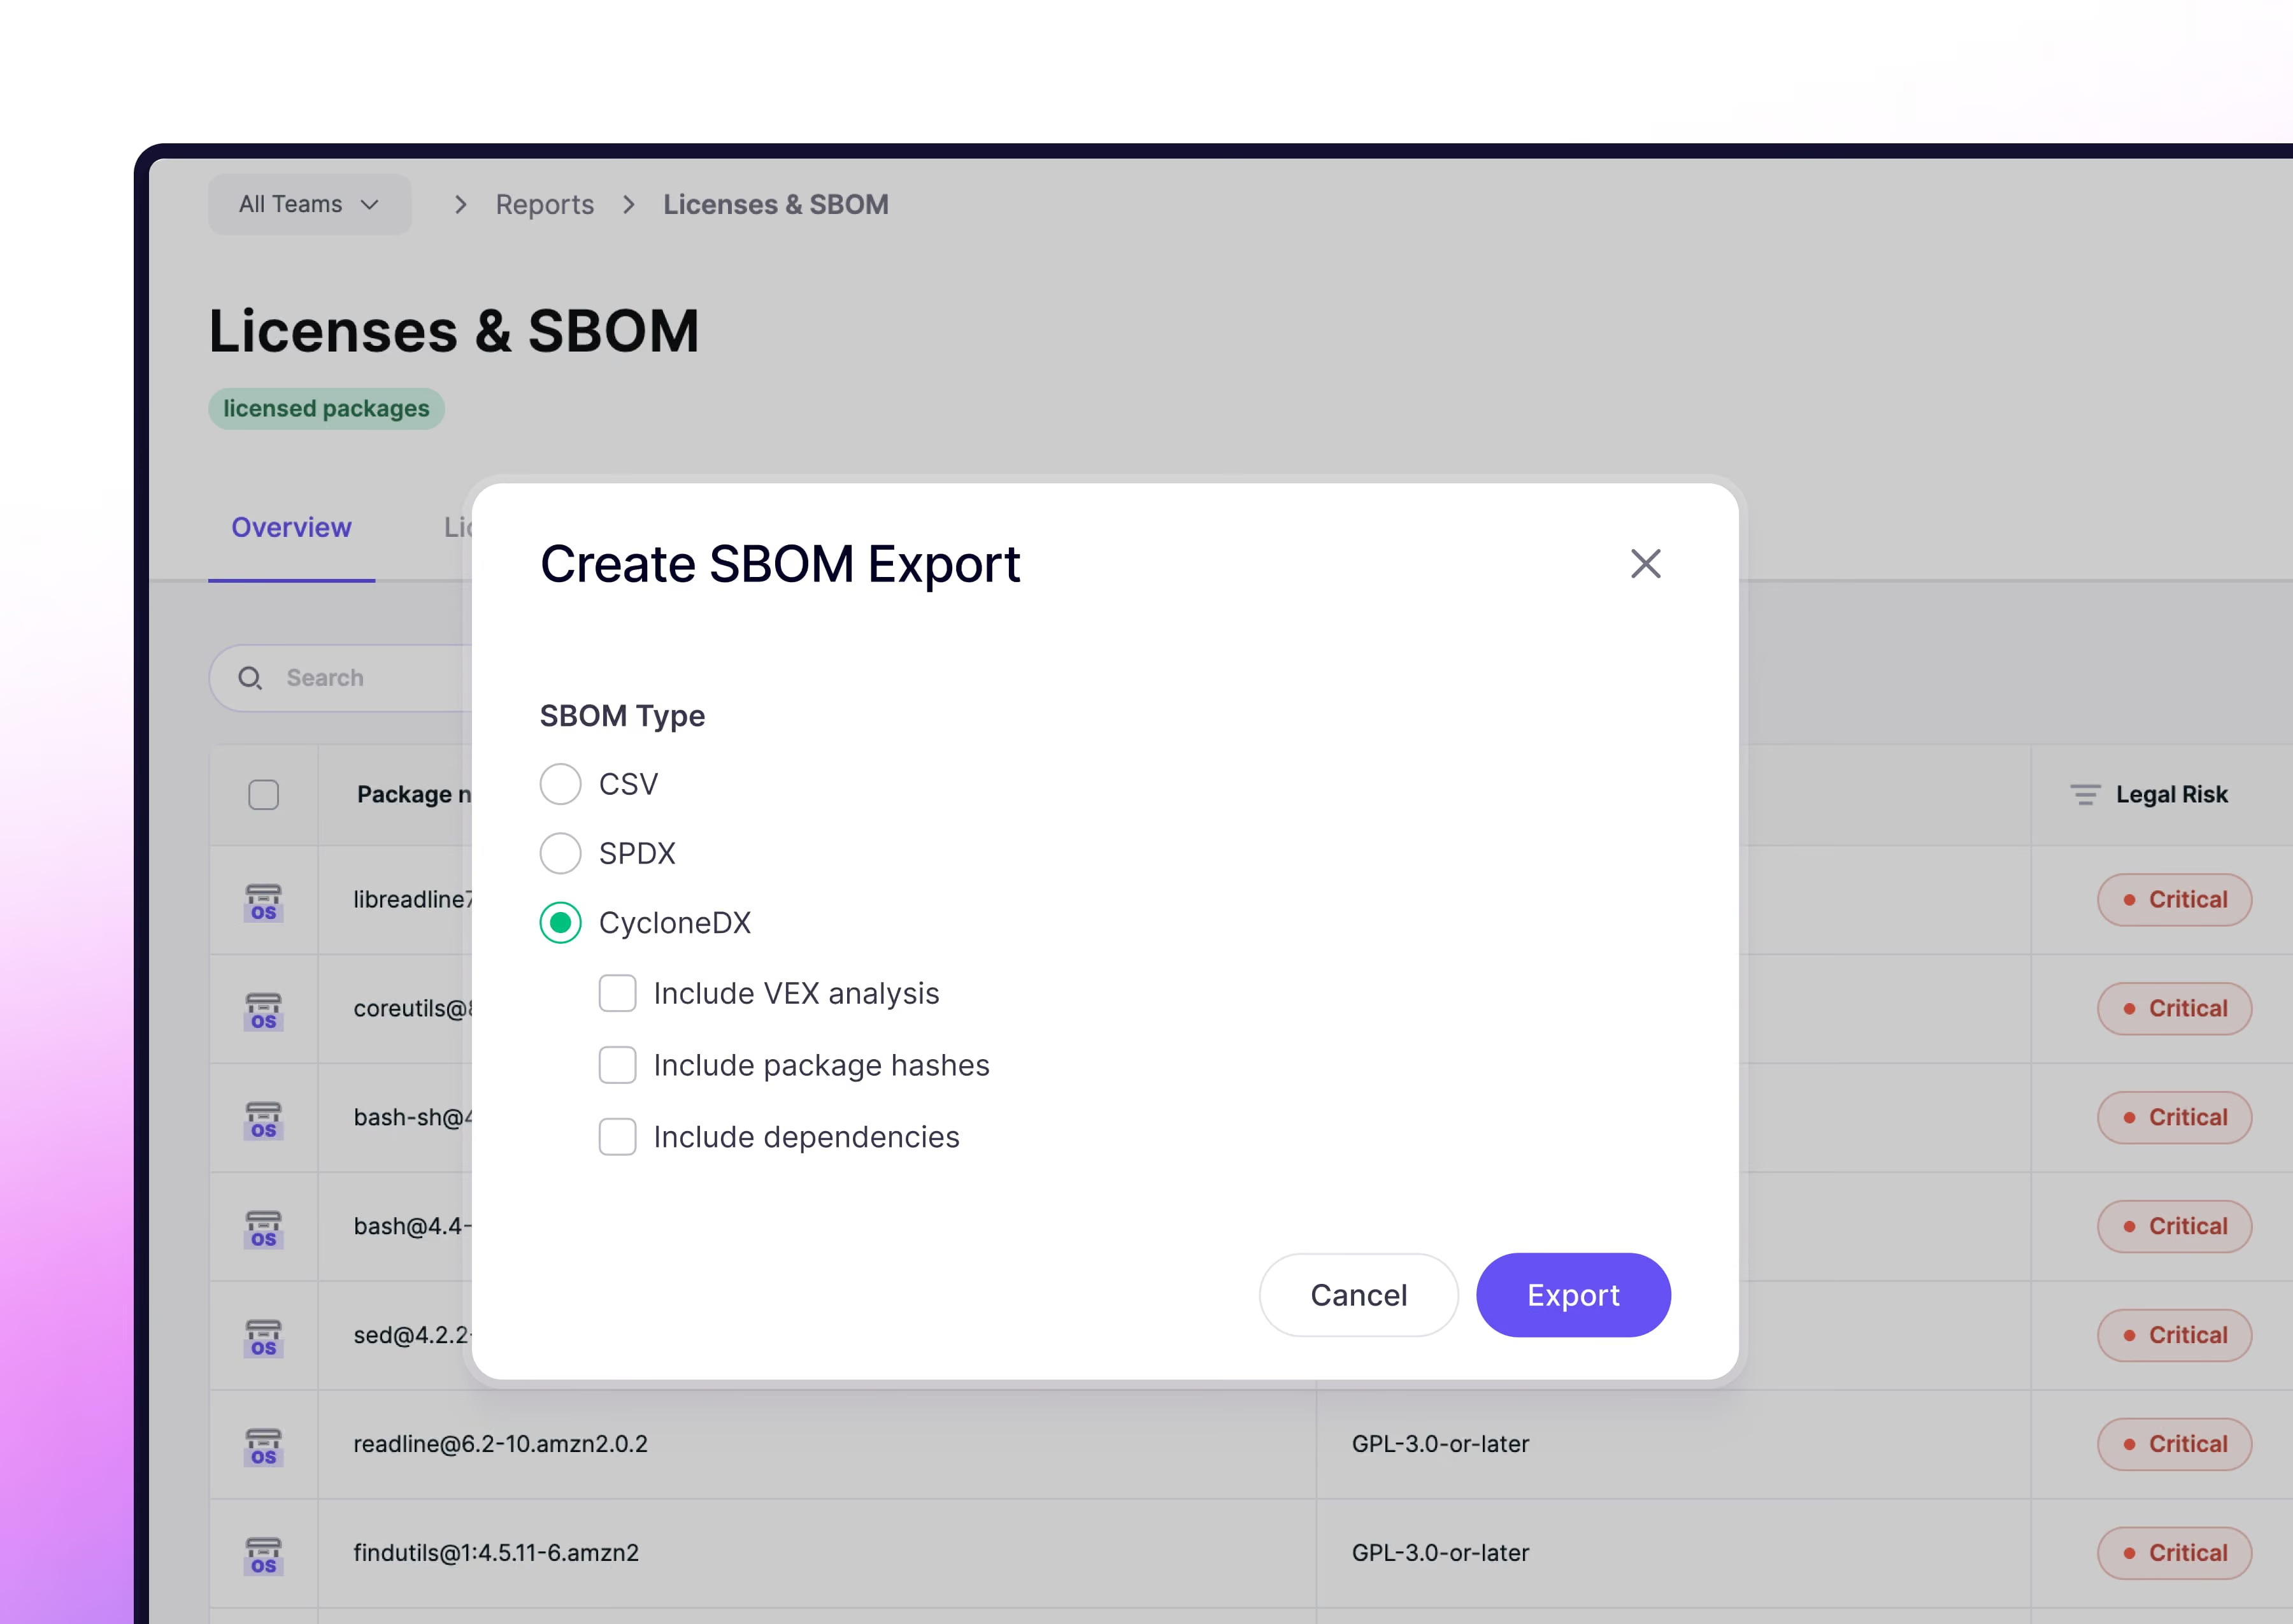






Features dedicated to FinTech firms
Accelerate security, win client trust
FinTech moves fast, but security and compliance can’t be left behind.
Aikido keeps your release cycles secure and audit-ready for DORA, PCI DSS, and ISO 27001, proving your posture tocustomers, partners, and regulators.
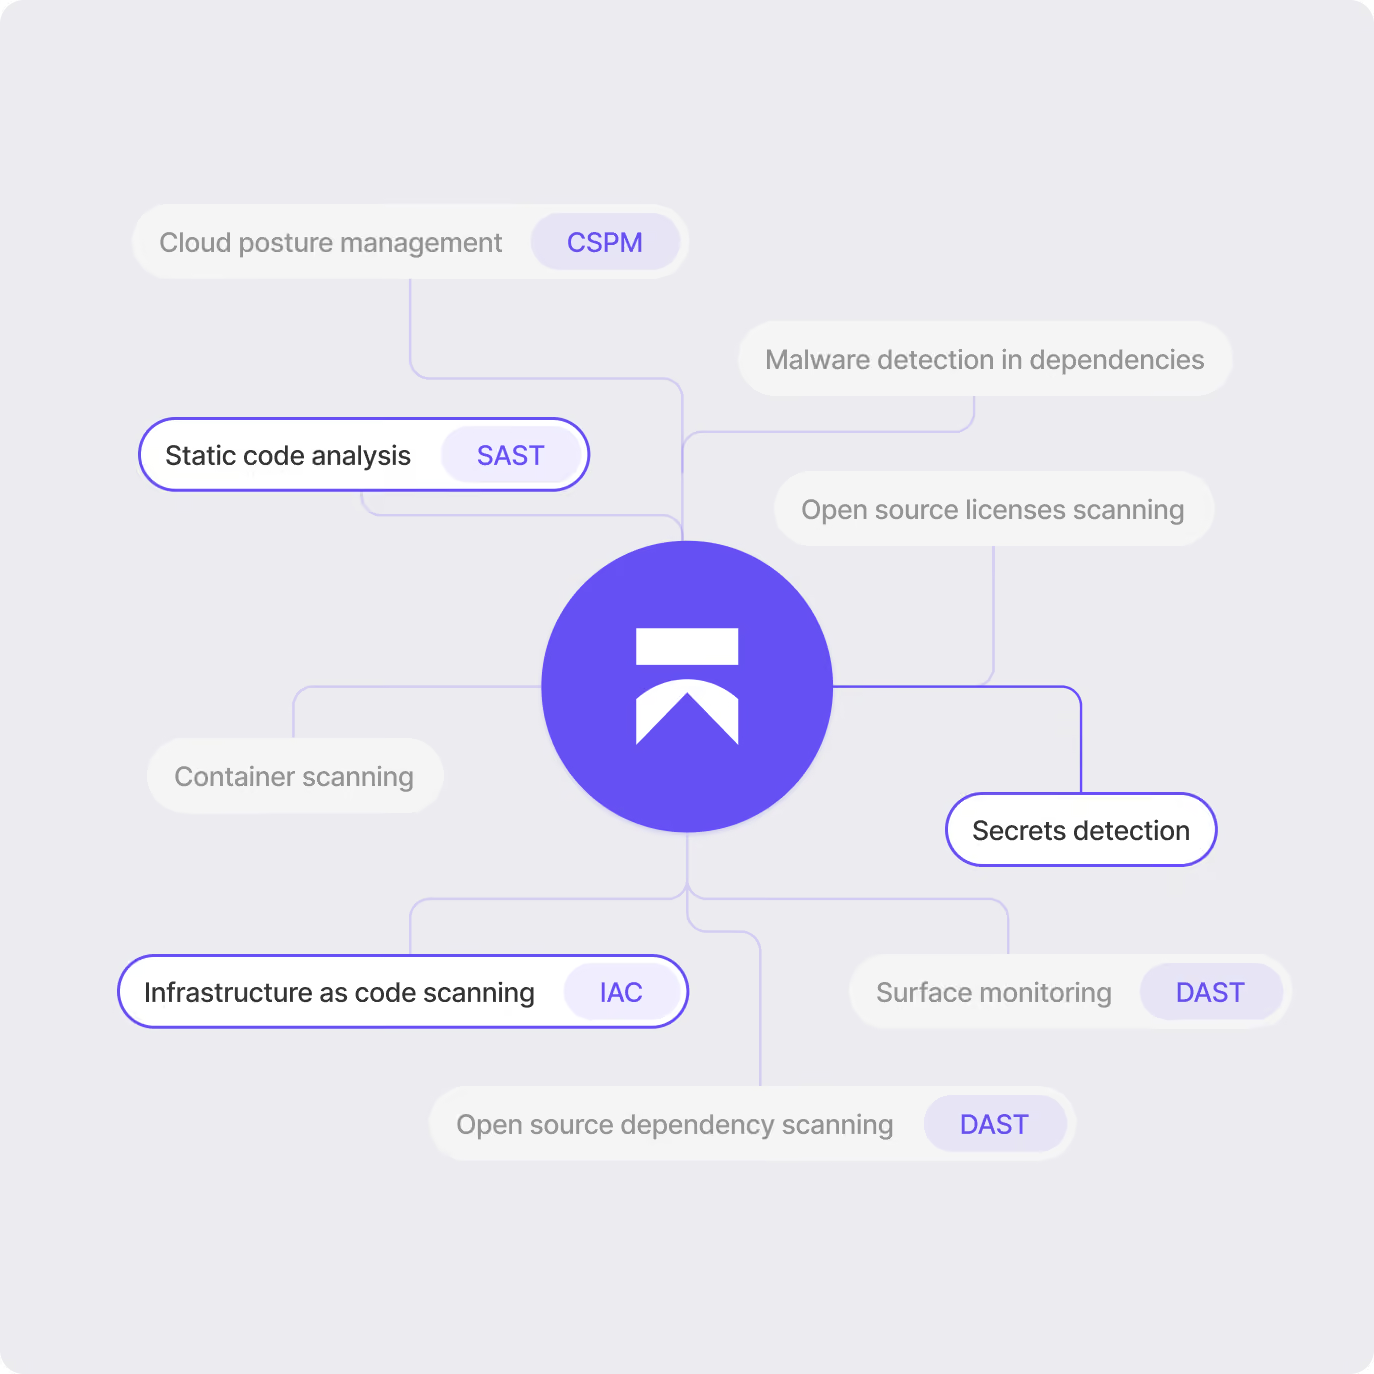
Industry leading security built for speed & credibility
In FinTech, credibility is currency. Aikido helps you meet the highest security standards without slowing delivery.
Unify detection, monitoring, and remediation
Fix issues before production
Prove compliance with audit-ready reports
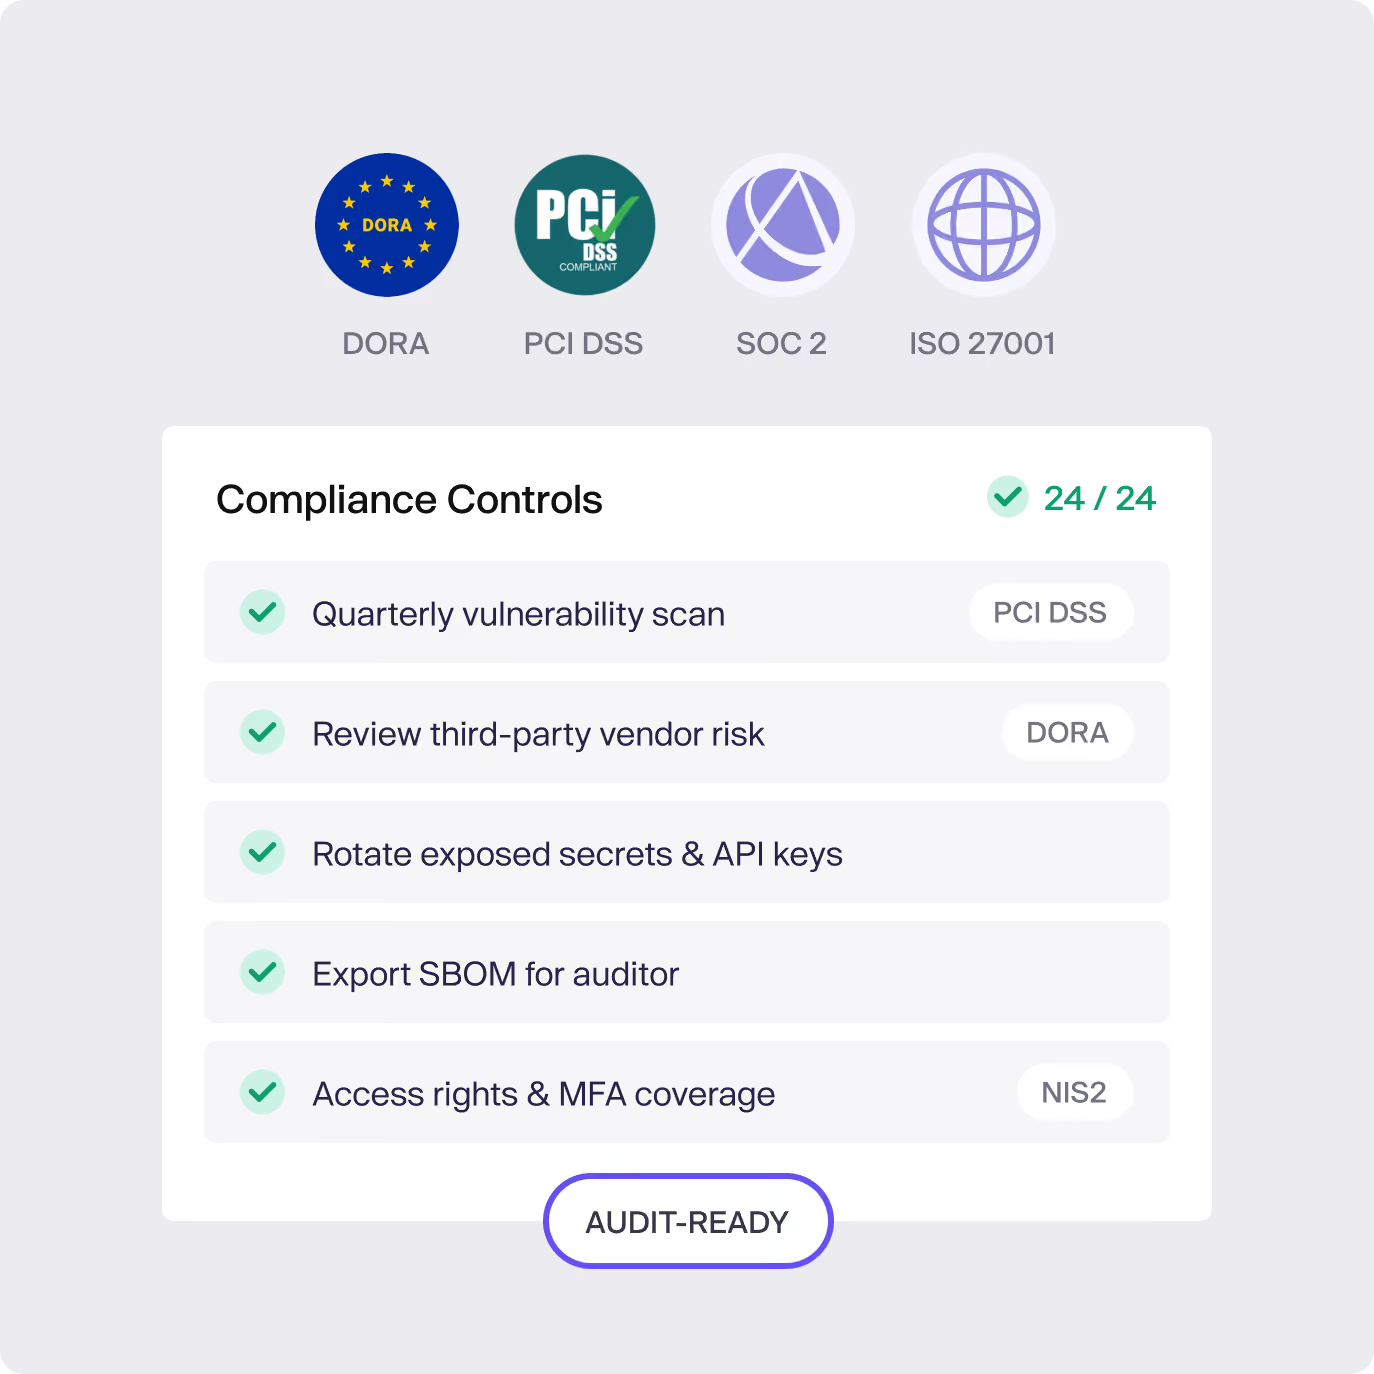
Hassle-free Compliance
From PCI DSS to DORA, ISO 27001, SOC 2, and NIS2, compliance is table stakes in FinTech. Aikido makes it easy to achieve and retain certification, with automated controls, clear reporting, and faster time-to-audit.
Automate SBOMs, OSS license checks & NIS2-aligned reports
Generate audit-ready evidence for DORA, PCI DSS, and more
Deliver clear proof to partners, auditors & regulators
Cut compliance overhead with built-in controls and reporting
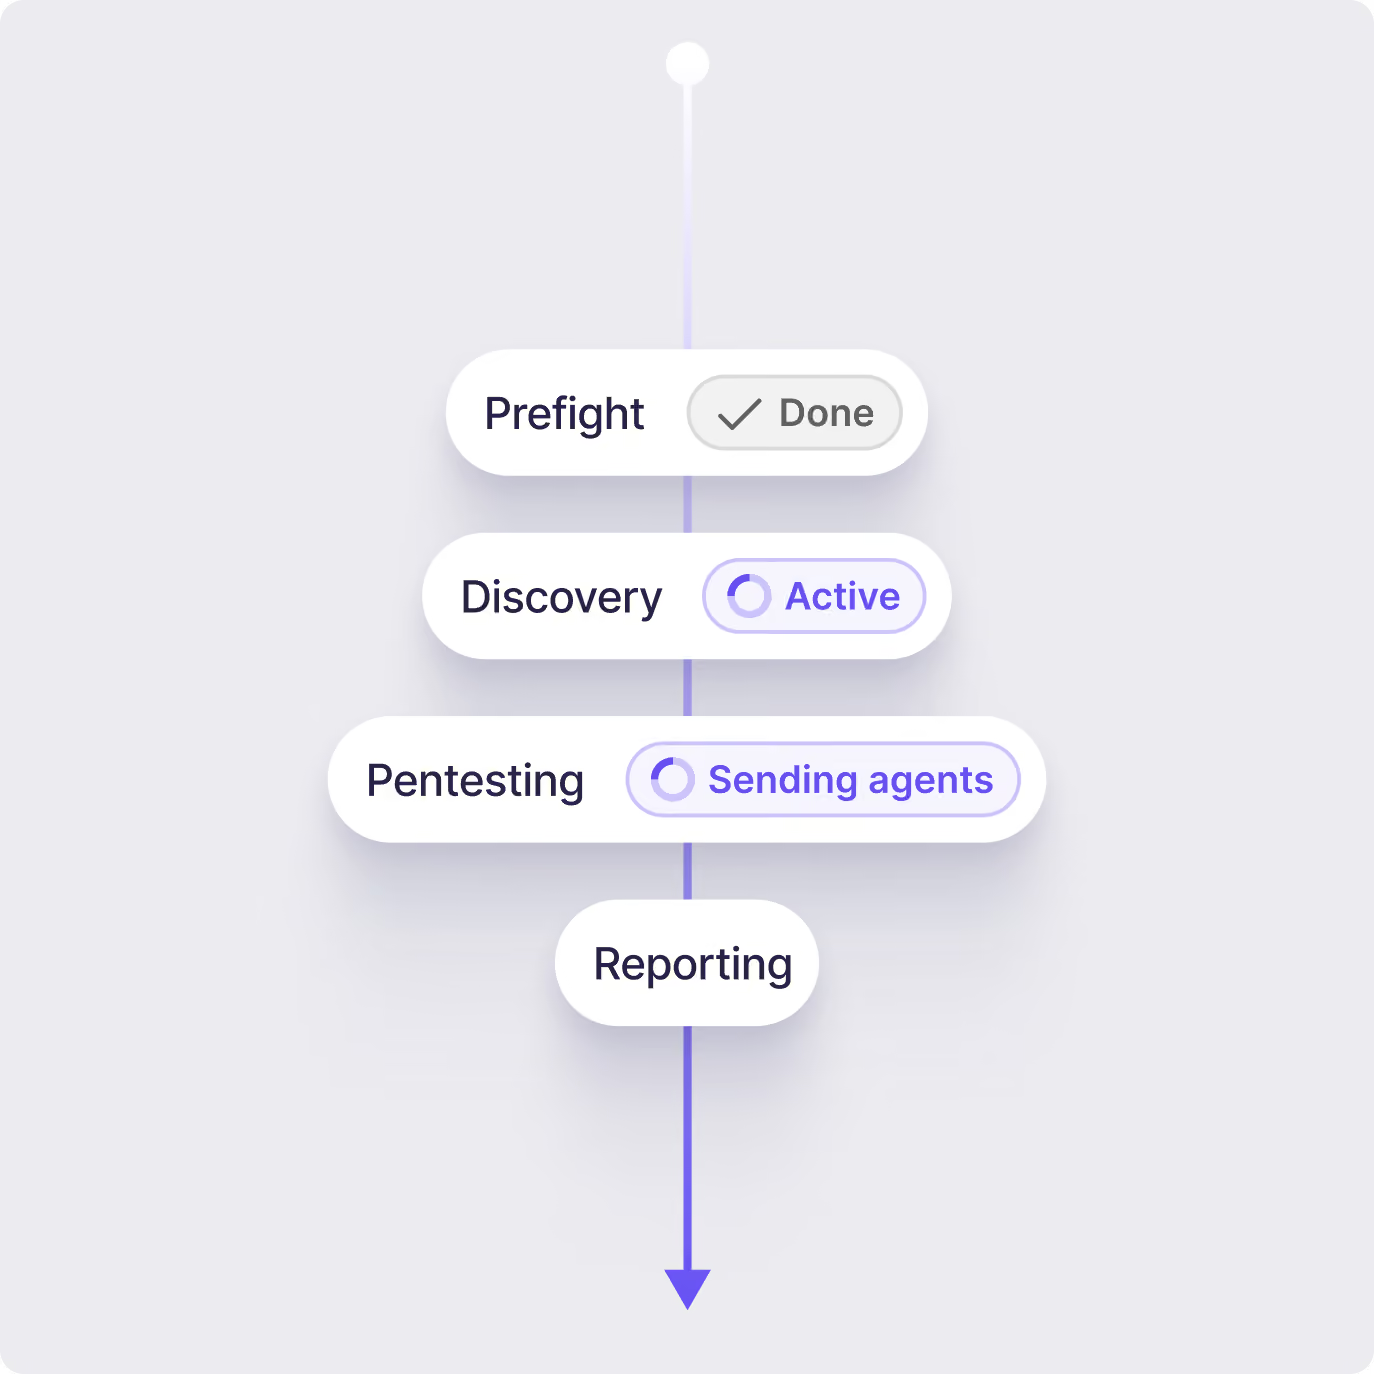
Autonomous AI Pentesting
Security isn’t just about scanning, it’s about understanding howreal adversaries move. Our AI agents analyze your code and deployed web apps or APIs, simulate real attacker behavior, and deliver a verified SOC2- and ISO27001-ready report - all within hours.
End-to-End Attack Paths: Map exploitable routes across code, cloud, and runtime.
Exploit Simulations: Test against real-world techniques without risk to production.
Prioritized Risk: Focus on the vulnerabilities attackers would actually exploit.
Crypto & Web3 ready
Crypto teams need proactive defense. Aikido adds in-app runtime protection to stop exploits in real time, and our Open Source Threat Feed surfaces risks others miss.
Open Source Threat Feed: Human-verified intel, tens of thousands of vulns & malware packages uncovered (incl. gaps in NVD/GitHub)
Runtime protection: block attacks as they happen inside your app
Early warning on zero-days in critical open-source dependencies
Everything you wish security tools actually did




Get Your Compliance In Check
Aikido performs checks and generates evidence for technical controls for ISO 27001:2022, SOC 2 Type 2, PCI Security standard, and for DORA. Automating technical controls is a big step-up towards achieving compliance.
ISO 27001:2022
ISO 27001 is particularly relevant for FinTech companies. This globally recognized standard ensures that you have a systematic approach to managing sensitive company information, ensuring its confidentiality, integrity, and availability. Aikido automates a variety of ISO 27001:2022 technical controls.
SOC 2 Type 2
SOC 2 is a procedure that ensures your service providers securely manage your data to protect the interests of your organization and the privacy of its clients. Show your commitment to safeguarding data by complying with SOC2. Aikido automates all technical controls, making the compliance process much easier.
DORA
The Digital Operational Resilience Act (DORA) is an EU regulation that requires financial institutions to strengthen their defenses against IT-related risks. Aikido helps with DORA compliance by automating the detection, and remediation of security vulnerabilities, enabling continuous monitoring, incident reporting, and management of 3d-party risks as required by the DORA regulation.
Payment Card Industry Data Security
The Payment Card Industry Data Security Standard (PCI DSS) require a set of security standards designed to protect cardholder data during and after financial transactions. Any organization that handles credit card information must comply with these standards to ensure the secure processing, storage, and transmission of cardholder data. Aikido automates many technical controls.
"One of our biggest wins is that the friction between security and our developers is gone. They trust that when Aikido raises something, it's worth their time."
Integrate with your compliance suite
Are you using a compliance suite? Aikido integrates with the suite of your choice.

Vanta
The fastest path to compliance. It collects 90% of the evidence needed for your certification.

Drata
Automates your compliance journey from start to audit-ready and beyond.

Sprinto
Sprinto is a one-stop platform for all security compliances and certification audits.

Thoropass
Thoropass is an end-to-end compliance solution offering a seamless security audit experience.

Secureframe
Leading security compliance automation platform that makes getting any compliance fast & easy.
SIEM
Centralize your security logs and accelerate threat detection in a single dashboard.
Get secure today,
quickly and for free.
Connect a repo to discover what the reasoning agents find in your codebase. Or run it alongside your current SAST and see what you’re missing.


FAQs for Fintech

We clone the repositories inside of temporary environments (such as docker containers unique to you). Those containers are disposed of, after analysis. The duration of the test and scans themselves take about 1-5 mins. All the clones and containers are then auto-removed after that, always, every time, for every customer.
Of course! When you sign up with your git, don’t give access to any repo & select the demo repo instead!
No! Unlike others, we're fully API based, no agents are needed to deploy Aikido! This way you're up & running in mere minutes & we're way less intrusive!