
See your whole cloud and fix what's reachable
Aikido maps your connected cloud accounts in a single view and links findings to the code and IaC templates with automated PRs that fix the issues. One fixed price based on your team size.
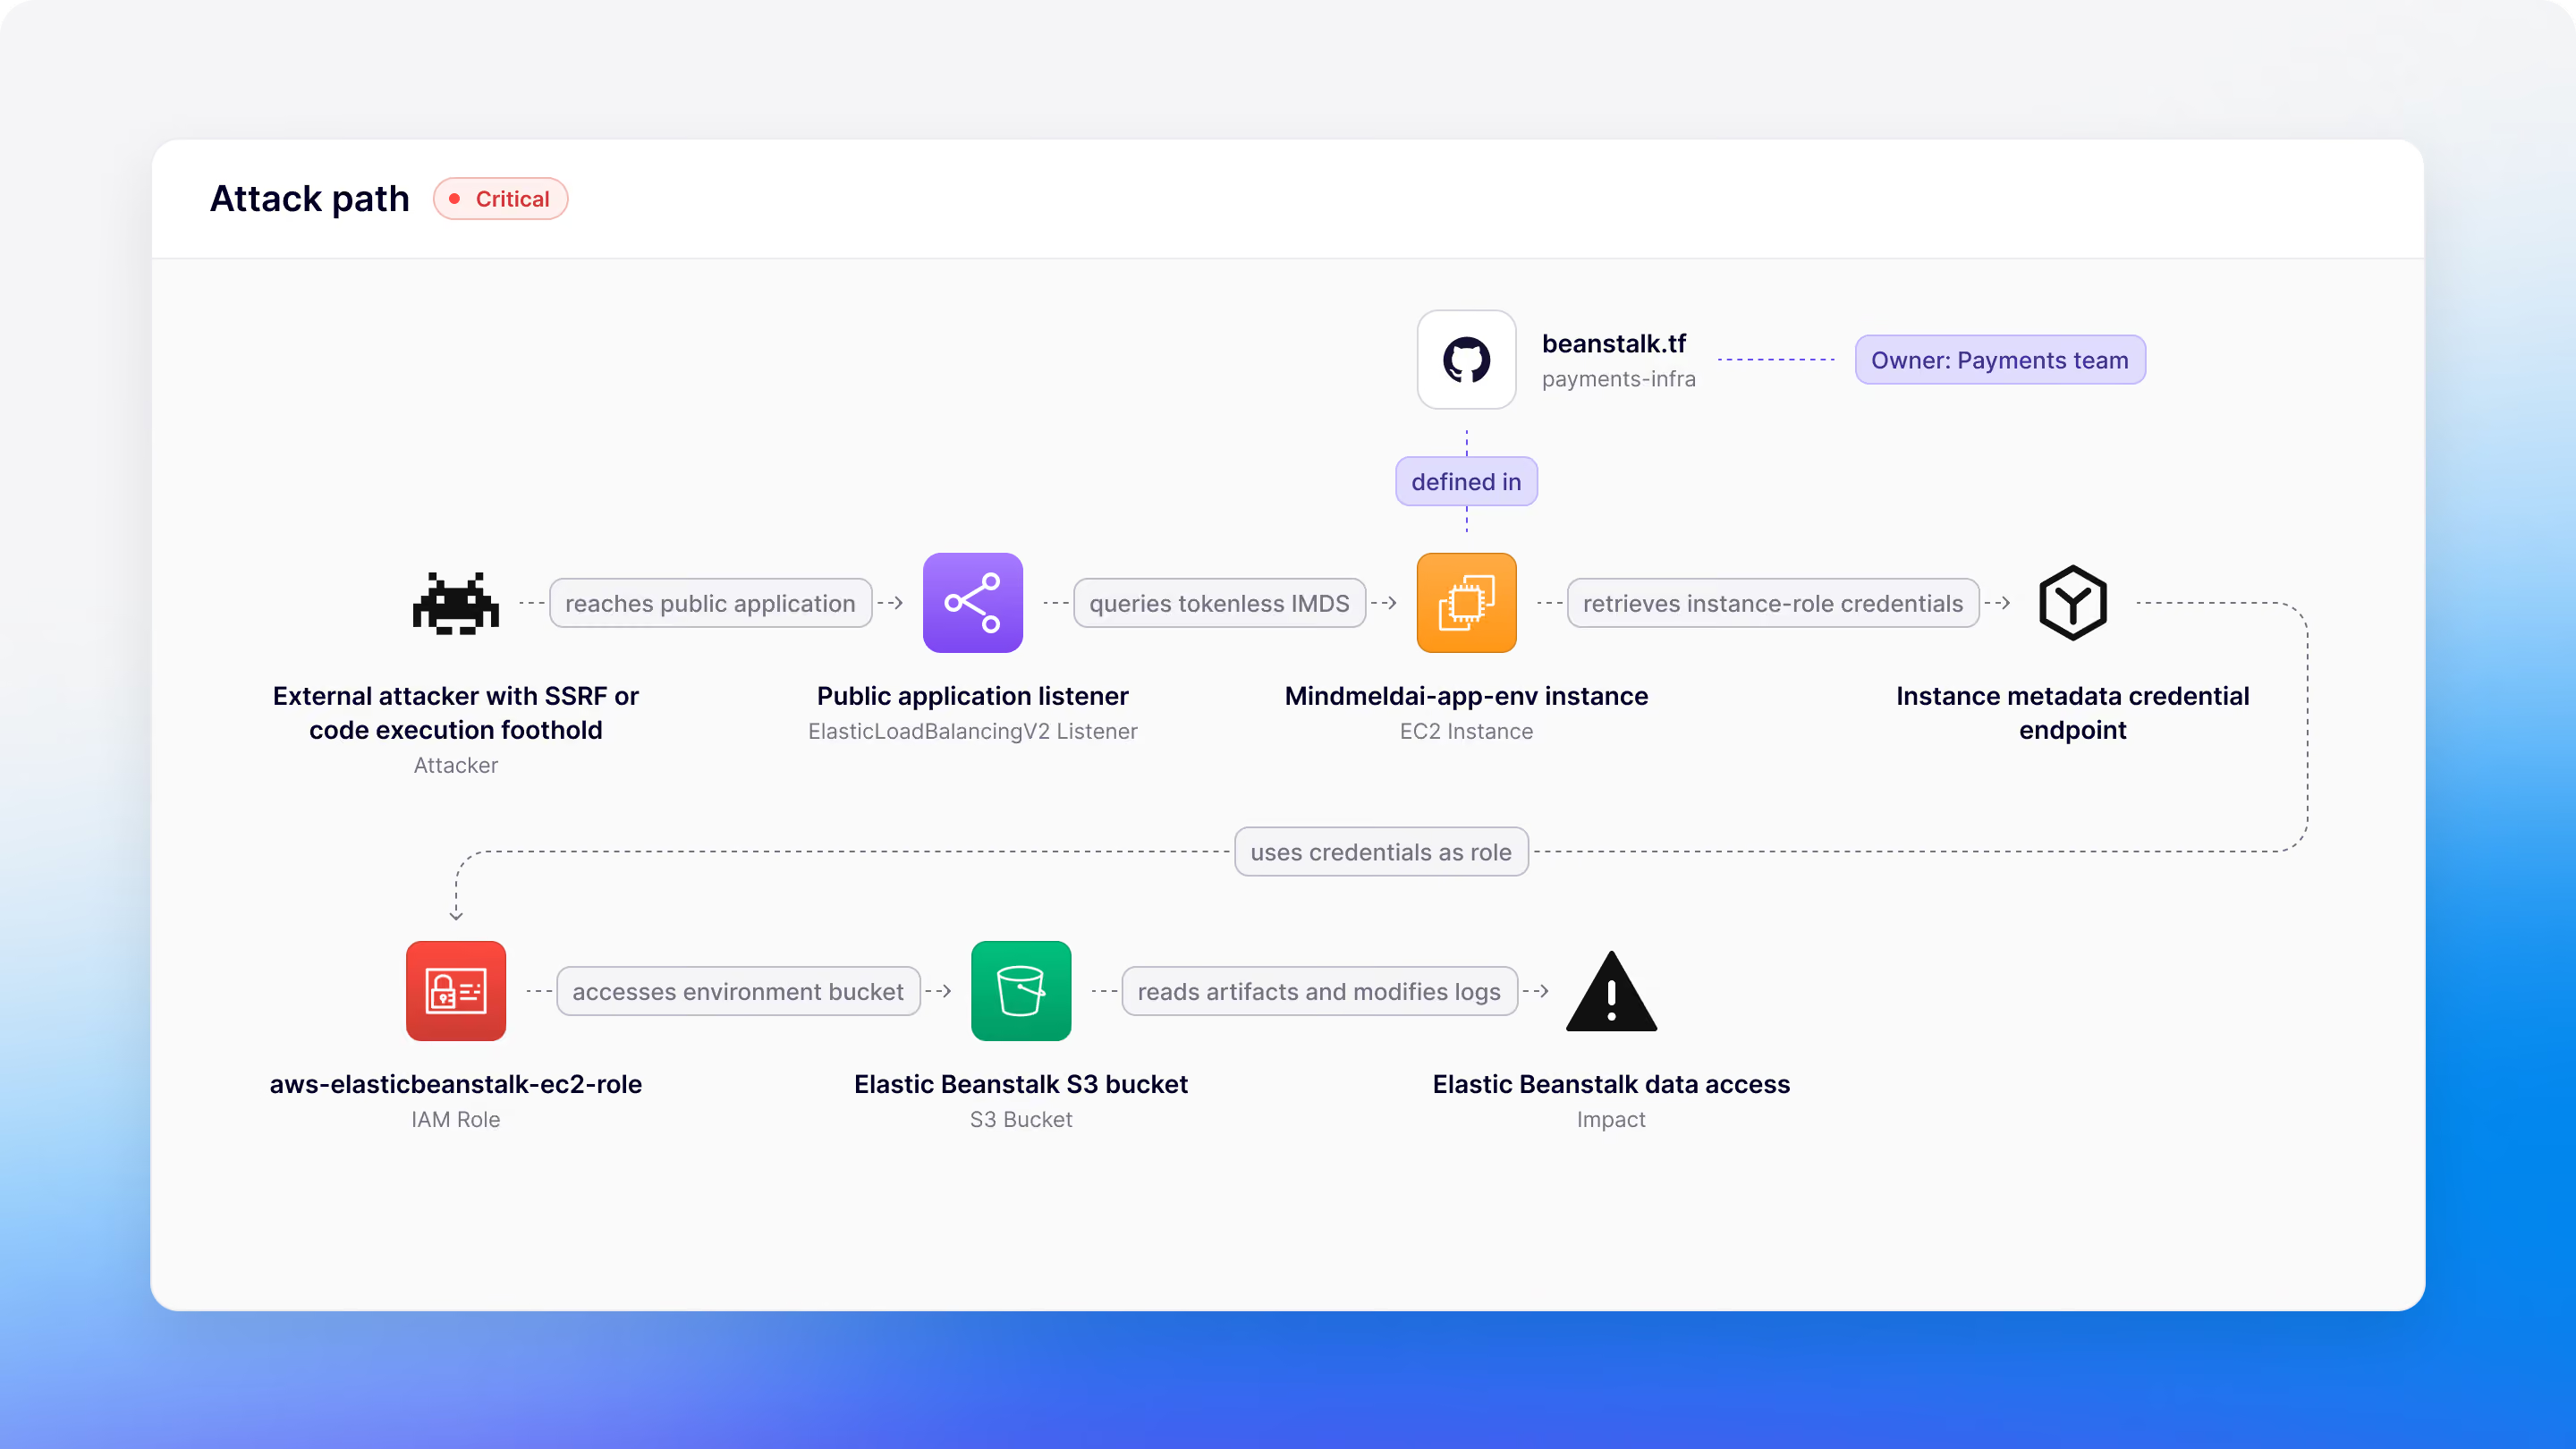
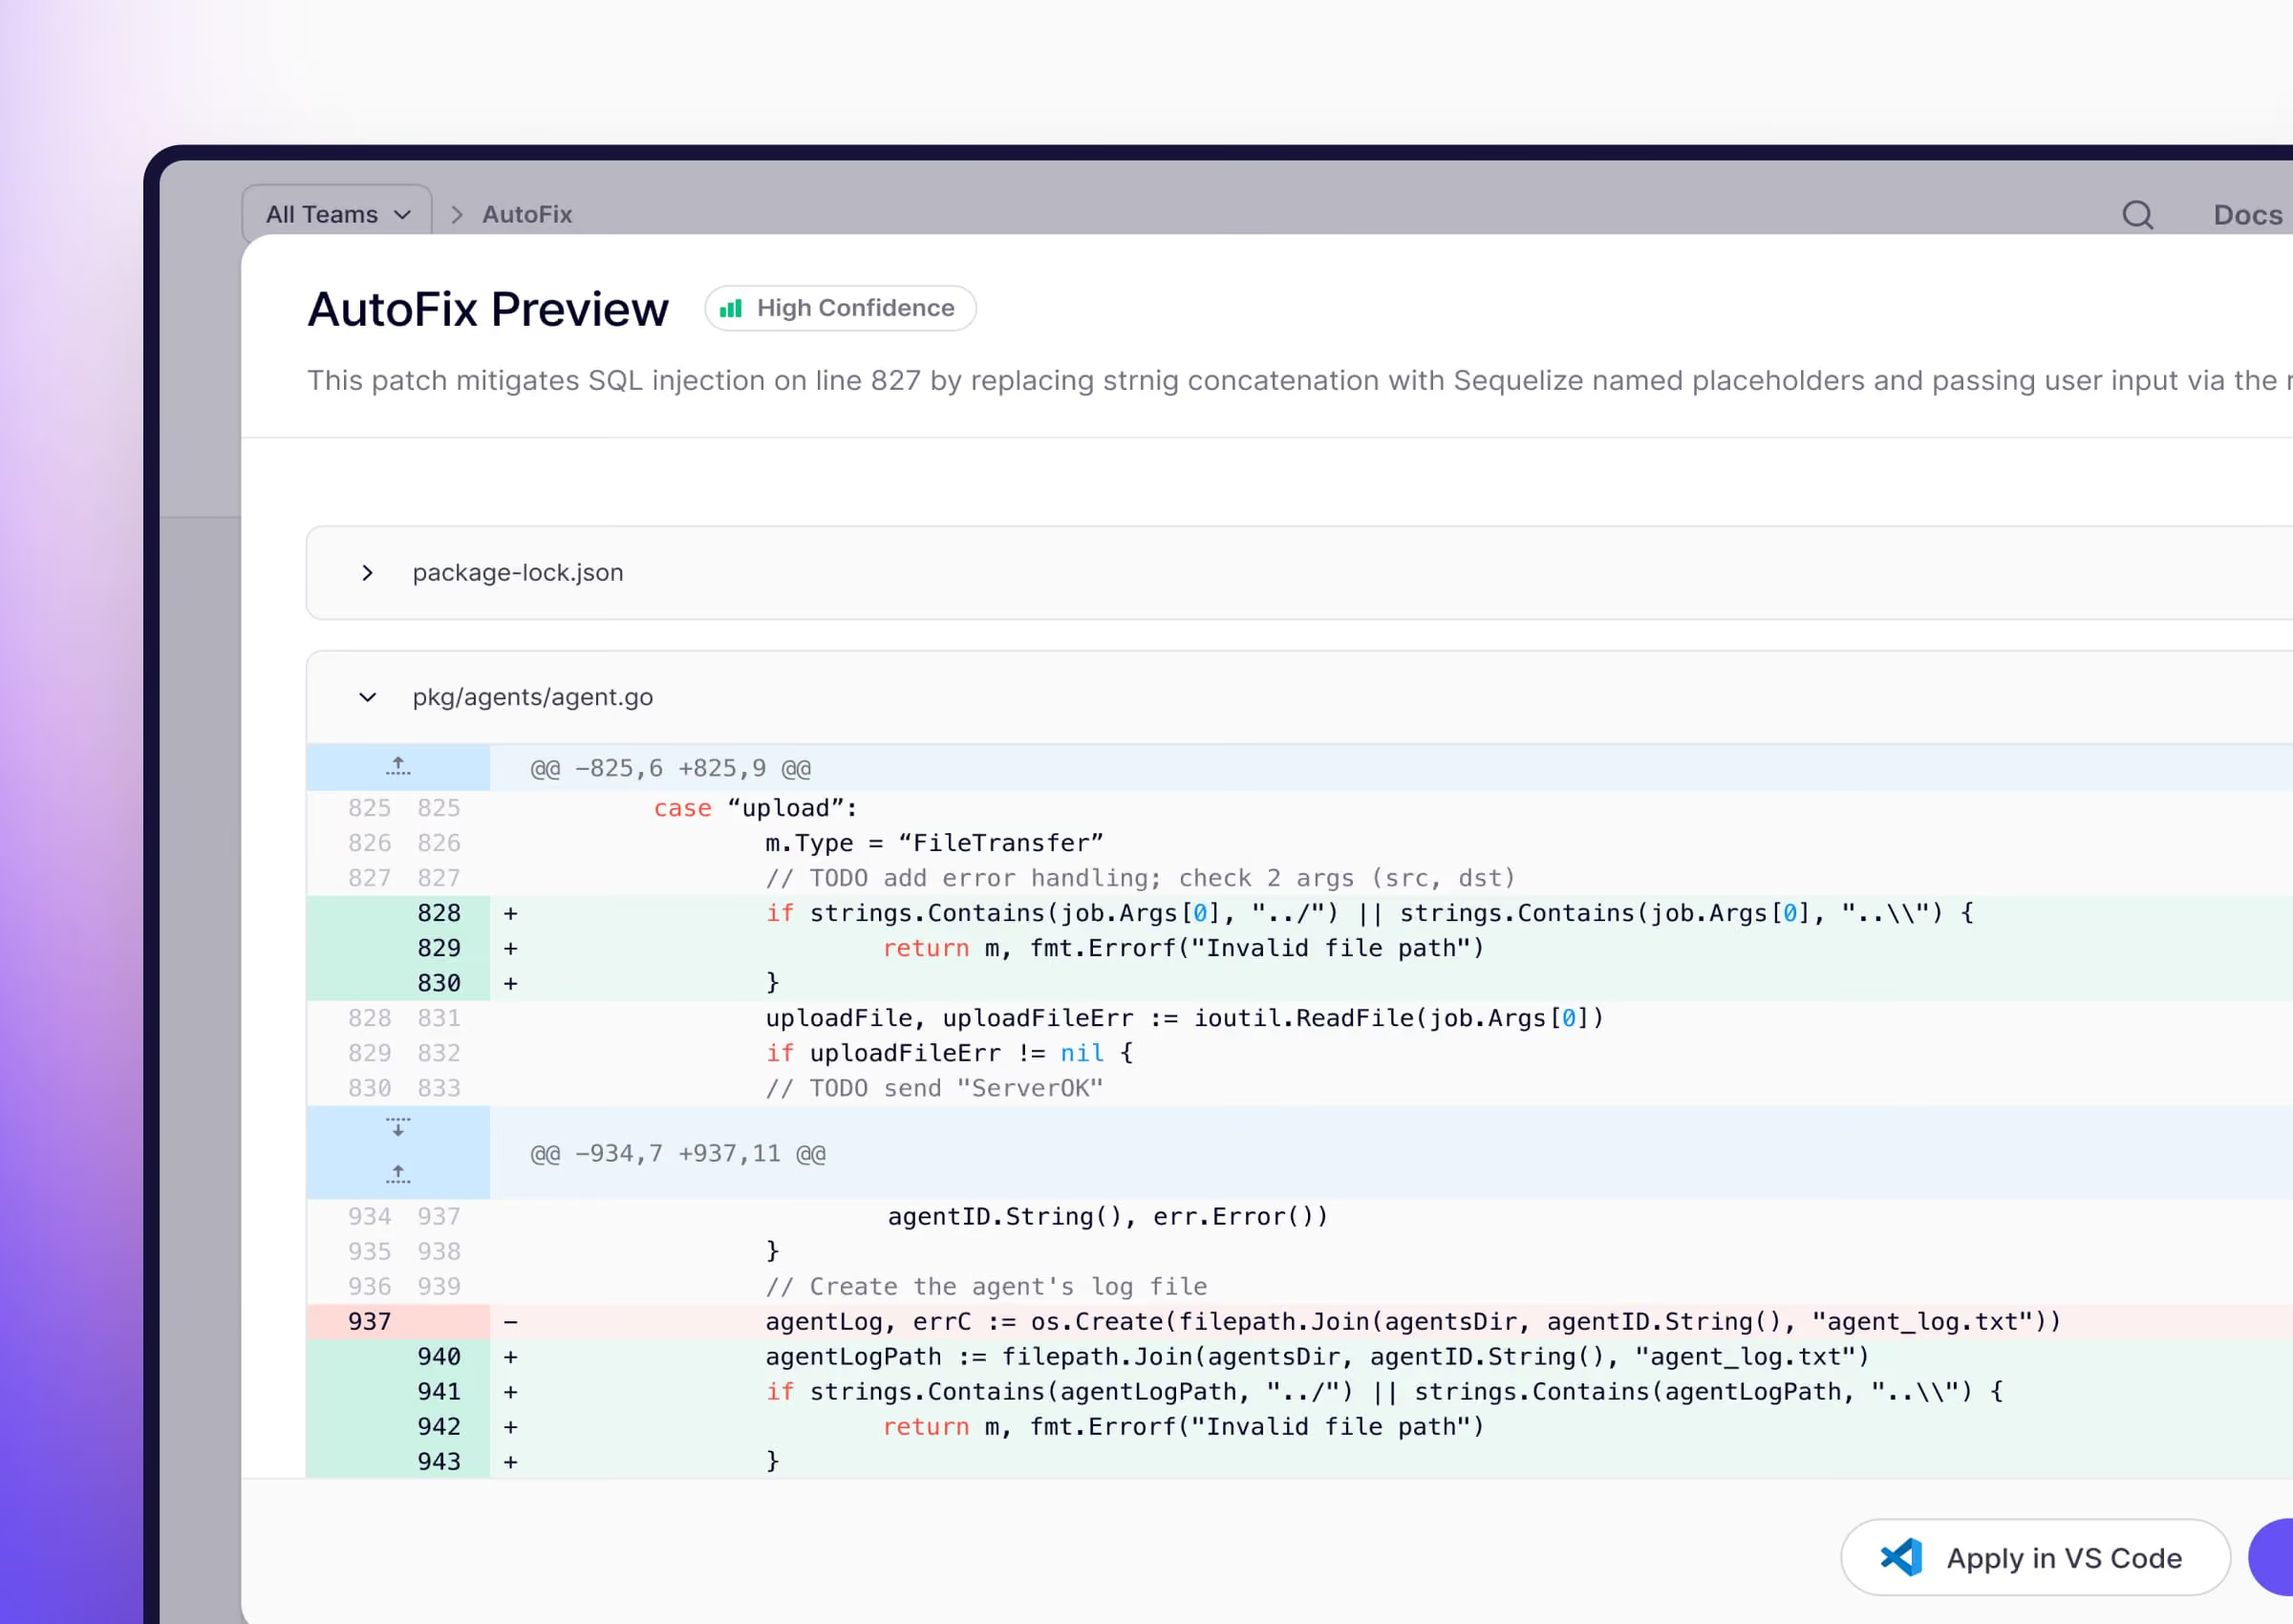





Cloud security that understands your application
Visibility across every cloud
One view of accounts, workloads, images and the connected code so you can instantly understand and assess risk.
Less effort to find and fix
Findings arrive in a ranked queue based on what attackers can reach. Fixes are sent to the right teams for review and deployment.
Fixes that stay fixed
Security issues are fixed in the source code so the next deploy doesn't reintroduce the same vulnerability.
"If you’re still patching manually, chasing people down to fix issues, and worrying about image upgrades, you’re doing it wrong. There’s a better, more automated way."
Ross HosmanCISO b.well Connected Health

“The fastest time we fixed a vulnerability was just 5 seconds after detection. That is efficiency.”
Aufar SukmajayaBack End Developer


Aikido vs Wiz


Stop chasing teams for cloud fixes
Aikido handles triage and hand-offs into your developer and agent workflows so issues are fixed and closed.
See everything you run
Connect your cloud in minutes and see every account, workload, and image in one searchable view.
Focus on what's reachable
Aikido maps each path from the internet to your instances, pods, ECS services and Lambda functions, and downgrades CVEs with no network path.
Know who owns each risk
Each image links to its repo and each cloud setting to its IaC template, so findings go to whoever owns that code.
Catch attacks in real time
Runtime Sensors flag container escapes and unexpected binaries on Kubernetes and Linux VMs, mapped to MITRE ATT&CK.
Built for devs. Trusted by security.
For Developers
For Security Teams
For CISOs
Get secure today,
quickly and for free.
Secure your code, cloud, and runtime in one central system. Connect a repo to discover what the reasoning agents find in your codebase.


FAQs about Aikido vs Wiz

Aikido covers posture and compliance, agentless VM scanning, containers, Kubernetes, IaC, attack paths and runtime threat detection, and sends each fix to the team that owns it. Aikido's data exposure checks work from code and don't check your live data stores. Infrastructure and Entitlement management are handled with Cloud Search and IAM checks along with Aikido's agentic Cloud Security Audit.
Aikido publishes pricing and plan limits for its free through advanced tiers. Custom quotes are available for larger teams, scoped to their exact needs. Wiz forces all custoemers into custom quotes.
Yes. Aikido connects to a cloud account in minutes with read-only access and without touching existing tooling, so many teams compare findings before deciding.
Aikido replaces Wiz Code's SAST, SCA, secrets detection, and IaC scanning with a natively built engine, rather than one that leans on a Checkmarx partnership for SAST and has no native DAST at all. It also adds AutoFix coverage across more finding types than dependency upgrades alone.
Aikido is SOC 2 Type II and ISO 27001 and ISO 42001 certified, and policy applies consistently across every connected repository and cloud account rather than varying by which module is licensed.
Plan limits count cloud accounts and VM scaling groups. An autoscaling group counts once however many instances it runs, so autoscaling doesn't change your price.
No. Aikido Images patch the base you already run. AutoFix an open the PR for your Dockerfile and images are pulled from an Aikido-maintained registry.
Not for cloud accounts or agentless VM scanning. Kubernetes scanning and Runtime Sensors use a lightweight read-only agent.
AWS, Azure, GCP, DigitalOcean, Alibaba Cloud, Oracle Cloud, Render, and Supabase.
Aikido is SOC 2 Type II, ISO 27001, ISO 42001 certified, and policy applies the same way across every connected repository and cloud account. You can learn more on the Enterprise use case page.