Software Security for Government & Public Sector
Uphold citizen trust, ensure compliance, and drive secure innovation across public services with our unified security platform for agencies & their contractors.
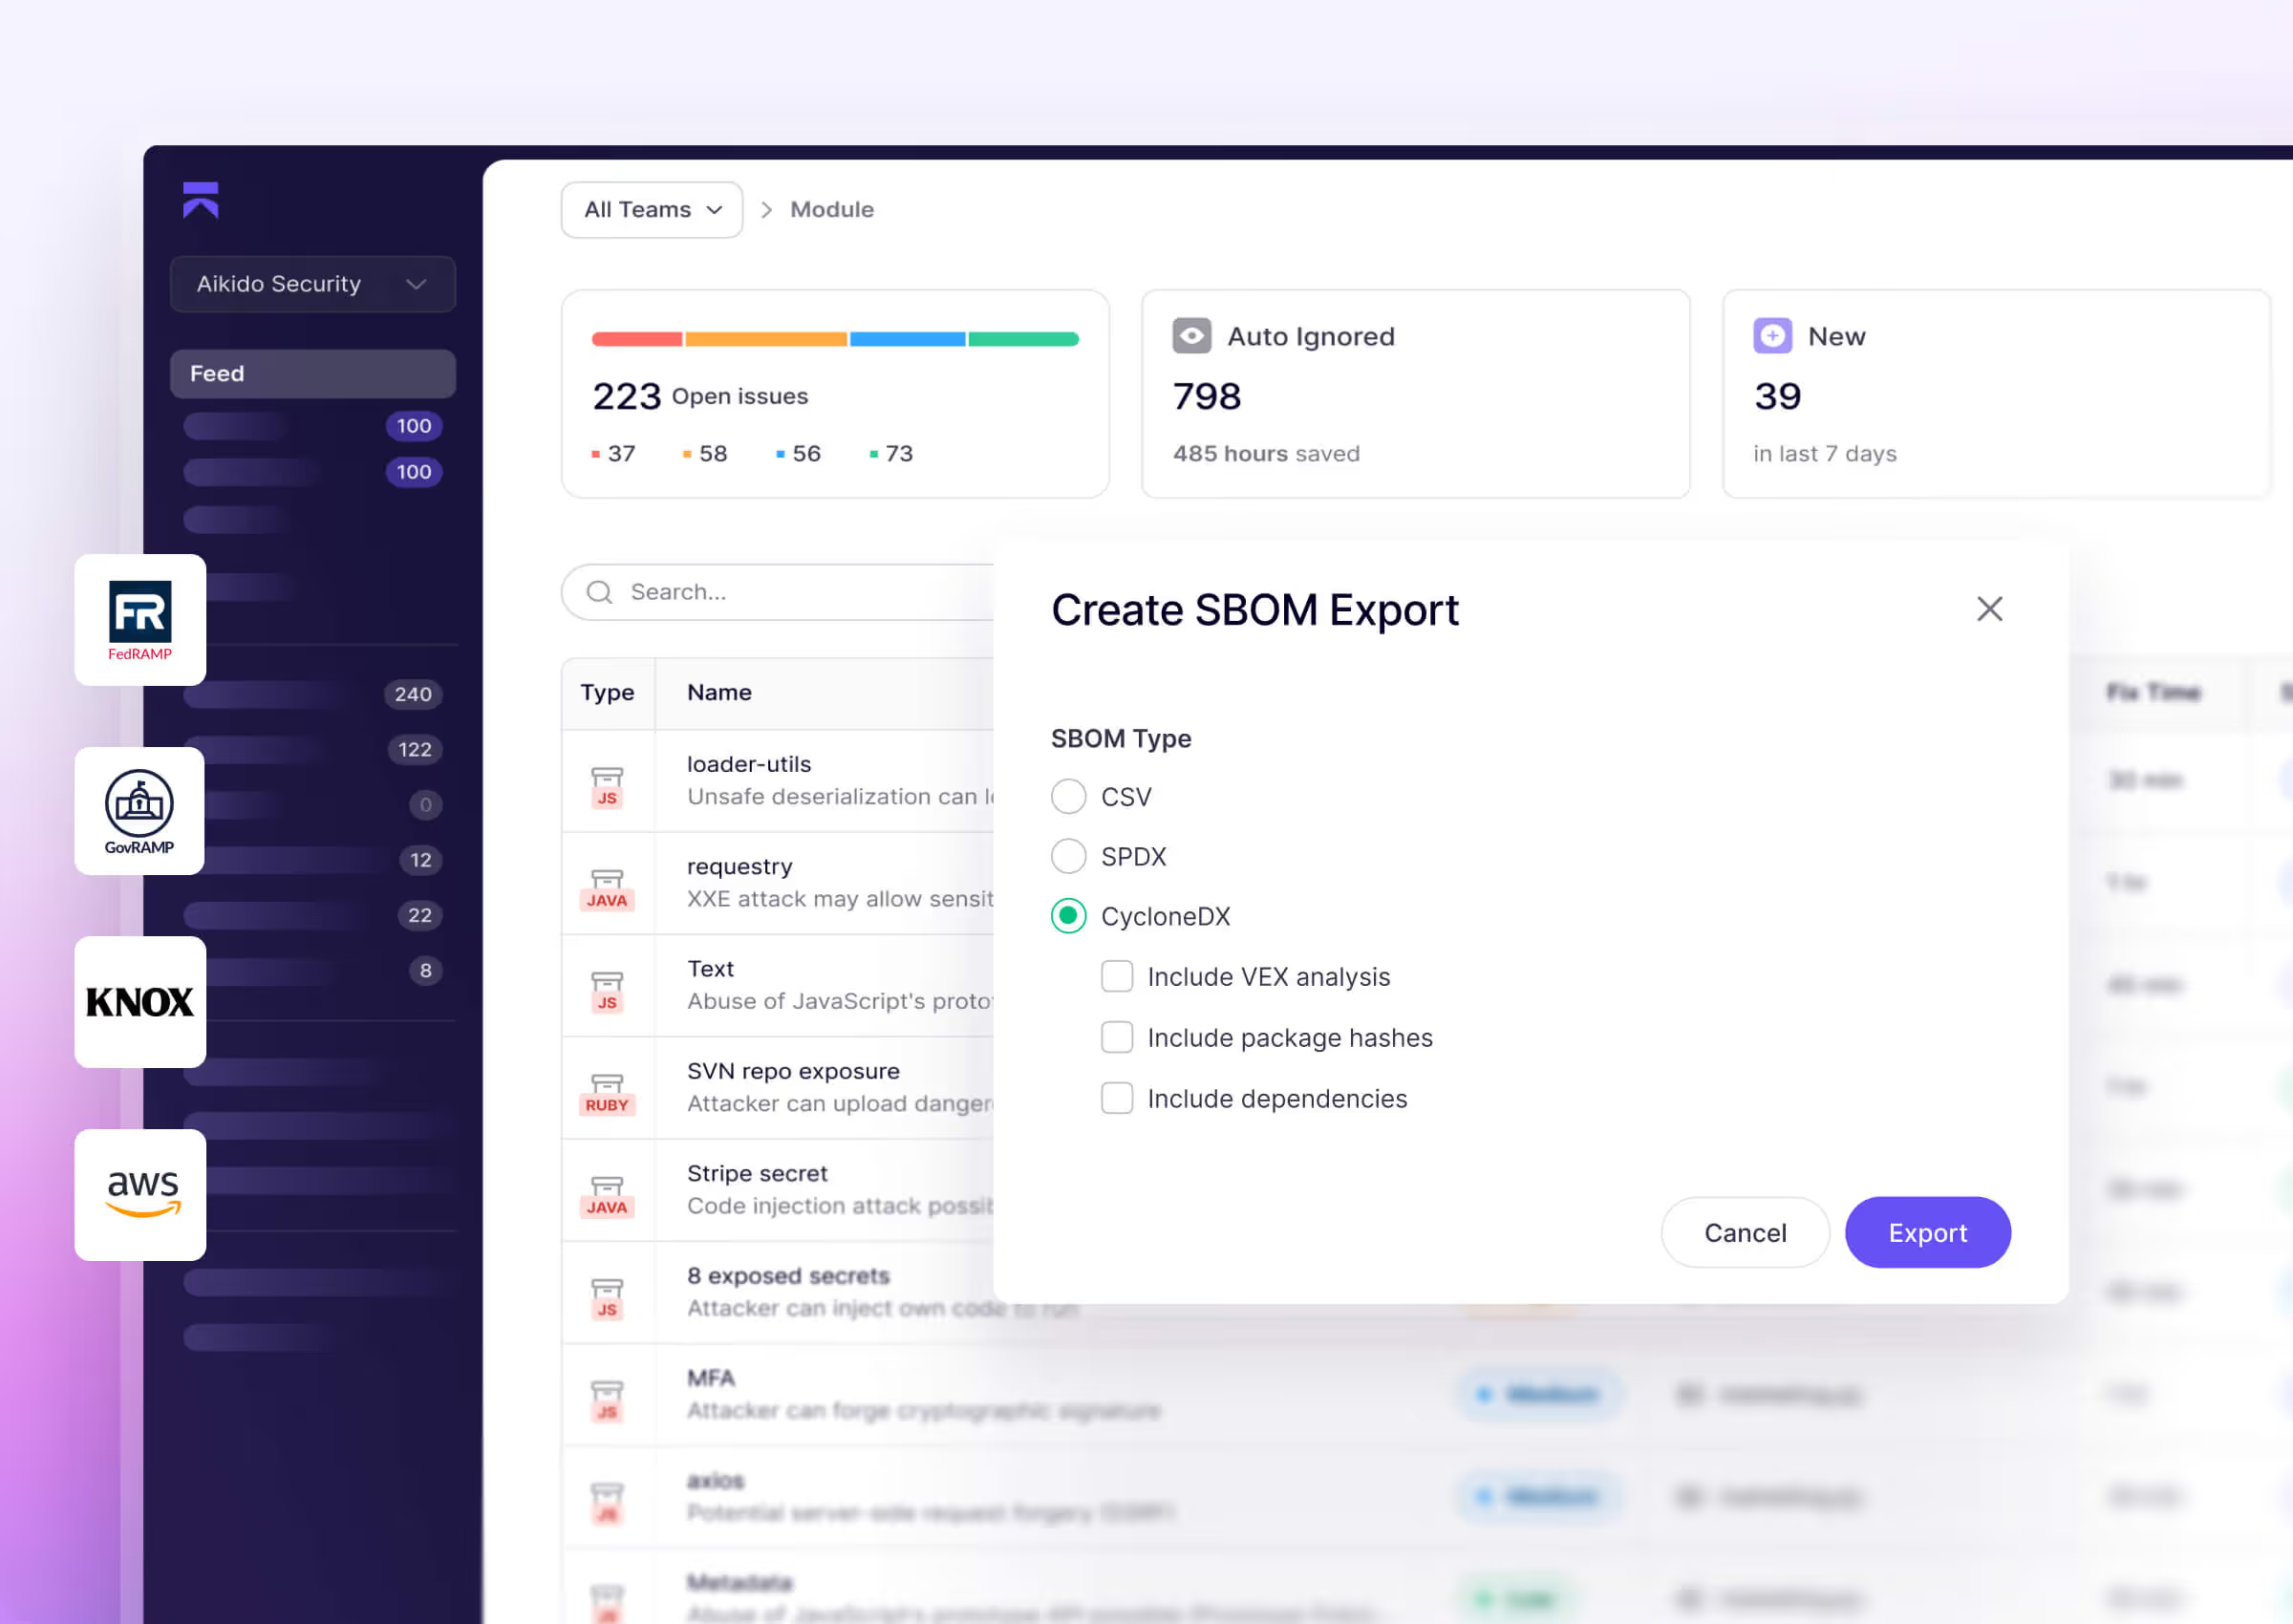
Continuous scanning across code, dependencies, containers, IaC & cloud with an SBOM for every application
KEV-first: known exploited vulnerabilities go to the top of the queue
Hosted, on your infrastructure, or fully air-gapped options
SOC 2 Type II · ISO 27001:2022 · ISO 42001 · FedRAMP Moderate


Built for public bodies and the contractors that serve them
Public services run on the same open-source code, pipelines and cloud as any tech company, and they face the same attacks. Aikido gives government teams the security tooling leading engineering teams use, with the evidence trail auditors expect.
National & local governments
Contractors and system integrators delivering public services
Public agencies, research institutions, and public-private innovation hubs
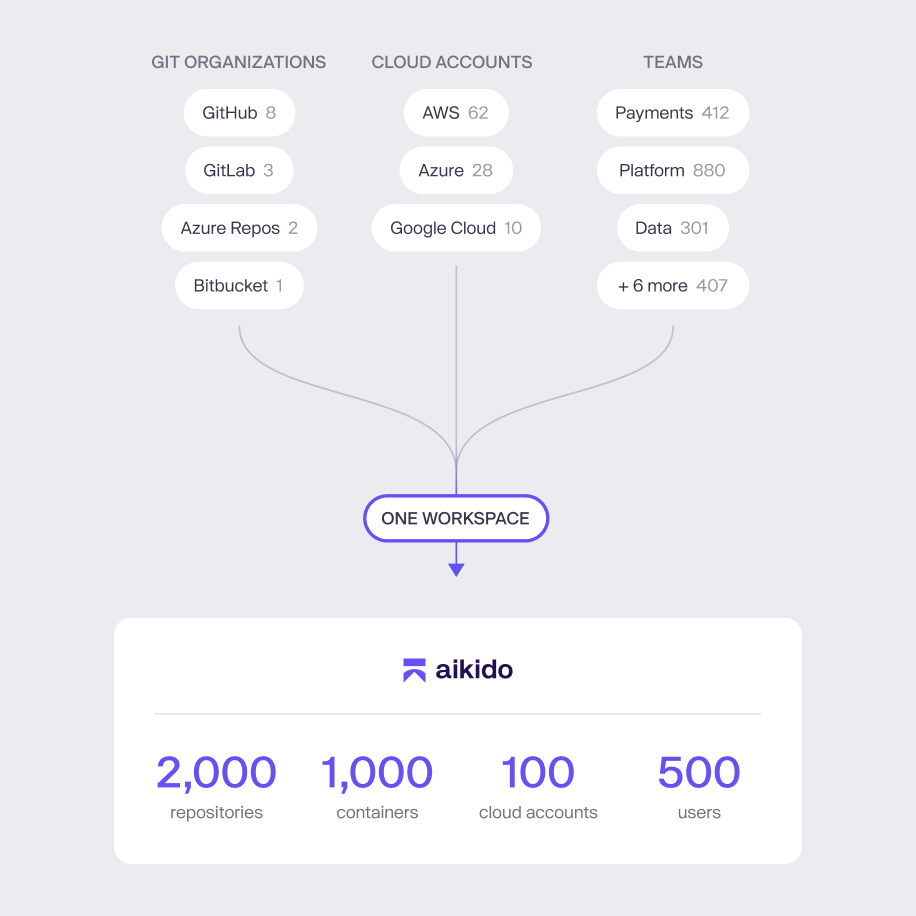
Purpose-built for public sector workflows
Government agency, research institution, or certified contractor. Aikido integrates seamlessly with the stack you already run.
Meet the mandate: Continuous monitoring and evidence aligned to national, regional and local government requirements.
Prove it fast: Export audit-ready reports for auditors, assessors and accreditation reviewers in minutes.
Ship without friction: Developer-first workflows in GitHub, GitLab, Bitbucket, Azure DevOps, and CI/CD.
US federal: FedRAMP certified at Class C (Moderate), hosted in AWS GovCloud.
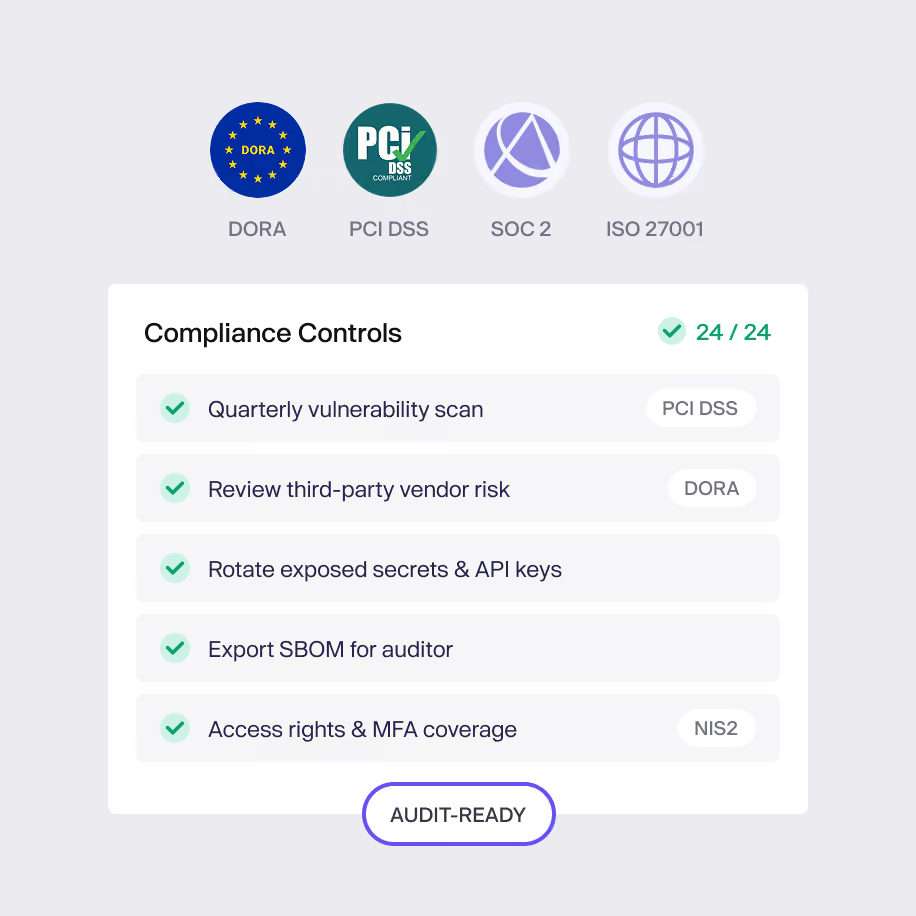
Hassle-free compliance
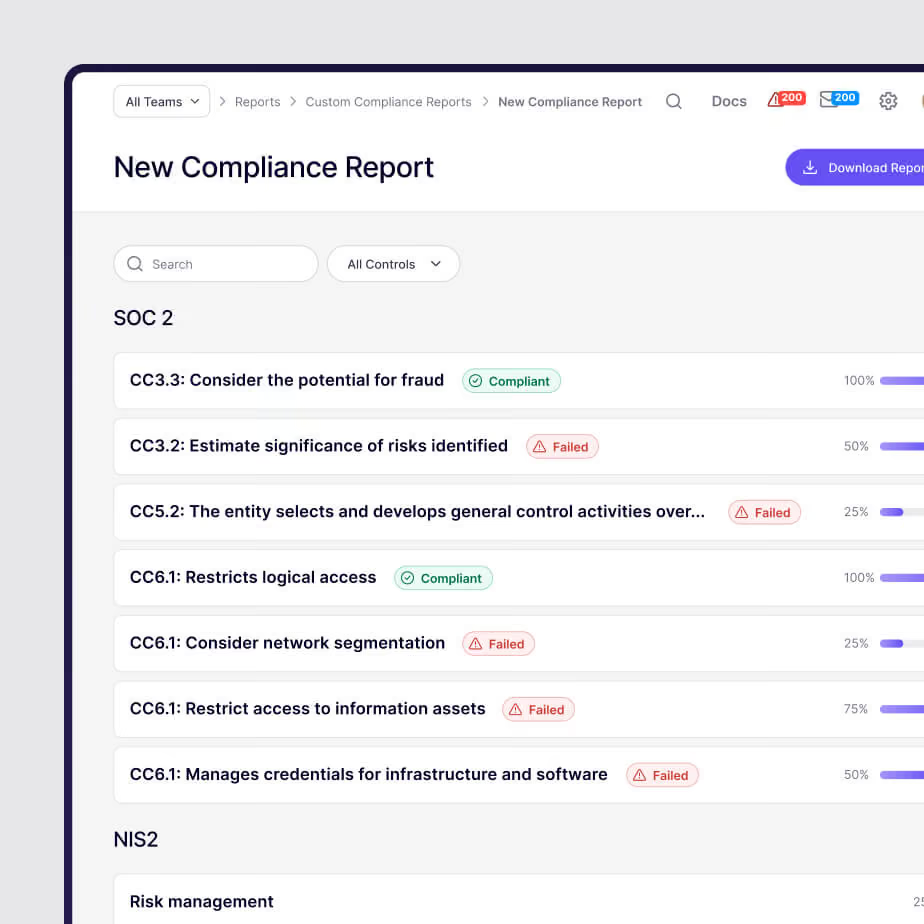
Whether you answer to ISO 27001, NIST or a national framework, compliance is table stakes in the public sector. Aikido maps findings to the controls you're audited on and keeps the evidence ready.
Automate SBOMs, OSS license checks, and audit-ready evidence
Map findings to NIST SP 800-53 (including RA-5), SOC 2, and ISO 27001
Deliver clear proof to partners, auditors & regulators
Cut compliance overhead with built-in controls and reporting
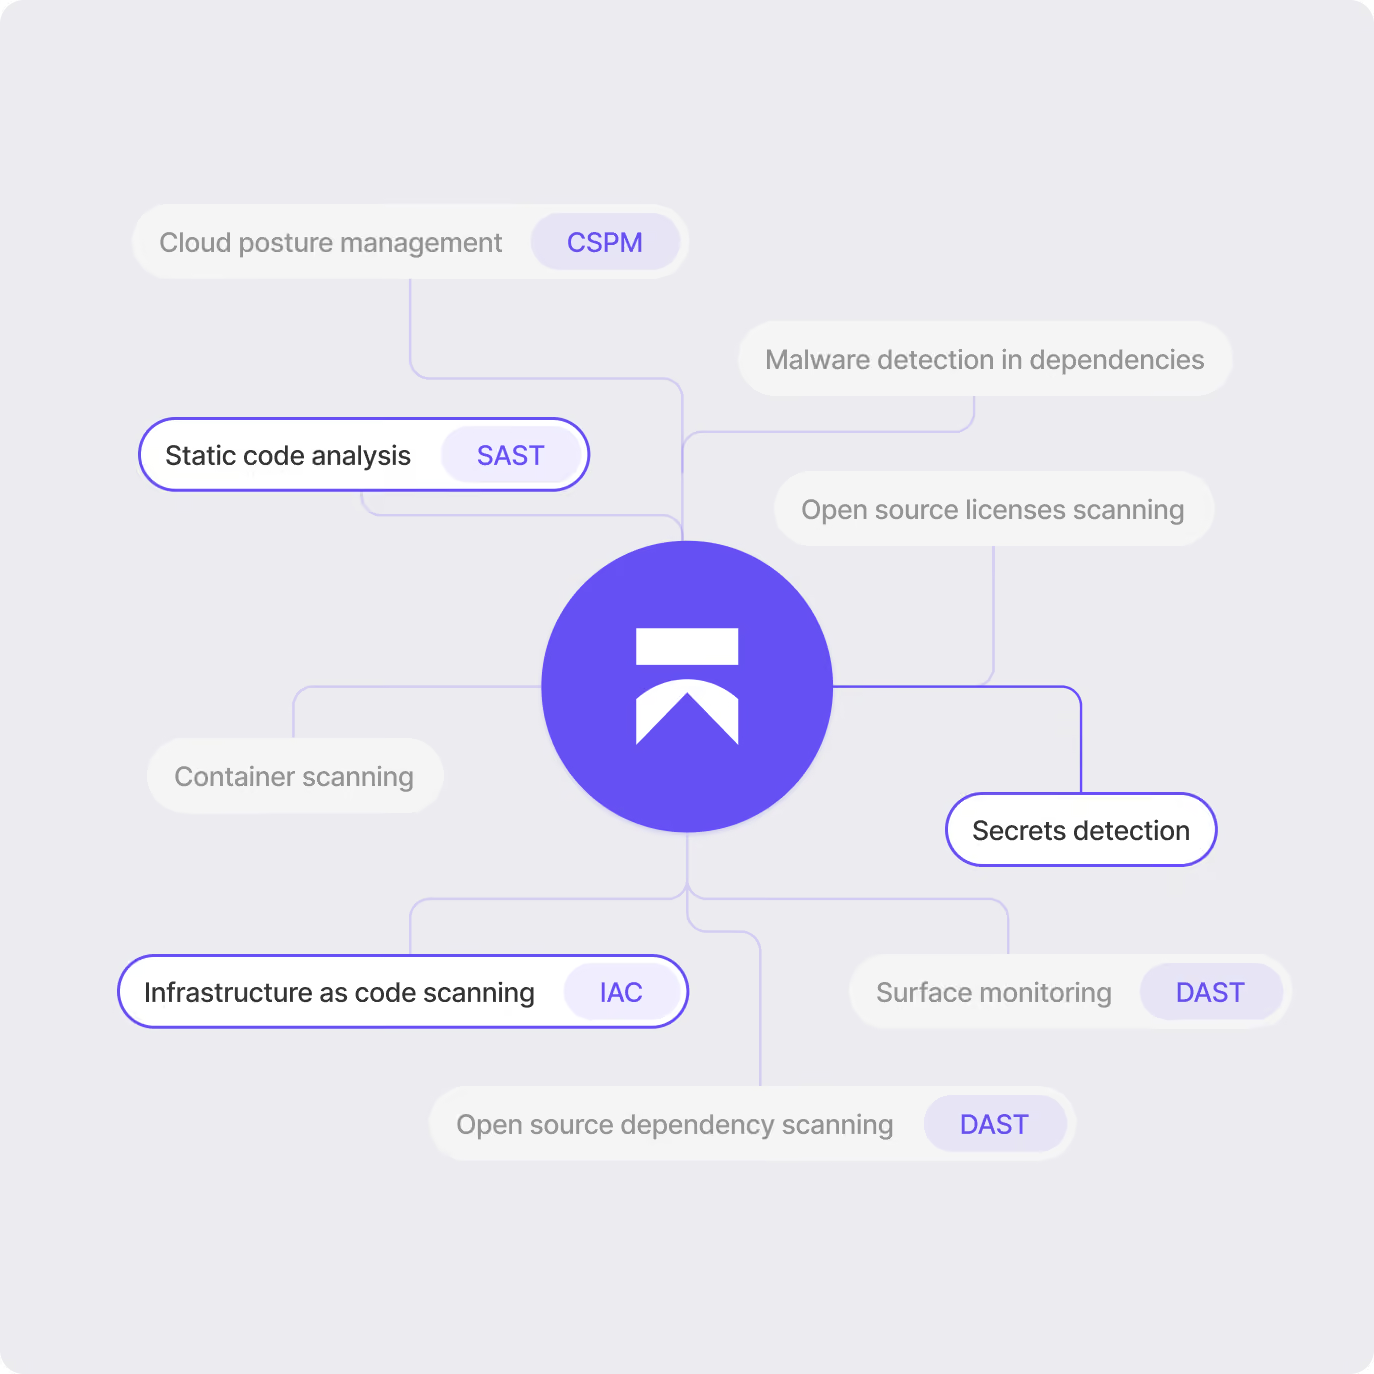
Known exploited and reachable vulnerabilites go first
In the public sector, credibility is everything. Aikido helps you meet the highest security standards without slowing delivery.
KEV first: Known exploited vulnerabilities go to the top of the queue, so teams fix what attackers are actually using.
Code to cloud: SAST, SCA, secrets, IaC, containers and cloud security, triaged into one prioritized queue
95% less noise: Fewer false positives, faster remediation, more developer time back.
AI pentesting entirely under your control
Continuous AI pentesting that keeps your code on-prem.
Finance, healthcare, and pharma ship constantly, but compliance expects regular pentesting and your code can't leave the network. The Aikido Machine continuously pentests every deployment, validates exploitability, generates patches, and retests the fix.
- Your data stays local
Source code, customer records, and findings never leave your network, which is what makes white-box testing possible for a bank or hospital.
- Nothing to ration
Inference runs on the Aikido Machine's own GPUs at no token cost.
- Findings auditors accept
Every result ships with the traces to reproduce it, so you hand over a confirmed issue instead of a maybe.
Autonomous pentesting for networks that never touch the internet.
Classified and mission systems can't send code to a cloud, and often can't let outside operators near them at all. The Aikido Machine runs entirely inside your enclave, air-gapped, with its own models on its own hardware, so nothing leaves the network.
- Fully air-gapped
The Aikido Machine runs with no outbound connection at all, and updates can also load from a separate device, so even patching stays off your network.
- No operator bottleneck
Testing is autonomous and runs on your hardware, so you're not waiting on external pentesters to be scheduled and cleared.
- Built for disconnected sites
Aikido’s AI pentesting stack and the models it needs run locally, reaching locations that cloud tools can't.
Test critical systems without citizen data leaving.
Government systems hold people's personal data and tend to run for decades. Rules like GDPR and FedRAMP often mean that data has to stay in the country and off the public cloud, which rules out most AI pentesting tools. The Aikido Machine runs entirely on your own infrastructure, so you get it without sending anything out.
- Data stays in jurisdiction
Code, data, and findings never leave your network, so there's no question of where they're processed or which country they land in.
- Meets your testing mandates
FedRAMP, NIST 800-53, and CMMC all require regular penetration testing. The Aikido Machine runs it continuously on your own hardware, so you stay covered without booking an outside pentest every cycle.
- Works with legacy stacks
The Aikido Machine tests modern and older systems alike, including languages like COBOL that a lot of public infrastructure still runs on.
- Predictable to budget
One annual fee covers hardware, software, support, and repairs, with no per pentest or token costs to forecast mid-year.
Multiple Deployment Options
Commercial SaaS
Free - Enterprise offerings
Regulated SaaS
FedRAMP
Sovereign Deployments
US/EU
NIST 800-171 Support
Air Gapped
On-premises

"What Aikido offers is observability. We can put a number on our security posture, and that gives us a defined roadmap for where we go next."
Walid MahmoudSenior DevSecOps Engineer
Aikido's features
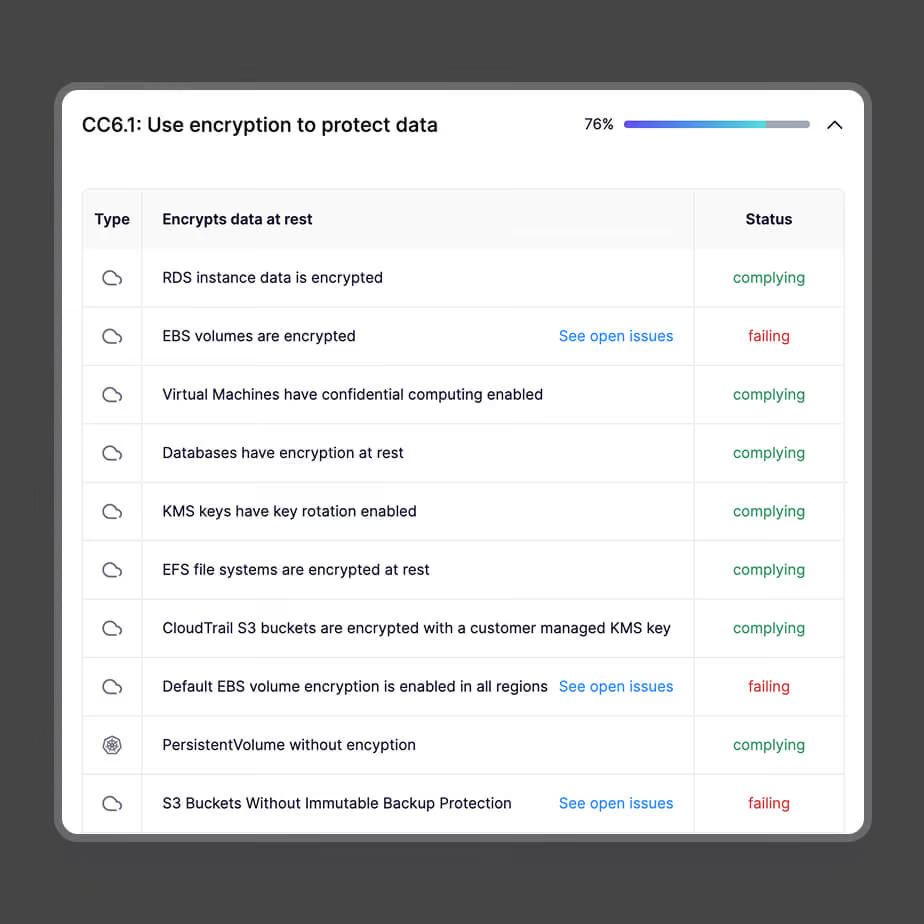
Compliance automation
Map findings to SOC 2, ISO 27001, OWASP Top 10, and NIST SP 800-53 (RA-5), and export audit-ready evidence in a few clicks. Compliance collects in the background while your team keeps shipping.
Evidence on demand: SBOMs, RA-5 findings, and compliance reports, exportable anytime.
Mapped to the mandate: Findings tie directly to the controls reviewers ask for.
No manual export round: Reports generate themselves. No spreadsheet wrangling.
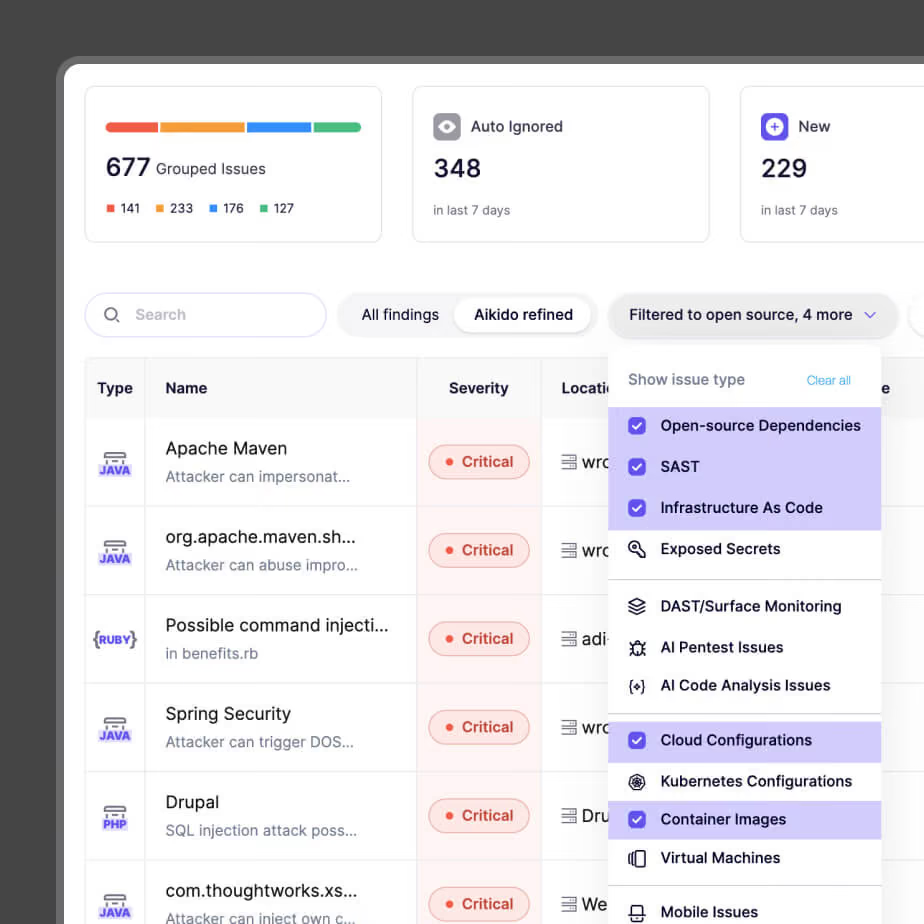
One view from code to cloud
Agencies get one view across everything they build and run, and one source of evidence. Aikido combines cloud posture (CSPM), SAST, SCA, secrets, IaC, and containers in one platform, so agencies get one view across everything they build and run, and one source of evidence.
Code to cloud: One platform across the whole SDLC and your cloud footprint.
Reachability-aware: We flag what's actually exploitable, and silence what isn't.
One control owner: No stitching five point tools together.
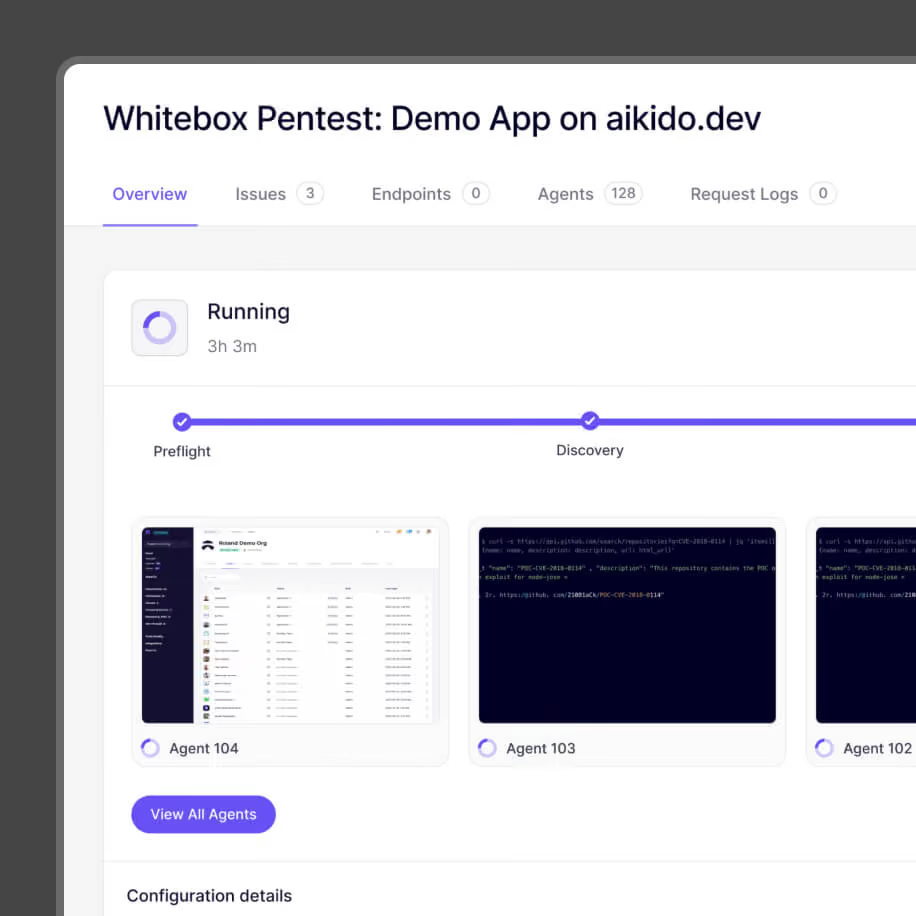
AI Pentest
Run a pentest with AI agents and get an audit-grade report in hours, not weeks.
Hours, not weeks: Audit-grade results without the scheduling lead time.
Runs on-prem too: The Aikido Machine keeps pentesting inside air-gapped and high-impact environments.
Proof included: Reviewable findings you can hand to auditors.
Frequently Asked Questions

Aikido maps findings to NIST SP 800-53 (including RA-5), SOC 2, and ISO 27001, and has achieved FedRAMP Moderate Authorization.. Agencies and contractors get audit-ready evidence exports.
Yes. SBOM, SSDF alignment, and attestation-ready evidence flow through one platform. Contractors prove what they ship, agencies verify it.
No. Scans run in temporary containers destroyed after analysis. Read-only access, always.
Yes. The Aikido Machine runs the full platform on-prem, including AI pentesting. Local scanners cover CI-only setups. Nothing leaves your boundary.
Aikido supports GovRAMP and state frameworks. Continuous monitoring and evidence exports map to the controls state reviewers ask for.
Get secure now
Secure your code, cloud, and runtime in one central system.
Find and fix vulnerabilities fast automatically.