
Code-to-cloud security for the public sector
Aikido finds and ranks exploitable vulnerabilities across code, containers and cloud on every change, then fixes them for you. Automate ConMon evidence and keep your POA&M from growing.
FedRAMP Certified: Class C (Moderate)
Continuous RA-5 scanning per commit, not quarterly
Deployable in AWS GovCloud and US-Gov-East
Trusted by public agencies and government tech providers

Multiple deployment options
FedRAMP (cloud)
Aikido for Government SaaS in a FedRAMP-authorized environment. It's the fastest route for agencies and contractors that use authorized cloud infrastructure. Nothing to host or maintain on your side.
Hybrid
Fully on-prem: The complete platform for IL5+, air-gapped & classified-adjacent environments.
Air-gapped
The platform runs inside your network, including AI pentesting with Aikido Machine. Built for IL5+, classified-adjacent, and sovereign environments, with NIST 800-171 support.
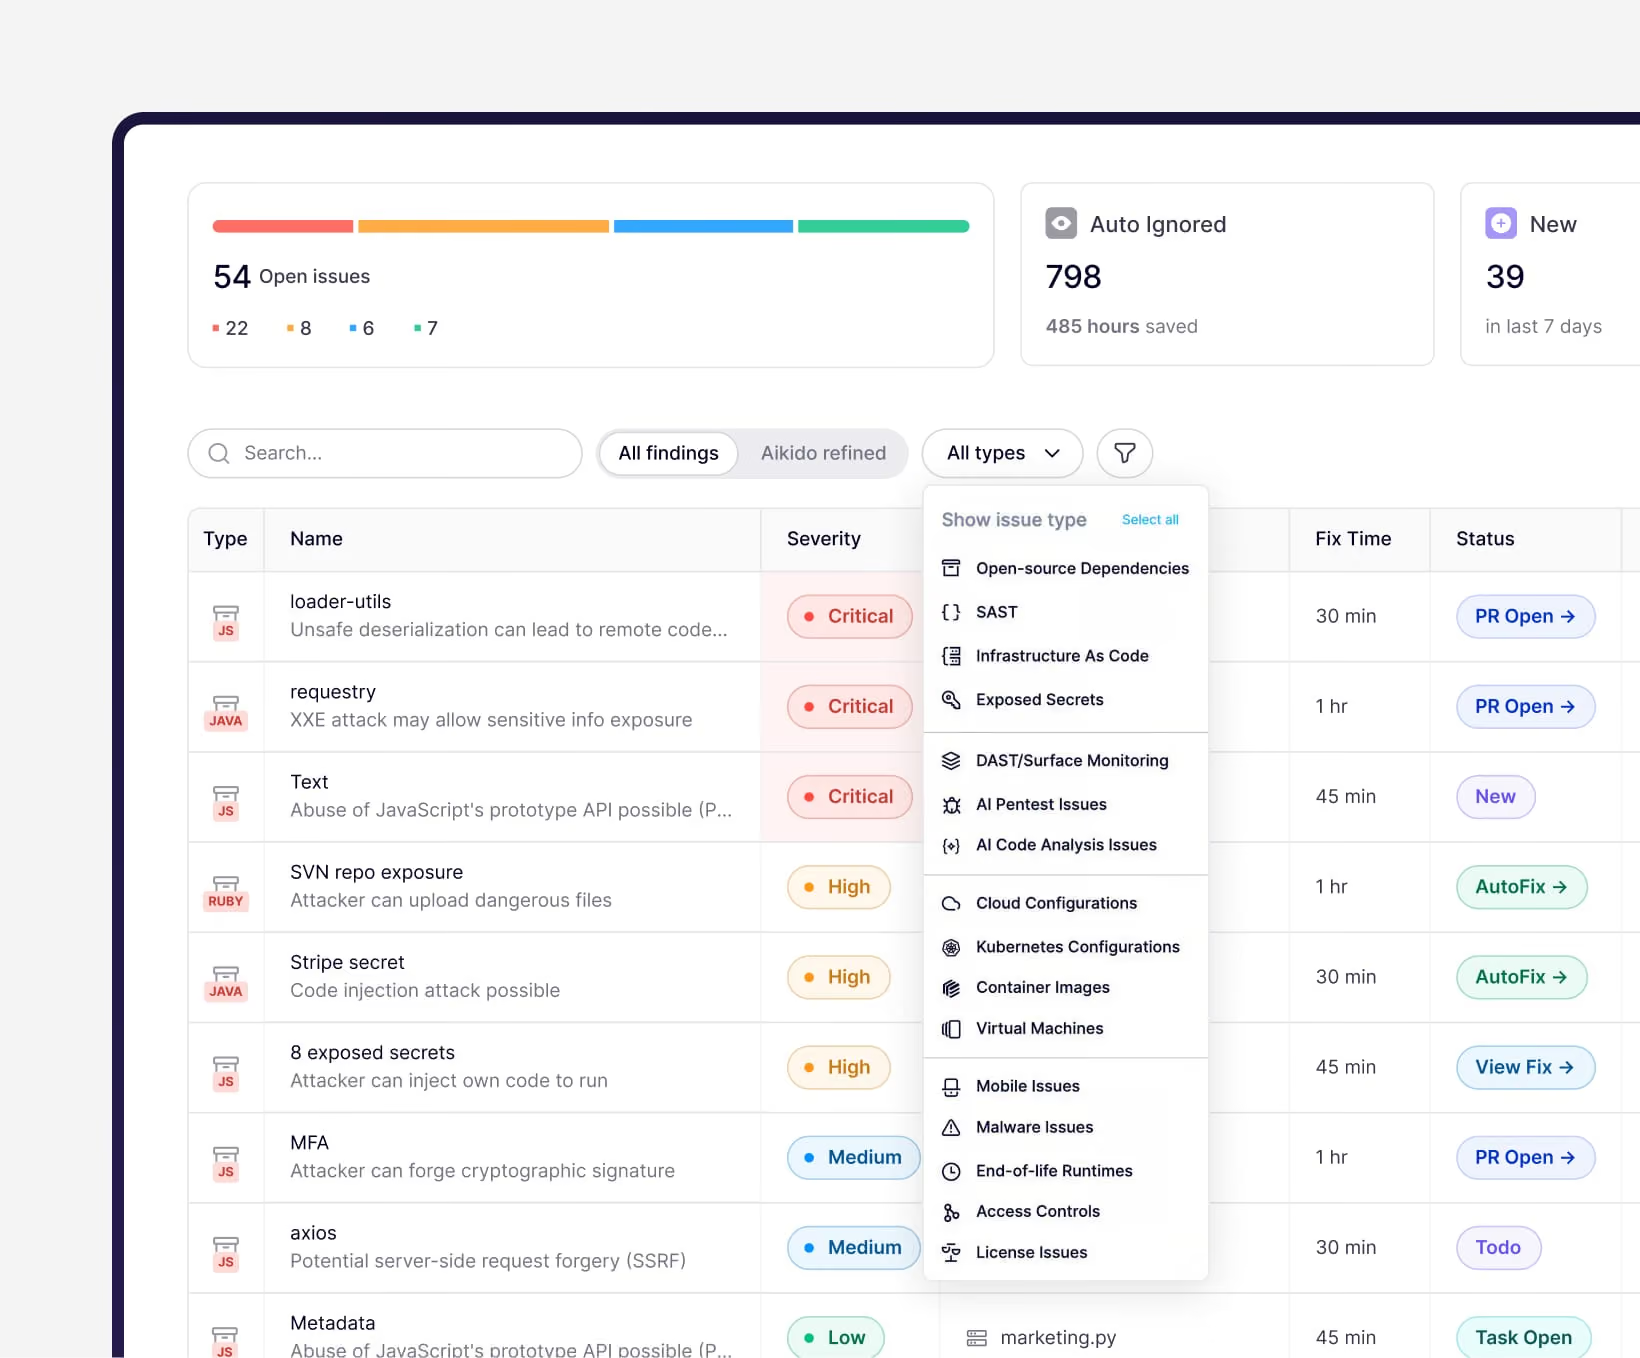
RA-5 vulnerability scanning, built into the way you ship
Your agency gets continuous, code-to-cloud scanning aligned to RA-5. Assessors get the evidence. Developers keep shipping
What your agency gets
Aikido is purpose-built for high-trust environments where compliance
and operational integrity are non-negotiable.


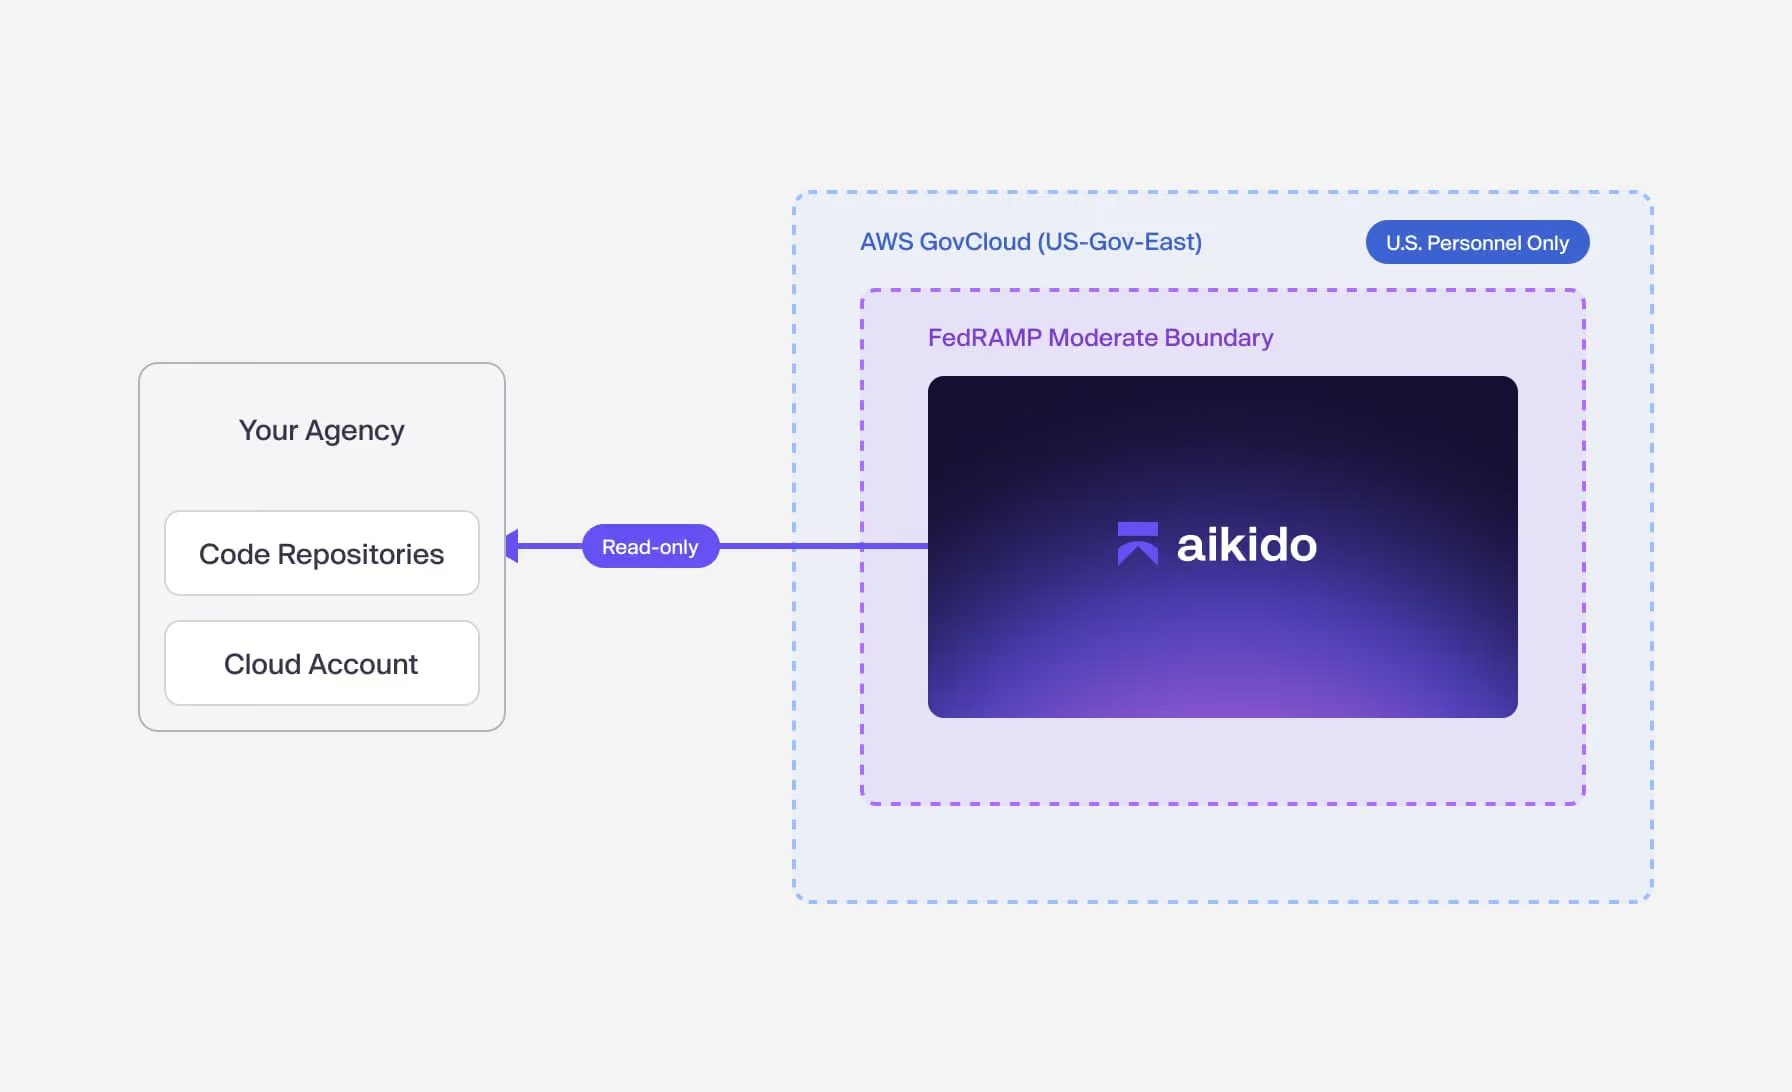
FedRAMP Certified: Class C (Moderate)
Aikido is FedRAMP Certified at Class C, the level for systems handling controlled unclassified information. Agencies can request our certification package through the FedRAMP Marketplace and use it for their own authorization.
Get your own system certified
Aikido generates the vulnerability evidence for your 3PAO assessment and ongoing certification, from the scans you already run.
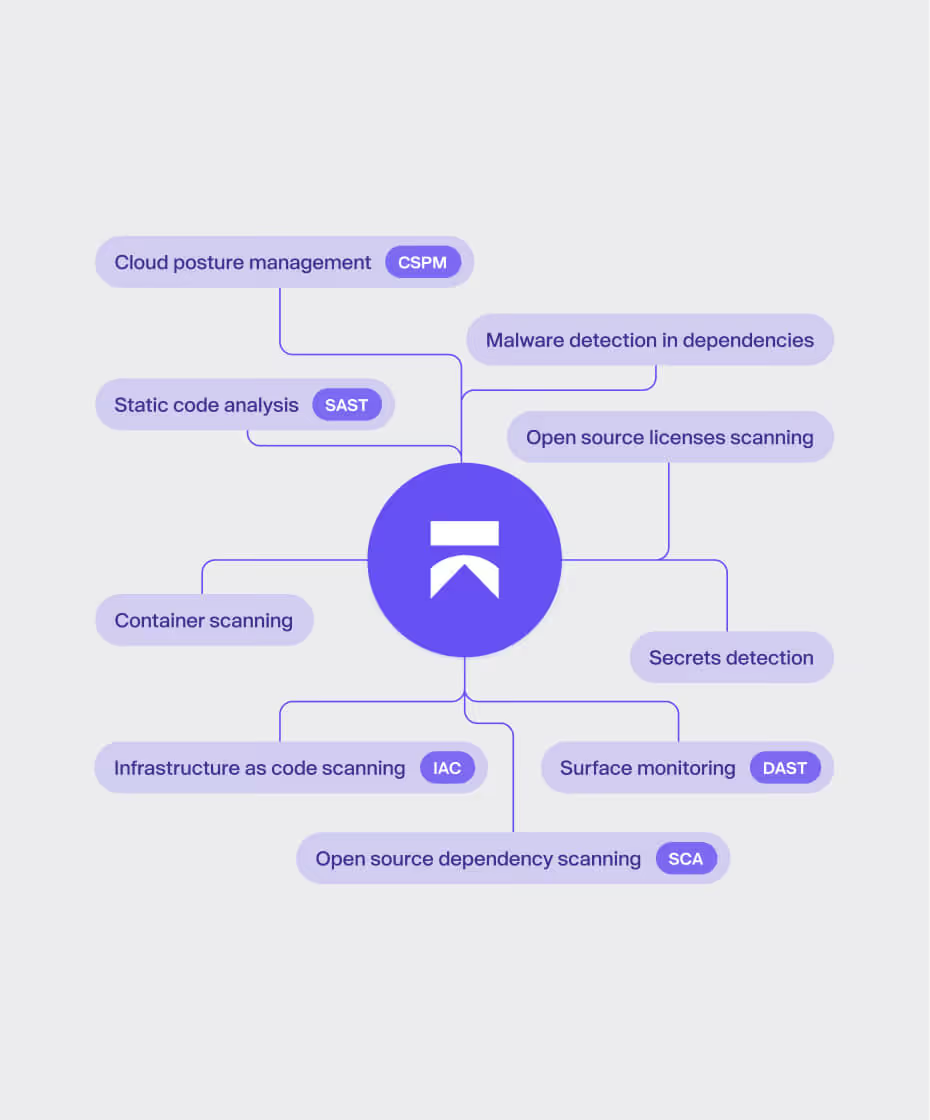
Get certified faster
Scan code, dependencies, containers, IaC, and cloud in one platform. Featuring SAST, DAST, SCA, secrets detection, CSPM and ASPM. Find and fix issues before they hit production.
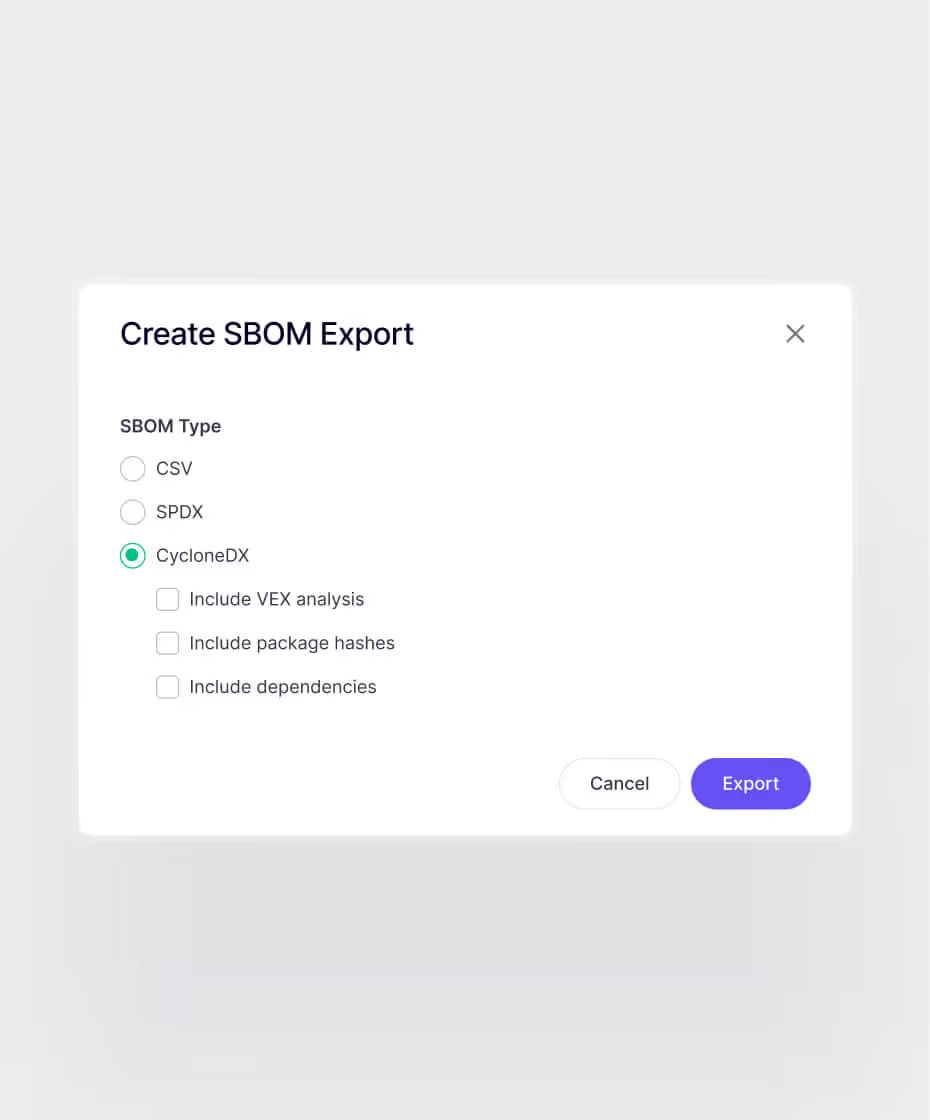
Prove compliance on demand
RA-5 scans, SBOMs, and POA&M-ready output, generated automatically. Evidence for FedRAMP, GovRAMP, SOC 2, ISO 27001, and NIS2, without the manual scramble.
Stay certified
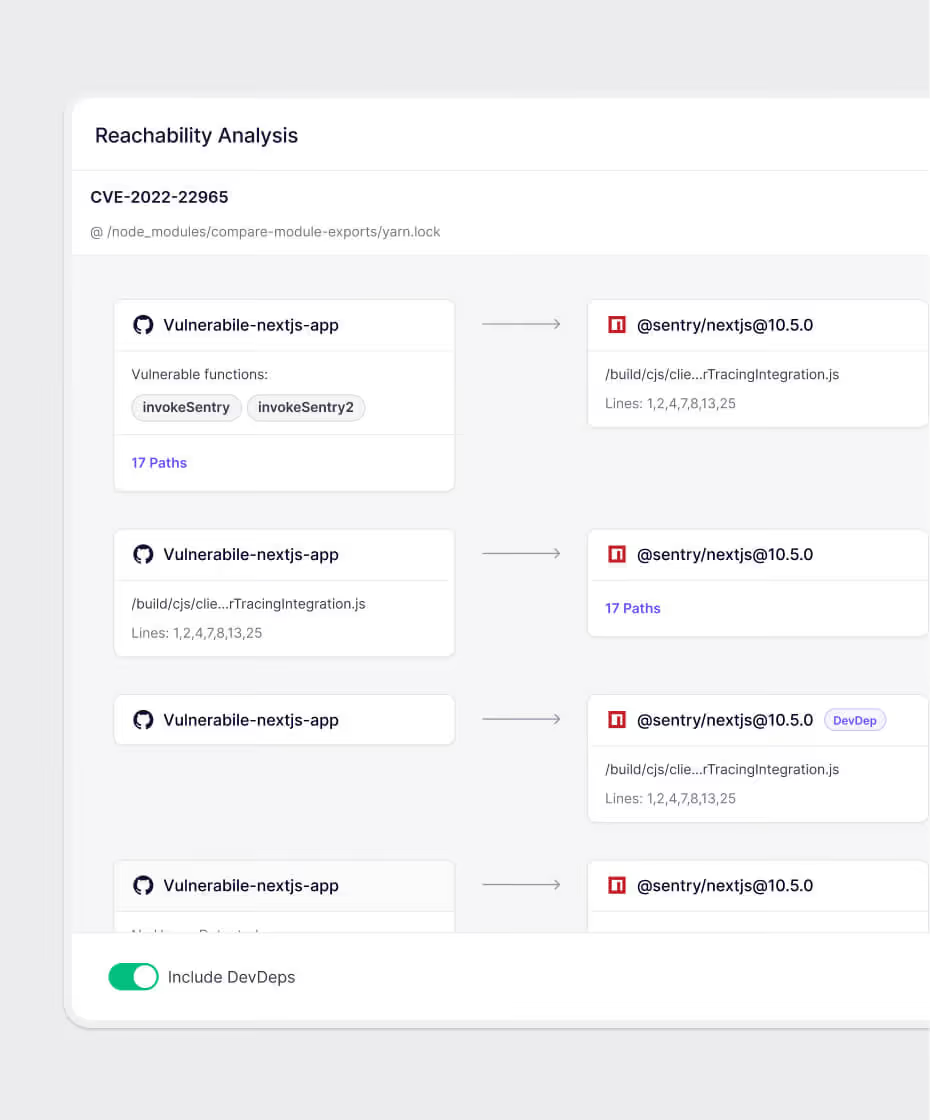
Continuous monitoring on every commit, not once a quarter. Reachability-aware prioritization cuts false positives by up to 95%, so your team fixes the exploitable issues first.

“Aikido let our engineers get back to what they do best building advanced defense systems without getting bogged down in CVE cleanup. It's helped us win projects, build trust, and stay ahead of schedule.”
Sam StentonHead of DevOps & Platform, SiXworks

“The fastest time we fixed a vulnerability was just 5 seconds after detection. That is efficiency.”
Aufar SukmajayaBack End Developer
Built for ongoing certification
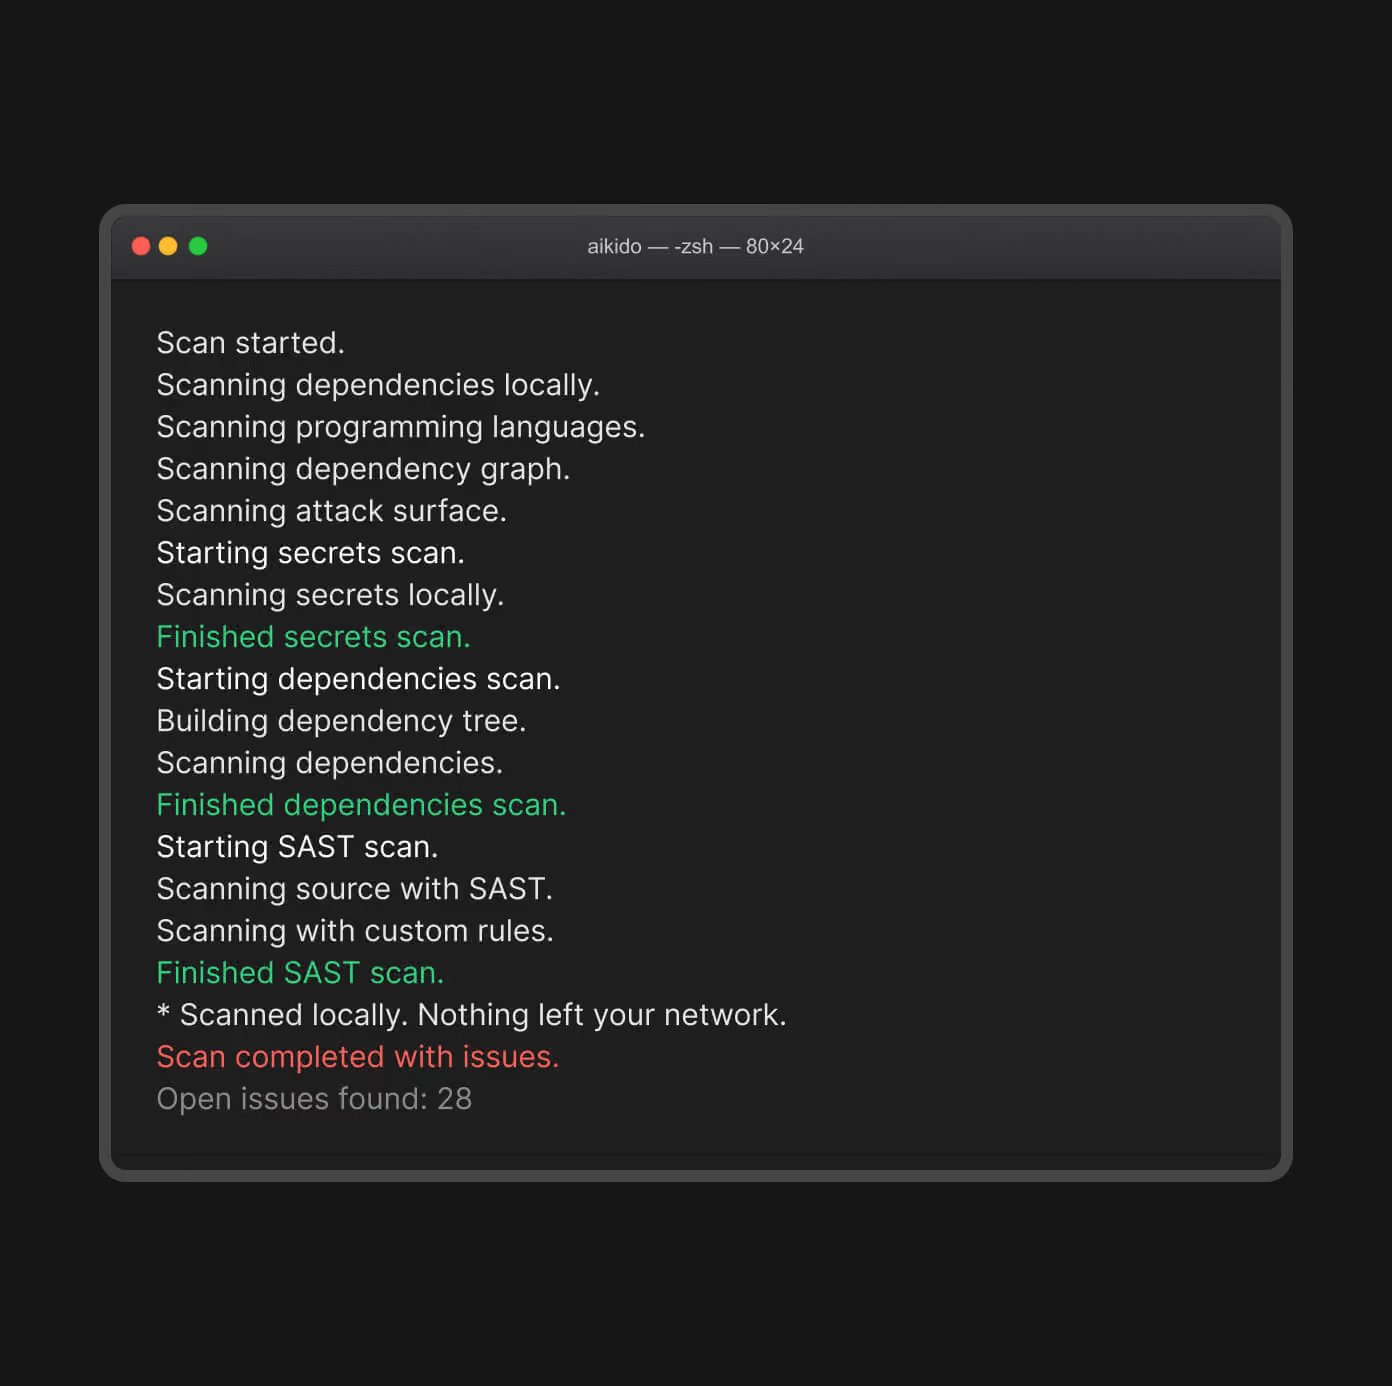
On-prem security
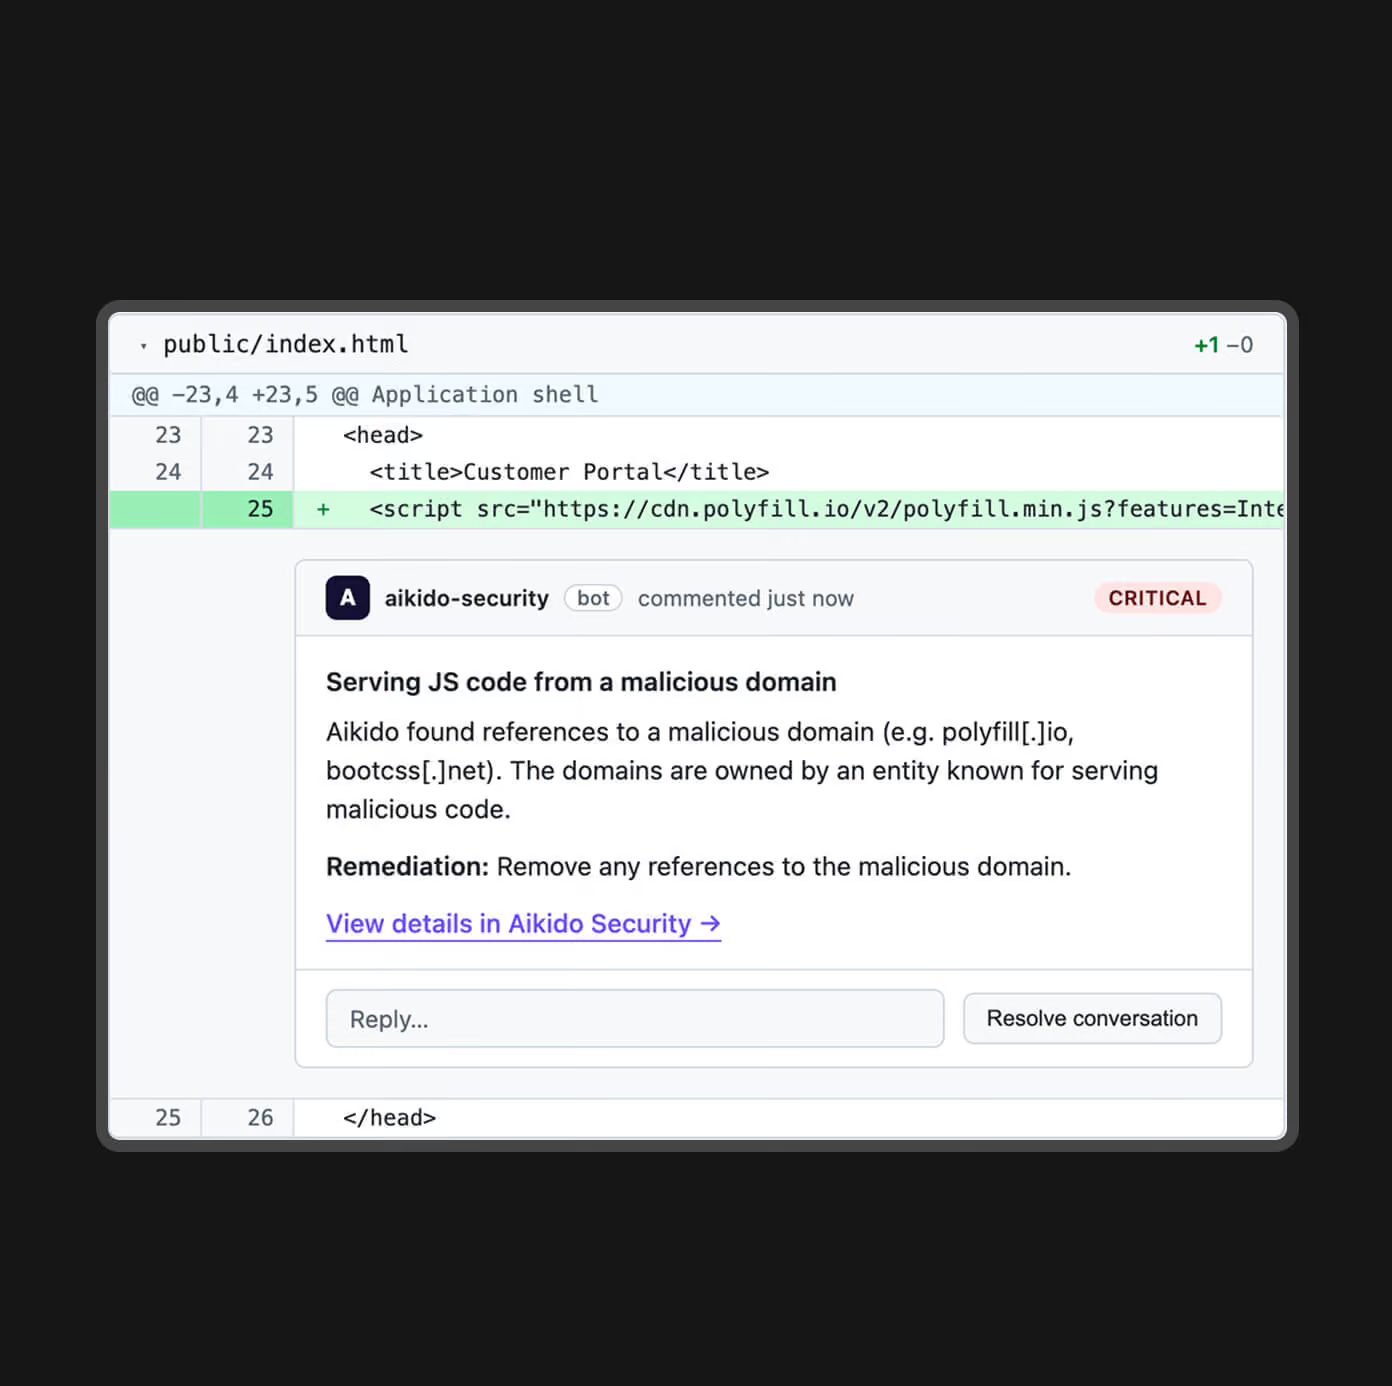
Aikido runs the full platform, including AI pentesting, inside your network. Nothing leaves your boundary.
Fully on-prem: The complete platform for IL5+, air-gapped & classified-adjacent environments.
CI-only option: Local scanners run in your pipeline; no code leaves your build environment.
Same evidence: Identical findings & exports, on-prem or cloud.
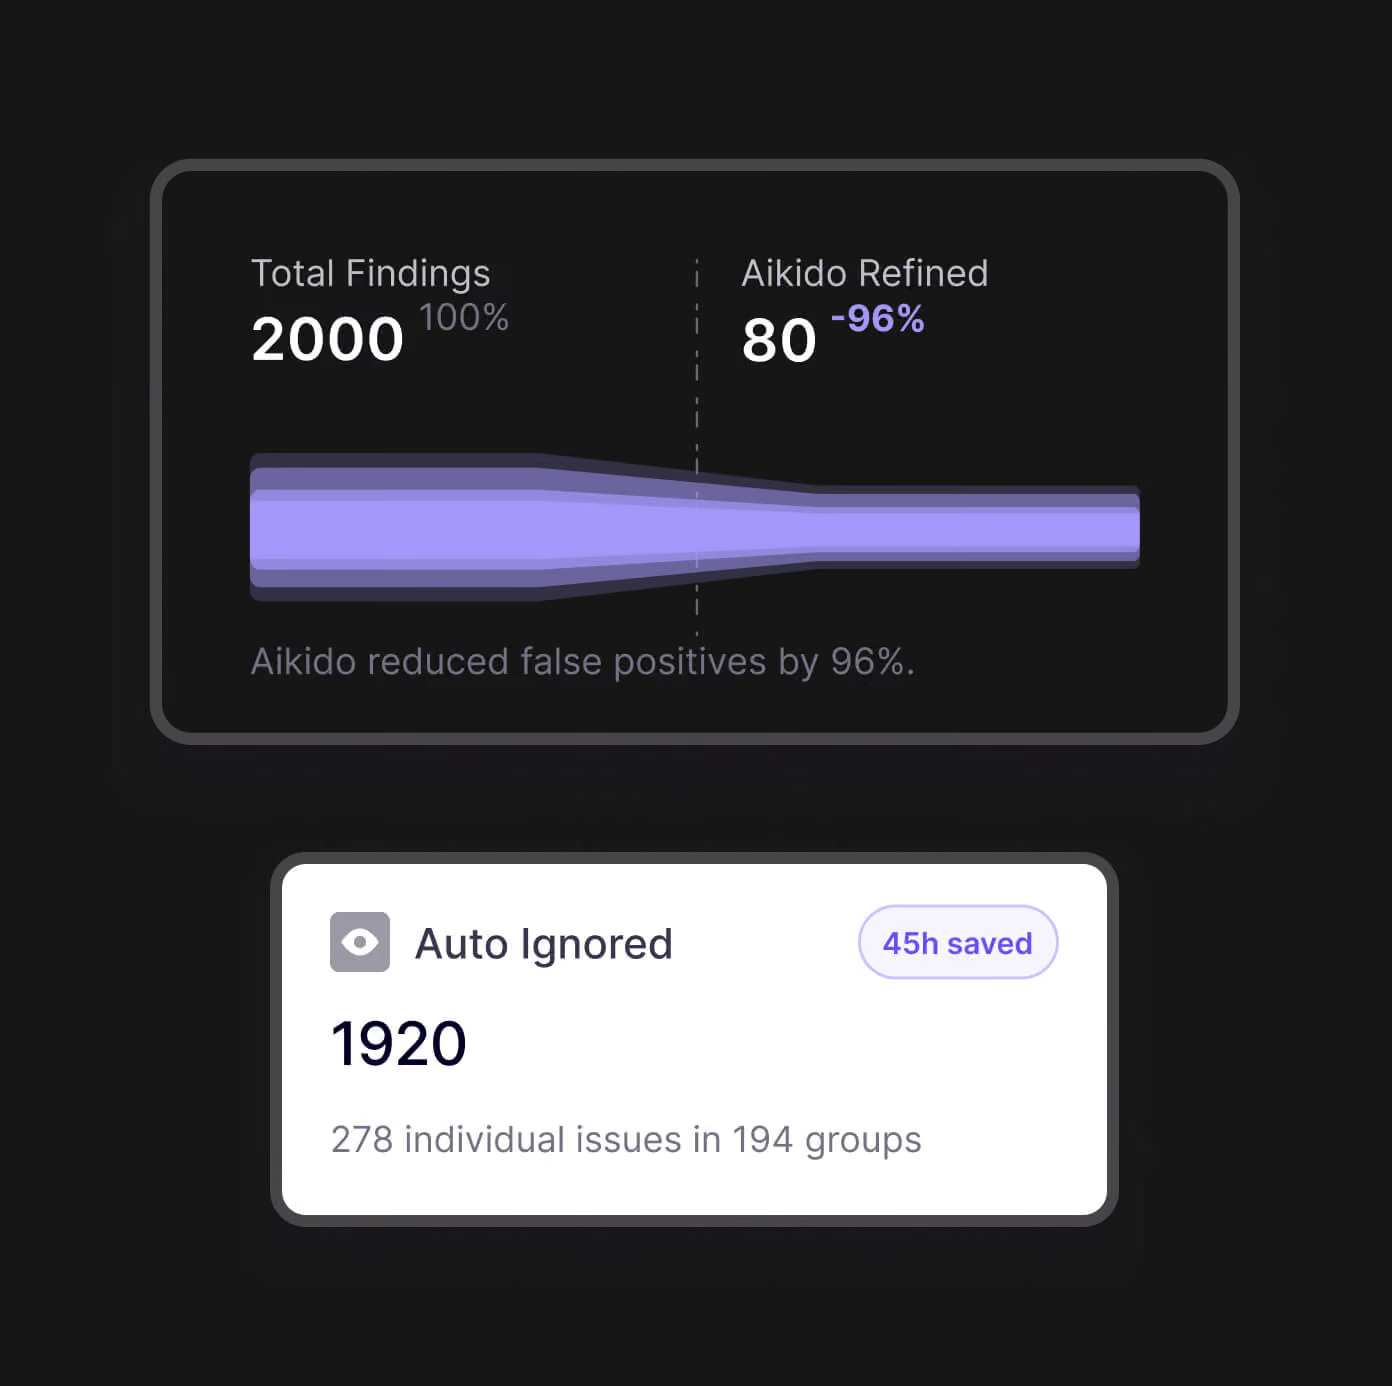
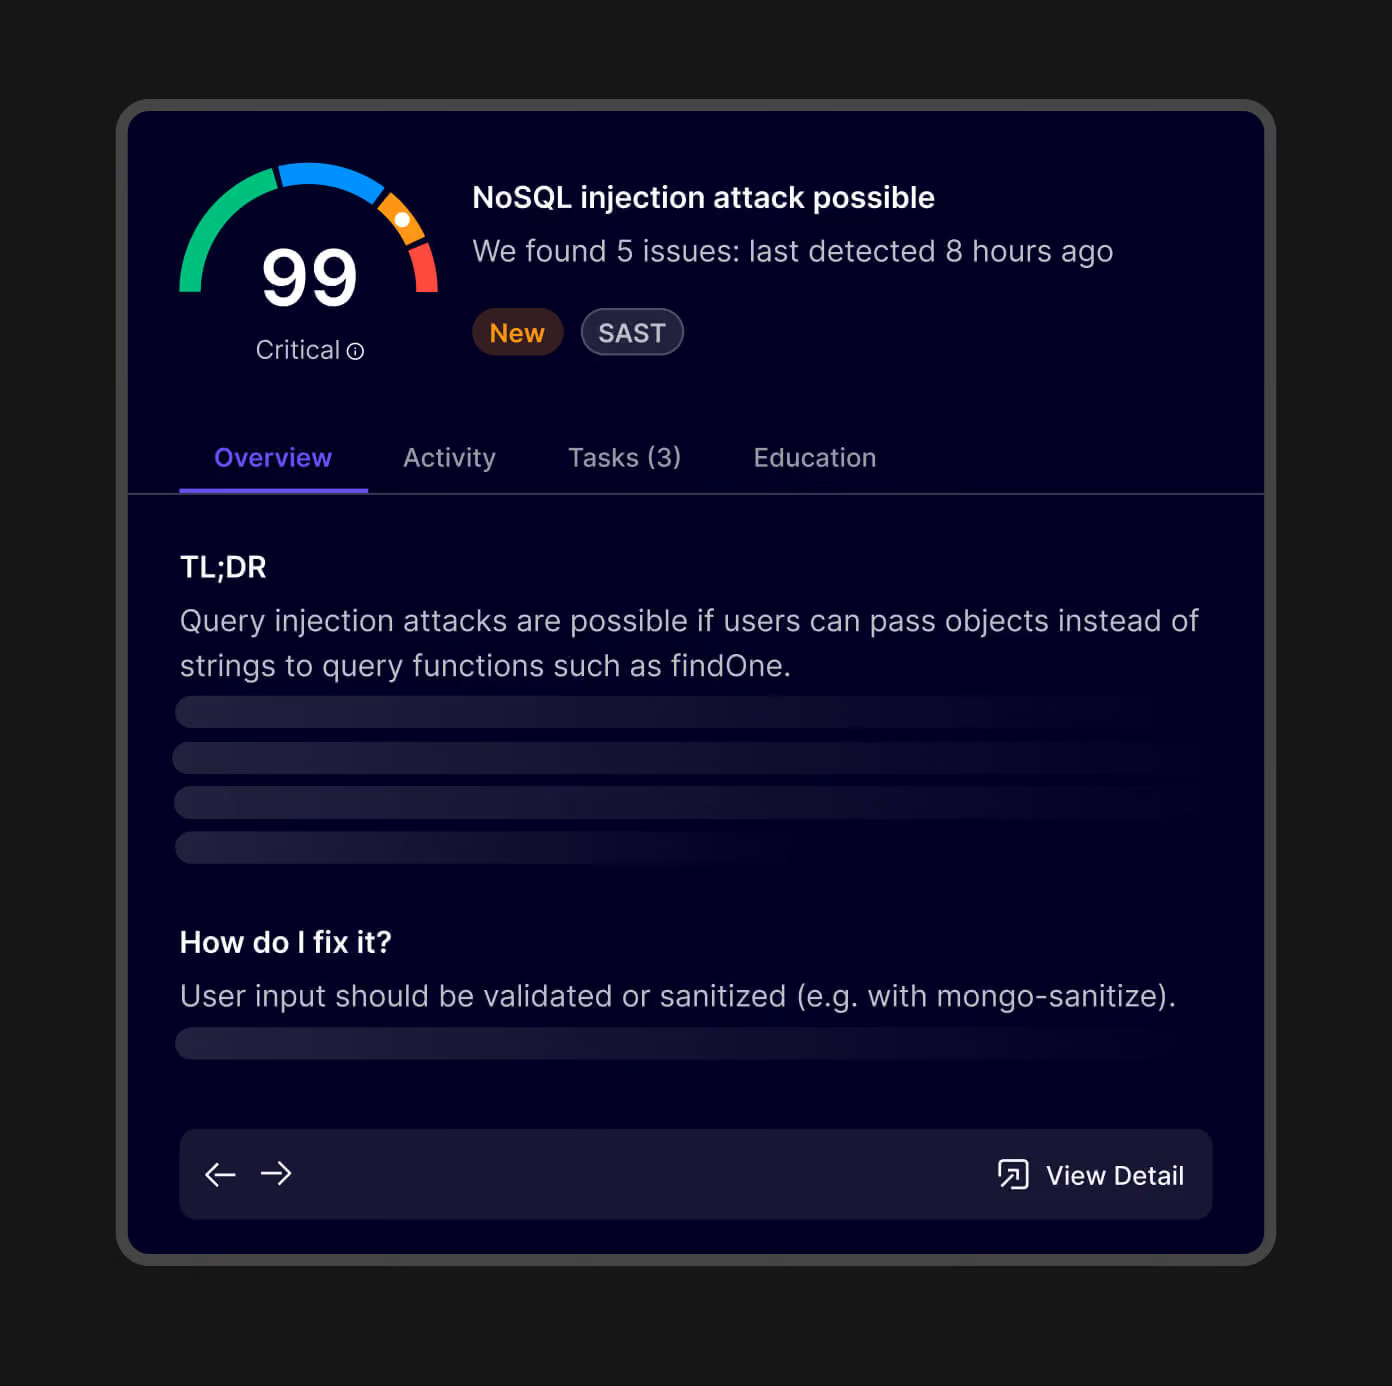
AI pentesting entirely under your control
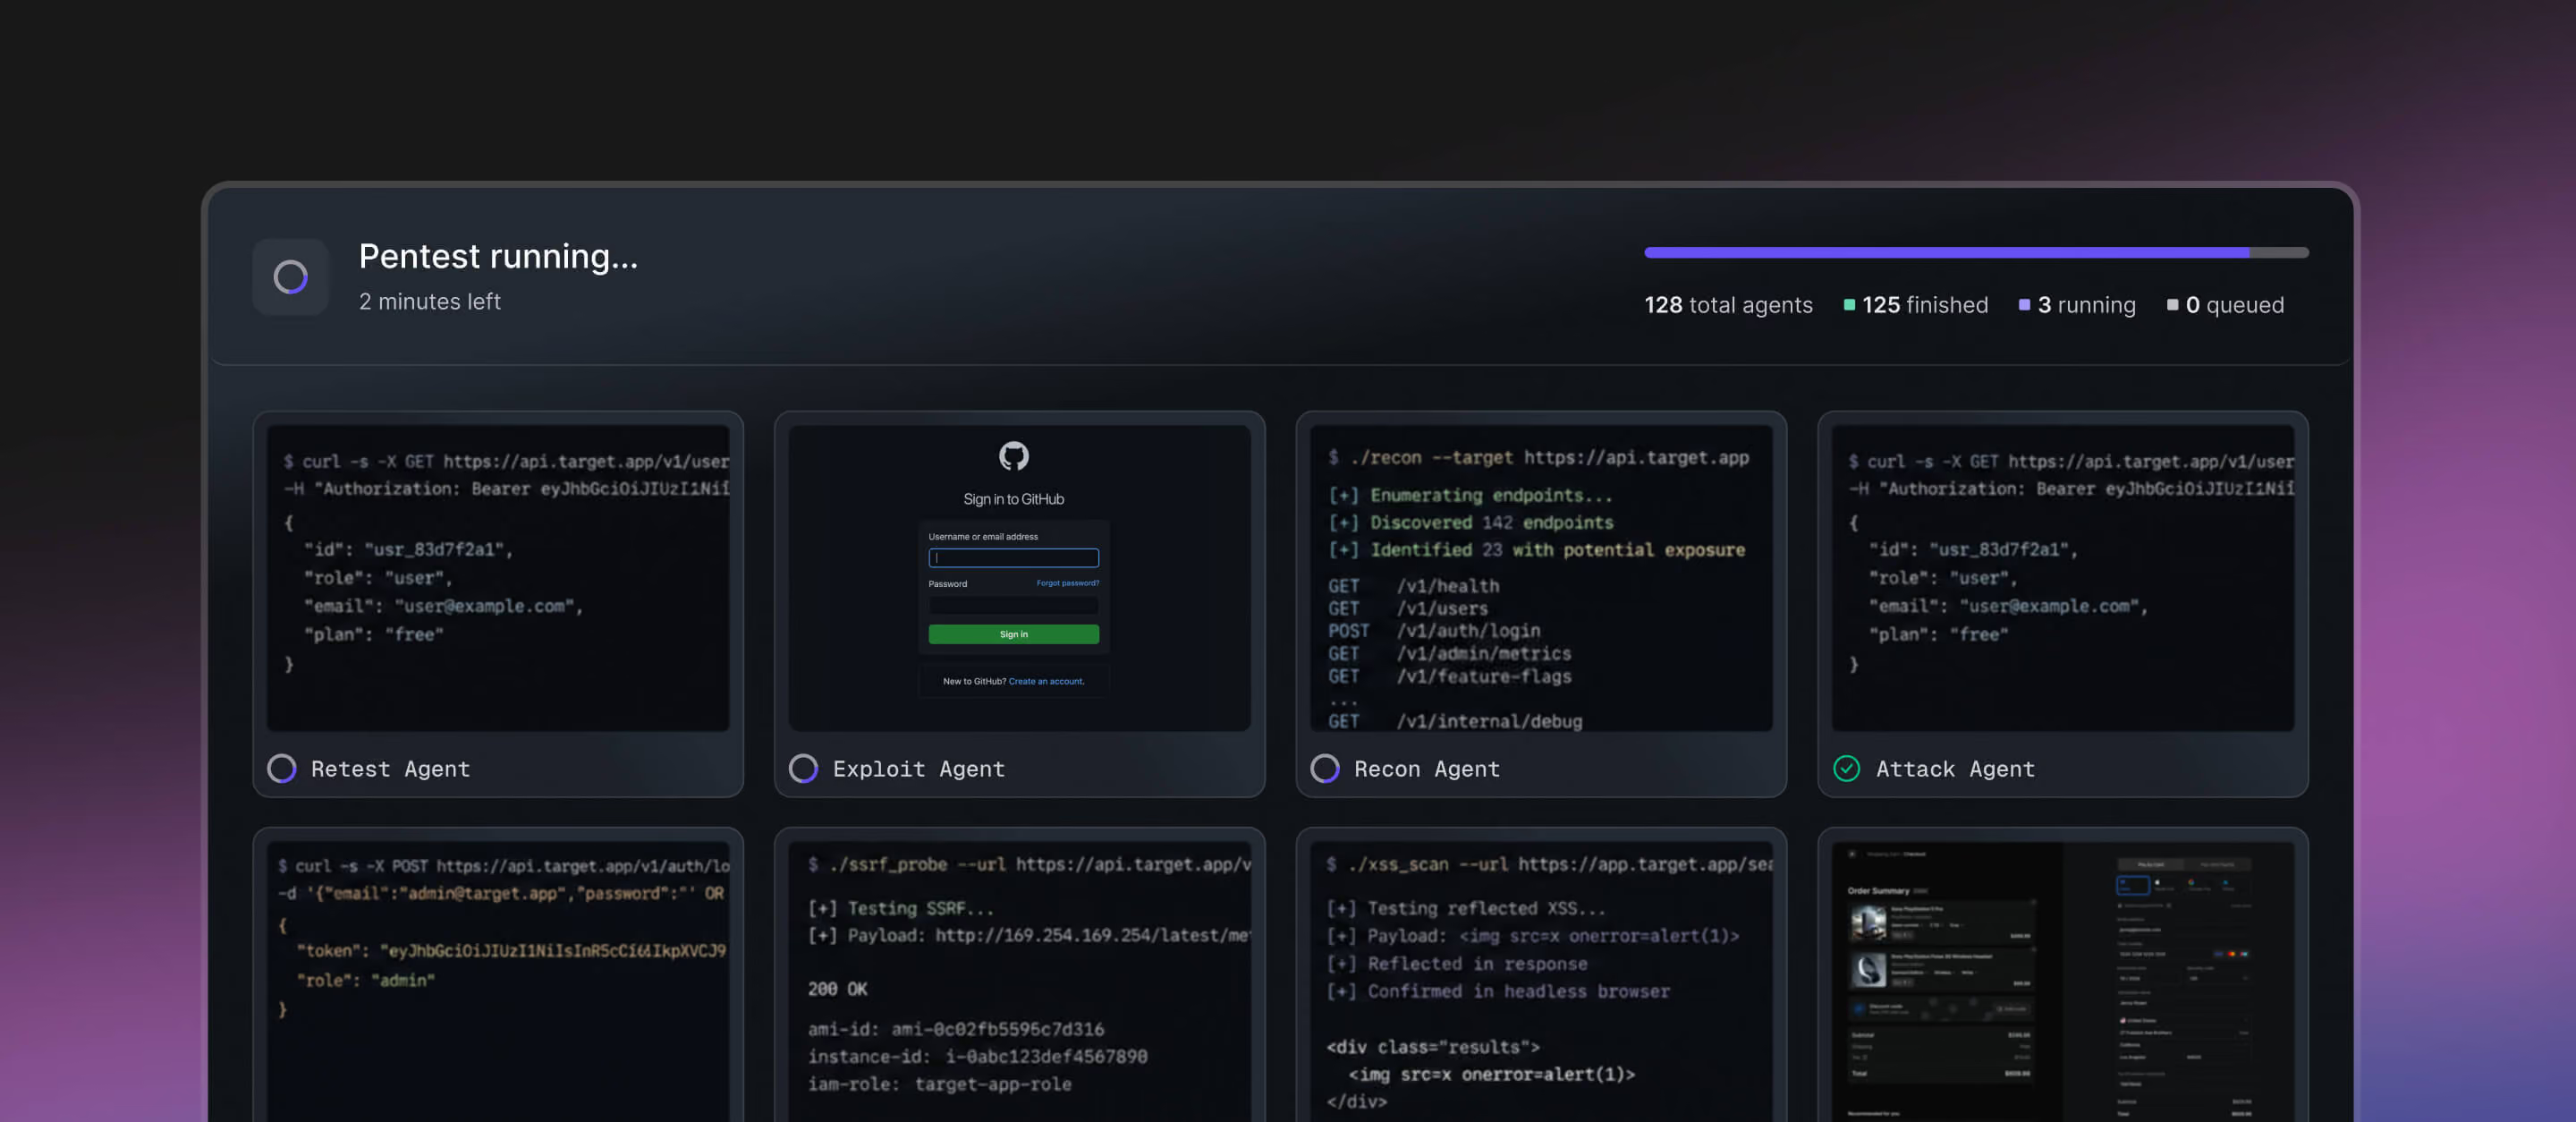
Continuous AI pentesting that keeps your code on-prem.
Finance, healthcare, and pharma ship constantly, and compliance expects regular pentesting but your code can't leave the network.
Aikido Machine pentests every deployment, validates exploitability, generates patches, and retests the fix.
Autonomous pentesting for networks that never touch the internet.
Classified and mission systems can't send code to a cloud, and often can't allow external operators access.
Aikido Machine runs entirely inside your enclave, air-gapped, with its own models on its own hardware, so nothing leaves the network.
Test critical systems without citizen data leaving.
Government systems hold people's personal data and tend to run for decades. Rules like GDPR and FedRAMP often mean that data has to stay in the country and off the public cloud, which rules out most AI pentesting tools.
Aikido Machine runs entirely on your own infrastructure, ensuring data sovereignty.
Talk to our federal team
See Aikido on one of your systems, hosted in GovCloud or inside your network.
Frequently Asked Questions

Yes. As of October 2026 Aikido is FedRAMP Moderate Authorized on the Knox Systems ATO in the FedRAMP Marketplace.
The new FedRAMP path for cloud services built on certified infrastructure: continuous, evidence-based, no government-specific fork of the product. Rev5 stops accepting new certifications in June 2027.
No. Scans run in temporary containers destroyed after analysis. Read-only access, always.
Yes. Aikido for Government can be deployed as an on-prem solution, including AI pentesting . Local scanners cover CI-only setups. Nothing leaves your boundary.
We map findings to NIST SP 800-53 controls, including RA-5. Export evidence for ATO packages, POA&Ms & ongoing certification reports.
Aikido for Government is the separate government edition (app.aikidogov.us, AWS GovCloud, operated by US persons). It is not possible to self serve, or transition to the FedRAMP environment. They are two completely separate SaaS products with different entitlements.
Yes. As Aikido for Government, the separate government edition. You can find us as part of the Knox listing.