

The Armadin alternative that pentests every release
Aikido connects to your repos, pentests every release and proves every finding before you see it. You get the price before the test starts and the results the moment it ends.

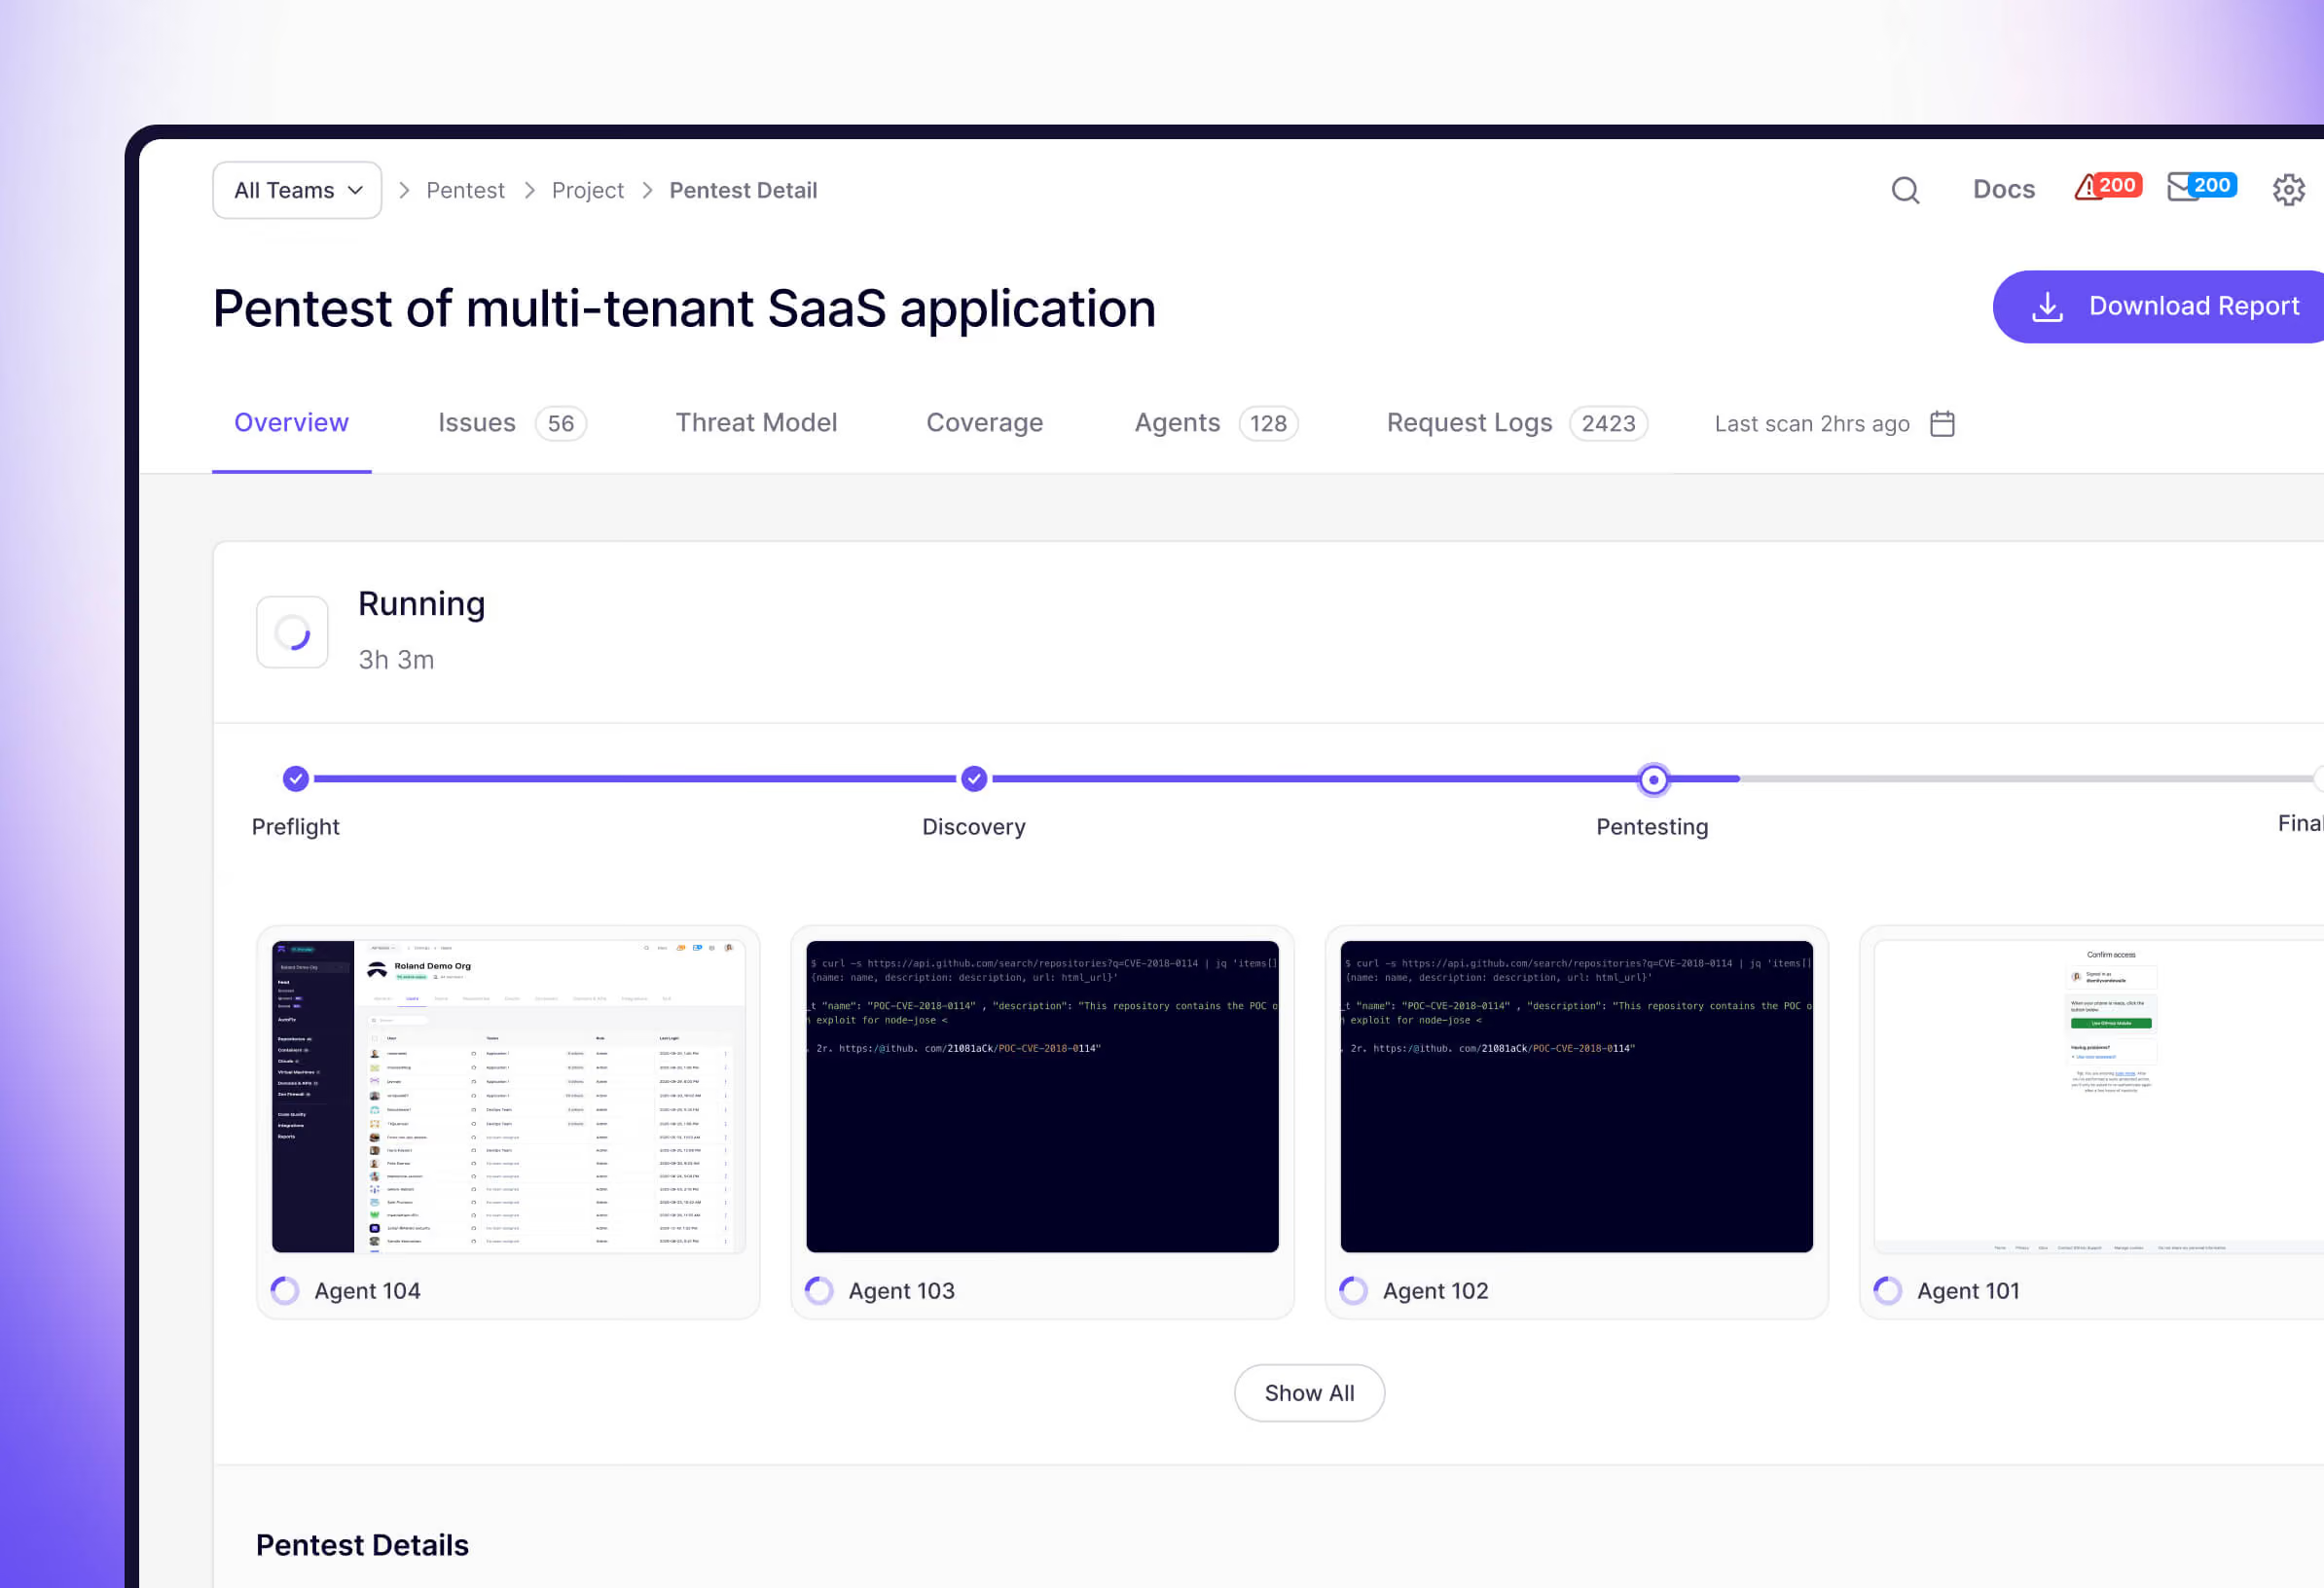





Where Aikido goes further than Armadin
Pentest every release, straight from your repos
Armadin works from source code you upload. Aikido connects to your repos, so when new code ships, Aikido Infinite pentests the change before it reaches your users.
Know the price before
you start
Armadin doesn't publish pricing, and every engagement starts with a sales conversation. Aikido sets the price from your actual scope before the test runs.
The fix arrives as
a pull request
Armadin hands your team remediation guidance. For web apps and APIs, Aikido hands you an AutoFix PR.

“Before, we’d just have an annual pentest once a year, often more of a checkbox than anything else. With AI pentesting we can find problems as soon as we release them. We can fix them before someone finds it.”
Gavin WilliamsEngineering Manager
Aikido vs Armadin


Start you own pentest in 5 min.
Get a full SOC2-ready report the same day.
See Aikido in action
Enter your work email to view the video

From your source code to your external network, in one product
Most security leaders run more than one offensive security program, from app pentests before release to external testing of the attack surface. Aikido covers each one with a pentest built for that surface, and puts every finding in the same place as your code and cloud findings.
Web apps and APIs
Agents read your repos, then attack the running app as each user role. They go after logic flaws, like one customer reading another customer's data.
Mobile apps
Upload your iOS or Android build, and add the backend code if you want deeper results.
External networks
Starting from just your domains, agents map your subdomains and internet-facing systems, then test exposed services and leaked credentials on your login pages.
AI Capabilities
You stay in control. Aikido verifies findings but won’t chain exploits or dig deeper unless you approve it first. On your perimeter, agents also skip systems you don’t own.

Top-tier pentest, flat-rate price.
Full PDF report for SOC 2 & ISO 27001
One application, one set of APIs


Full PDF report for SOC 2 & ISO 27001
Coverage scales with your application
How a rightsized pentest is calculated

Continuous reports & real-time findings
Always-on, scales with your releases
Start your Pentest in under 5 min
Automated penetration testing that matches human creativity with machine speed.
Detect, exploit, and validate vulnerabilities across your entire attack surface, on demand.


