

Seventy-three percent of teams still rely on manual reviews, even as GenAI writes more and more of their code. If you're one of them, that's fine, but there's a better way.
Human oversight is invaluable. On a large codebase, though, it's slow, inconsistent, and easy to let something through, which is where AI code review tools earn their place. They catch what a fast human pass misses, hold style consistent, and free developers to spend their attention on the reviews that actually need judgment.
The better tools now read a change against the rest of the codebase and reason about what it might break elsewhere, working directly in the pull requests and IDEs developers already use. This guide covers the top AI code review tools teams are using today, with a side-by-side comparison to make the call easier.
Curious about how AI code reviews work? Check out these articles on, Using AI for Code Review: What It Can (and Can’t) Do Today and Manual vs. Automated Code Review: When to Use Each.
TL;DR
Aikido Security earns the #1 spot as the top AI code review tool in this list. It reviews every pull request and secures what's in it. The AI review gives inline PR feedback, one-click fix suggestions, and custom rules that learn from your team's past PRs, catching the logic bugs and null dereferences a standard review tends to miss. A deeper layer reasons about business logic on each change, so access-control bugs like IDORs get caught while the pull request is still open. The same reasoning runs across the whole repository, surfacing real logic flaws before a live target even exists to test against.
Findings come with fix recommendations for secure code fixes and single-click suggestions for SAST and IaC issues. IDE plugins catch secrets and code problems as you type, before anything reaches the repository. And it doesn't stop at the pull request. Dependencies, cloud, and runtime are covered in the same platform.
{{cta}}
Top 4 AI Code Review Tools (Comparison Table)
How Aikido Security Handles Code Review
Top 9 Best AI Code Review Tools
1. Aikido Security
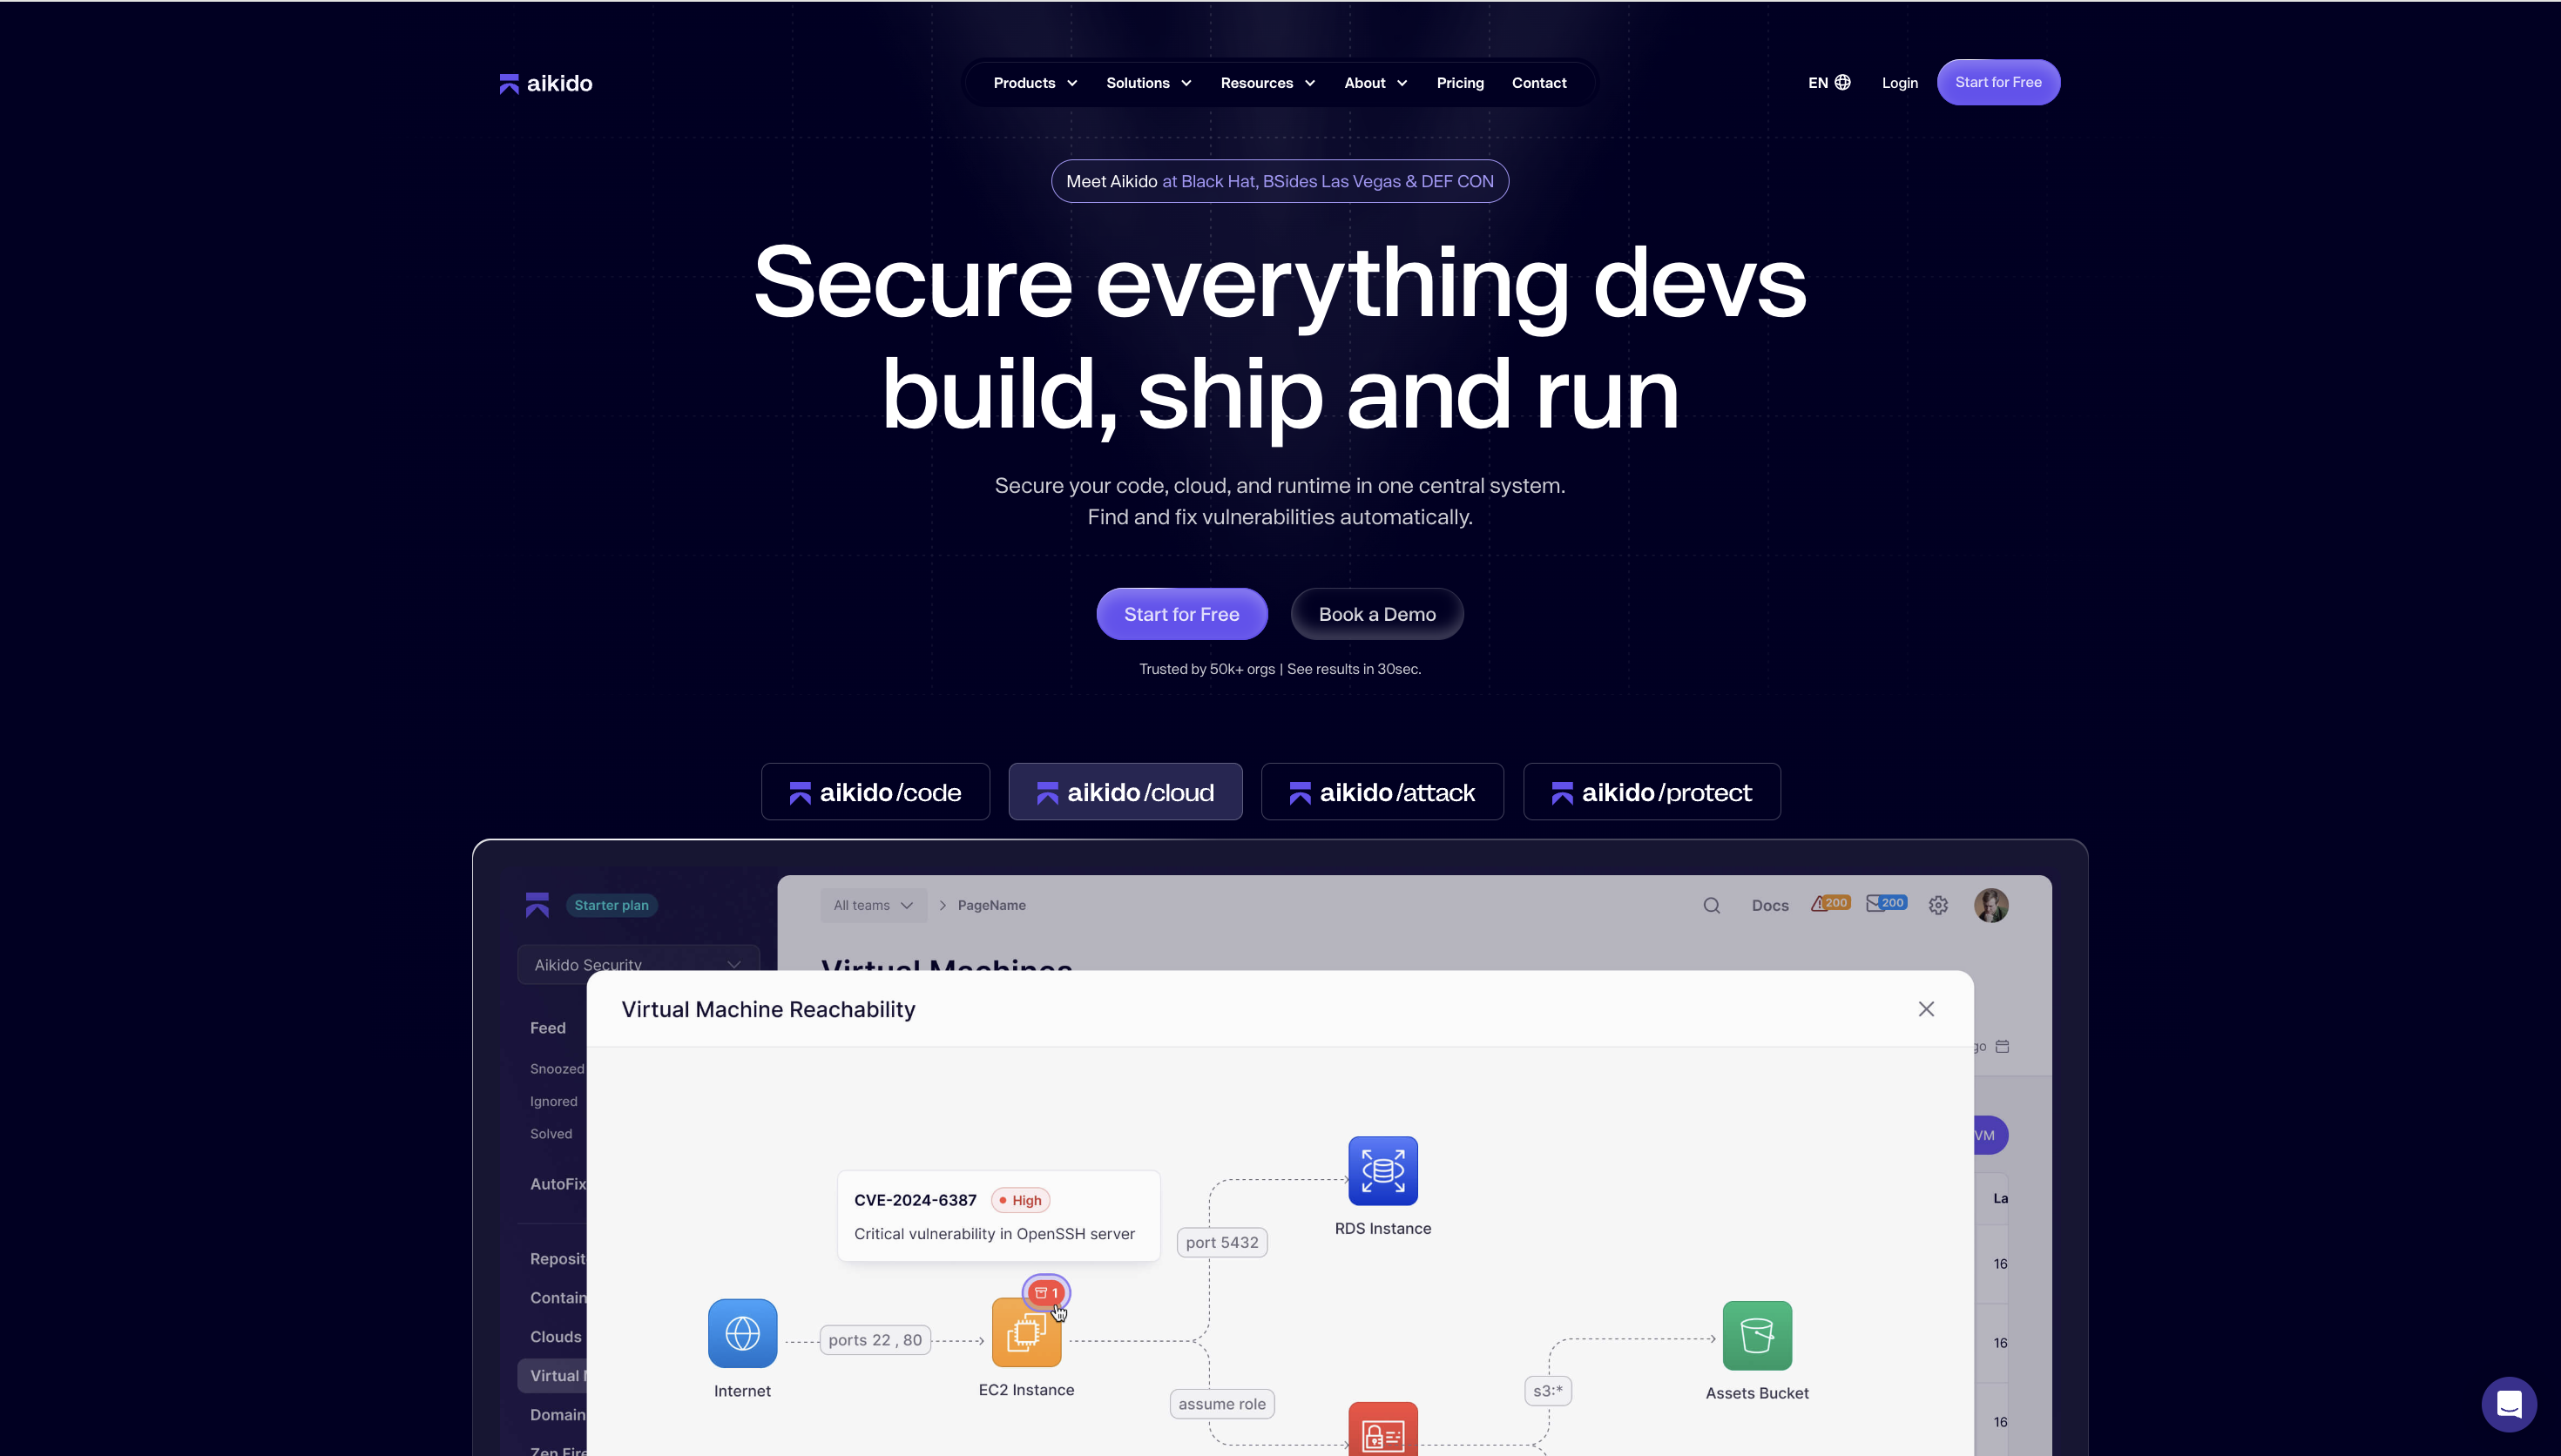
Aikido Security reviews every pull request and secures what's in it, across three products that work at different depths. Code Quality handles the day-to-day review. Deep PR Review runs full AI reasoning on every pull request as it opens. Code Security Audit turns that same reasoning on code you've already shipped. All three run across your version control, CI/CD pipelines, and IDEs, reading each change against the wider codebase rather than the diff alone.
Code Quality produces inline PR comments and one-click fixes on every change, with custom and predefined rules you enforce across the team. Connect a repo and it runs on smart defaults, no config. It gives instant, context-aware feedback, learns your codebase from past reviews, and turns your team's tribal knowledge into reusable rules, so your best engineers' instincts get baked into every review. Rather than matching patterns, it uses LLMs to understand intent and context, which is how it flags "good-looking" code that compiles fine but could still break production. Developers only see actionable, high-severity notifications, so they move from detection to remediation without switching tools.
Deep PR Review is the layer for teams shipping faster than they can read. Coding agents now open more changes in a day than a team can review, and a diff-level pass wasn't built for that volume. Deep PR Review reads each pull request the way a senior engineer with unlimited time would. Before it flags anything, it takes in your whole codebase, related repositories, existing static results, and the comments already on the change. That context is what lets it reason about business logic and catch access-control bugs like IDORs while the pull request is still open, well beyond what a linter or a fast human pass will see.
Code Security Audit turns that same reasoning on code you've already shipped, following data flow and permission checks across services to find where the logic breaks down. It takes several individually low-severity bugs and works out the single privilege-escalation path they add up to, the kind of multi-step exploit an attacker would actually build. Every finding shows what's exploitable and how someone would reach it, with a full reasoning trace, and it runs on your source with no test environment to wire up.
Code Coverage allows you to upload test coverage from GitHub Actions and track it next to your security and quality findings. See which repositories are under-tested, browse uncovered files down to the line, and watch coverage move as you add tests. When a scan or PR check flags a file, you can check in the same place whether that file is even tested. Learn more
Together the three cover the pull request, the review of it, and the code already in production. And review is one part of a wider platform: SAST, dependencies, secrets, cloud, and malware detection live in the same place, each a product in its own right rather than a lightweight add-on. In 2025, Aikido acquired Trag AI, which trained custom large language models on real-world codebases, giving the review engine deeper semantic understanding and better context across complex codebases.
Key features:
- Business-logic awareness via LLMs: understands intent and context, catching logic and access-control flaws that static-only tools walk past.
- Deep PR Review: reasons about business logic on every pull request, catching IDORs and broken access control that SAST and a fast human review both miss.
- Code Security Audit: reasons about shipped code, tracing data flow and permission boundaries across files and services to surface flaws and multi-step exploit chains, with no environment to wire up.
- Code Coverage: shows you test coverage across repositories, files, and lines, alongside your code quality findings.
- Codebase-aware rule generation: learns from your team's past PRs and turns tribal knowledge into reusable rules.
- AI-driven SAST: reviews source for vulnerabilities, misconfigurations, and quality issues at both pre-commit and merge stages.
- Secrets detection: spots hardcoded credentials and API keys before they reach production.
- Continuous compliance monitoring: maps findings to SOC 2, GDPR, HIPAA, and other frameworks with exportable, audit-ready reports.
- Data privacy: doesn't store your source after analysis or use it to train its models.
Pros:
- Three products covering the pull request, the review, and shipped code, all reasoning about business logic rather than matching patterns.
- Custom rules that hold consistently across hundreds of repos, from one service to a full estate.
- Strong compliance coverage for regulated industries, with audit-ready reporting.
- Broad language support and multi-repository management from one place.
- Predictable, flat-rate pricing with no per-line or per-module surprises.
Best for:
- Enterprise teams where finding and fixing issues quickly is mission-critical.
- Teams shipping AI-generated code faster than humans can review it, who need an independent layer on every PR.
- Regulated environments where audit trails and compliance are non-negotiable.
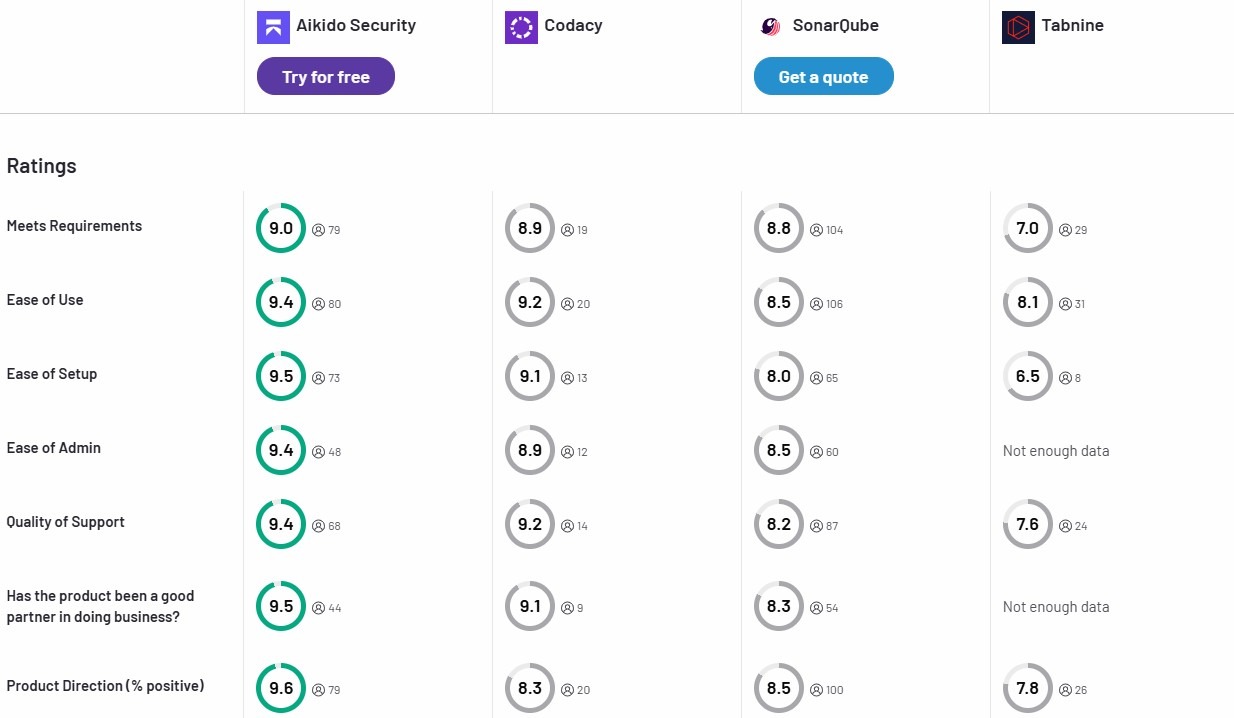
Gartner Rating: 4.9/5.0
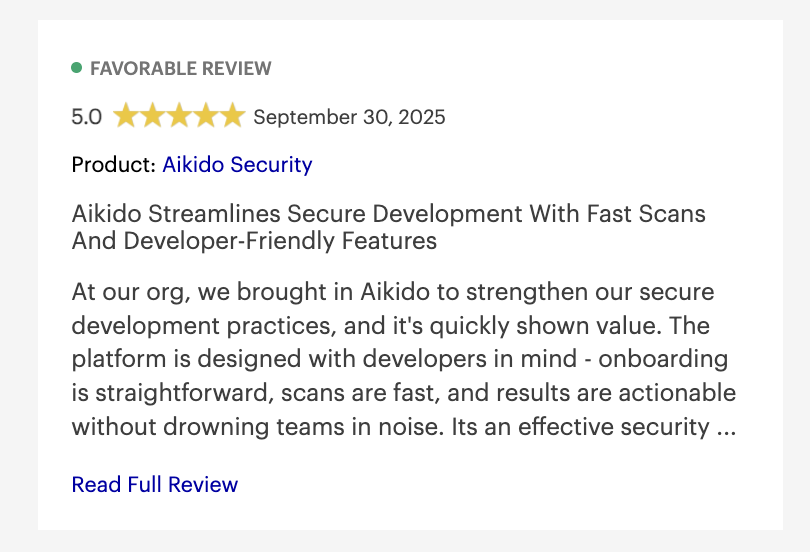
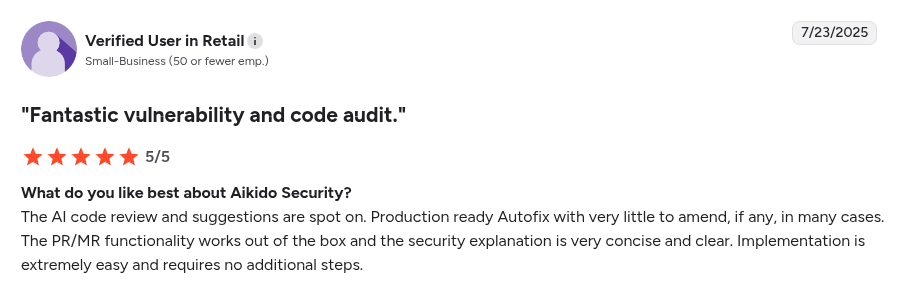
Aikido Security Reviews:
Beyond Gartner, Aikido Security also has a rating of 4.7/5 on Capterra and SourceForge.
Curious about the difference between AI code review tools and automated code review tools? Check out our article, AI Code Review vs Automated Code Review: The Complete Guide.
2. Codacy
Codacy is a code quality automation tool that focuses on code style, static analysis, duplication detection, and standards enforcement..
Key Features:
- Customizable Quality Gates: Teams can set minimum criteria for merging code, like coverage or linting thresholds.
- Real-Time Feedback: As soon as code is pushed, it provides automated insights into issues-speeding up iteration cycles.
- Multiple Language Support: Works well for diverse stacks, enforcing standards consistently.
Pros:
- Broad language support
- Customizable quality gates
- Supports common CI/CD platforms
- Automates reviews by commenting on pull requests.
Cons:
- Pricing can be expensive for larger teams.
- Limited Customization for Advanced Rules
- Users report slow support response
- Users report slower analysis in large codebases
- Limited security and compliance features
Ideal Use Cases:
- Small to Medium-Size Teams: Especially those seeking to formalize quality practices without heavy configuration.
- Early-Stage Startups: Where resources for manual code reviews are limited, but basic static checks are critical.
Gartner Rating: 4.4/5.0
3. DeepCode AI (now integrated with Snyk)
DeepCode AI (now part of Snyk) uses machine-learning and semantic analysis to identify security risks and recurring code patterns that would have been missed by traditional linters.
Key Features:
- AI-Powered Semantic Analysis: Sifts through vast open-source datasets to flag unusual or previously unknown bug patterns.
- Integration with Snyk: Integrates with the Synk platform for deeper dependency and license risk analysis.
Custom Rules: Allows teams to define and save their own rules.
Pros:
- Multi-language support
- Dependency-aware insights
- CI/CD integration
Cons:
- False positives
- Learning curve
- Requires tuning for noise
- It can miss issues in non-standard or proprietary codebases
- Fix suggestions are sometimes generic
- Users report slow scans on large repositories
Ideal Use Cases:
- Security-Focused Teams: Projects dealing with open-source dependencies where subtle security bugs can sneak in.
- Open-Source Projects: Where detection of unconventional vulnerabilities is a priority.
Gartner Rating: 4.4/5.0
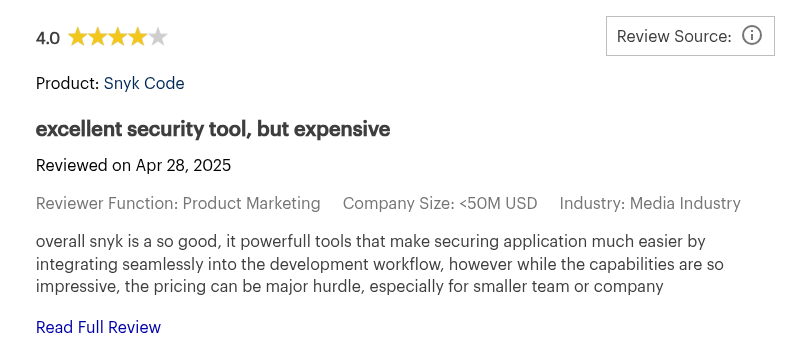
DeepCode AI Reviews:
4. Tabnine
Tabnine is an AI-powered coding assistant that specializes in code completion, offering real-time suggestions as developers' type. It’s primarily focused on improving productivity and code consistency.
Key Features:
- Real-Time Code Completions: Boosts developer velocity, especially for repetitive or boilerplate-heavy work.
- Works with Popular IDEs: Integration with VS Code, JetBrains IDEs, and others brings AI suggestions to daily coding workflows.
- Team Knowledge Sharing: Trains on your project's codebase to offer tailored suggestions, fostering team consistency.
Pros:
- Multi-language support
- Context-aware suggestions
- Integrates with major IDE’s
Cons:
- Learning curve
- AI code review agent is limited to its enterprise plan
- Limited free features
- May cross-file semantics in large projects.
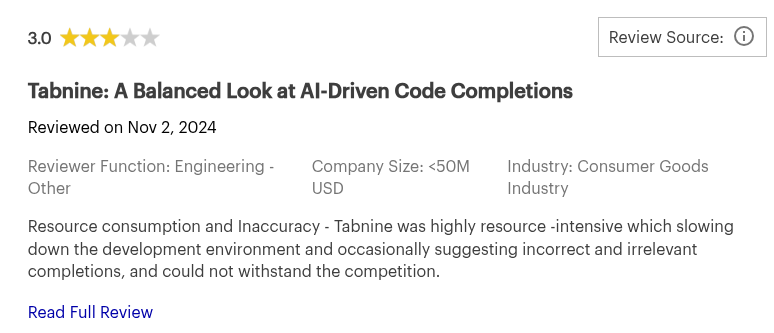
- Users have reported high resource consumption during use
Ideal Use Cases:
- Individual Developers: Those looking for speed and efficiency, especially in fast-paced product teams.
- Repetitive Tasks: Projects with a lot of repetitive or formulaic code structures.
Gartner Rating: 4.1/5.0
Tabnine Reviews:
Exploring more tools and how they compare? Check out our article on The Top 18 Best Code Review Tools of 2026
5. CodeRabbit
CodeRabbit streamlines code review processes by providing automated feedback, collaboration, and customizable rules to meet project standards.
Key Features:
- PR Summaries and Explanations: Provides summaries of code changes to help reviewers understand pull requests.
- Context Visualization: Can generate sequence diagrams or flow explanations for complex code changes.
Pros:
- Supports multiple programming languages
- Integrates with Git workflows and IDEs like VS Code
- Zero-data retention policy
Cons:
- Advanced features (like self-hosting or compliance options) are available only in higher-tier plans
- Limited customization
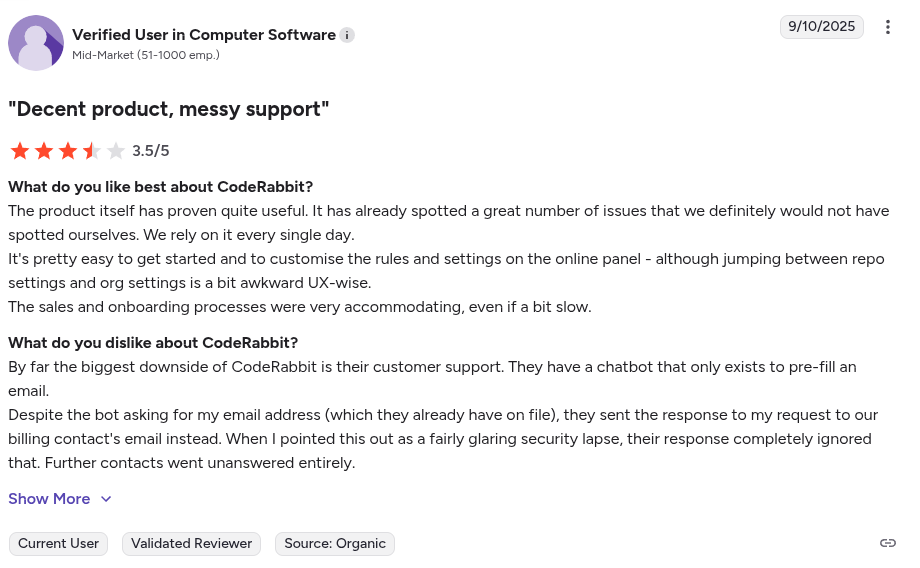
- Users have reported performance issues in large repositories and complex PRs
- May generate noisy or irrelevant comments if not fine-tuned
Ideal Use Cases:
- Startups and mid-sized teams: Teams that want to maintain code quality while scaling quickly.
Pricing:
- Free
- Lite: $15 per month/developer
- Pro: $30 per month/developer
- Enterprise: Custom pricing
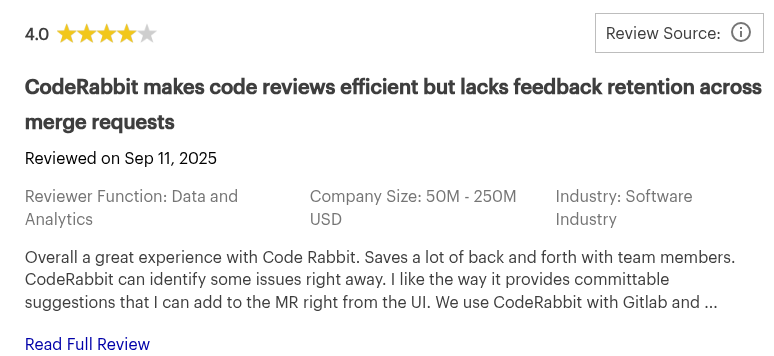
Gartner Rating: 4.0/5.0
CodeRabbit Reviews:
6. CodeAnt AI
CodeAnt AI combines automation with flexibility, offering tools to detect, fix, and optimize code efficiently. Developers primarily use it because of its end-to-end AI-augmented code review and understanding of abstract syntax trees (ASTs).
Key Features:
- CI/CD integration: Supports common CI/CD tools.
- Automated Documentation: It can automatically generate documentation for the entire codebase.
- Custom Rules: Allows teams define and enforce custom coding standards.
Pros:
- Custom rules
- Built-in security features
- Automated documentation
- Automatic PR summaries
Cons:
- Learning curve
- Still a relatively new tool
- False positives
- May require additional configuration
- Review speed and performance may degrade with very large repositories
- Slow response time
Ideal Use Cases:
- Startups and scaling tech teams: Especially useful for fast-growing teams that want to enforce code standards and security checks without needing a large team of senior reviewers.
Pricing:
- Basic plan: $12 per user/month
- Premium plan: $25 per user/month
- Enterprise plan: Custom pricing
Gartner Rating:
No Gartner review.
CodeAnt AI Reviews:
No independent user generated review.
7. Qodo (formerly Codium)
Qodo (formerly Codium) is an AI-driven code integrity platform that helps teams write, test, and review code with advanced automation and contextual understanding.
Key Features:
- Context-Aware Analysis: Uses retrieval-augmented generation (RAG) to index codebases and understand architectures
- Automated Test Generation: Generate unit tests, suggest coverage improvements.
- Multi-Agent Framework: Qodo is built around agents (e.g., Gen for code generation/testing, Merge for PR review)
Pros:
- Context-Aware suggestions
- Automated PR workflows
- Broad language support
Cons:
- Learning curve for advanced features
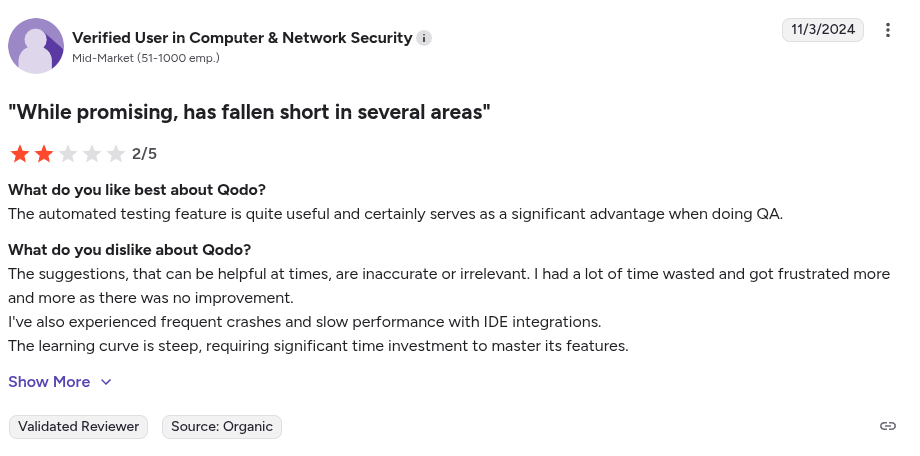
- False Positives
- Users have reported the user interface as confusing/clunky
Ideal Use Cases:
- Engineering teams practicing shift-left testing: Automatically generate tests and surface issues early in PRs to catch bugs before they reach CI.
Gartner Rating: 4.5/5.0
Qodo Reviews:

8. Sourcery
Sourcery uses a hybrid approach for its code review. It uses LLMs for contextual tasks like generating pull request summaries and a rule-based static analysis engine for code quality.
Key Features:
- Code Quality Metrics and Scoring: Provides metrics for functions, such as Quality Score, Complexity and Method Length.
- Security Scanning (SAST): Actively scans for security vulnerabilities and secrets within the code.
Pros:
- Automated Feedback
- Strong Data Privacy
Cons:
- Lack of Conversational Review
- May struggle with complex logic
- False positives
- Advanced features (robust custom rules) are locked behind the paid tiers
Ideal Use Cases:
- Individual Developers: As an automated "pair programmer" and learning tool that provides instant feedback to help improve coding skills and efficiency.
Gartner Rating:
No Gartner review.
Sourcery Reviews:
No independent user generated review.
9. Greptile
Greptile is an AI code review tool designed to catch bugs, antipatterns, and mismatches that simpler linters or difference-only tools might miss.
Key Features:
- AI Code Review: Automatically reviews pull requests (PRs) with full codebase context.
- Learning Capability: Greptile can learn from your feedback and adapt to your project.
- Contextual Assistance: Developers can ask Greptile natural language questions about the codebase
Pros:
- Actionable Feedback
- Full Codebase Context
Cons:
- Learning Curve
- Depends on third-party models for LLM inference
- Pricing can become expensive when scaling
- Limited support for multi-repository architectures
Ideal Use Cases:
Gartner Rating:
No Gartner review.
Greptile Reviews:
No independent user generated review.
Not sure how you can improve your team's code quality? Check out our article on Code Quality: What Is It and Why It Matters
Comparing the Top 9 AI Code Review Tools
To help you compare the capabilities of the tools above, the table below summarizes each tool's supported features with their ideal use cases.
Choosing the Right AI Code Review Tool for Your Workflow
AI-powered code review tools can accelerate development and reduce human errors, but only when they’re precise, developer-friendly, and integrate seamlessly with your existing workflows. Aikido Security delivers exactly that.
Aikido Security offers the best-in-class AI code reviews for start-ups to enterprises, coming out on top in technical comparisons and POC head-to-heads in each of these categories.
No more juggling multiple tools, drowning in false positives, or spending hours on manual reviews, just cleaner, faster, and more reliable code.
Want faster reviews and cleaner code? Start your free trial or book a demo with Aikido Security today.
FAQ
How accurate is Aikido Security’s AI review?
Aikido prioritizes signal over noise. It filters out over 90% of false positives before alerts reach developers. This reduces alert fatigue and keeps feedback actionable.
Can it suggest or apply fixes automatically?
Yes. Aikido Security provides AI-generated fixes and one-click pull request patches for supported languages and vulnerabilities.
Does it only scan full repositories, or can it scan just PRs?
It scans both. By default, Aikido Security run on pull requests to give feedback early, but you can also configure full repository scans or scheduled pipeline checks.
Is there support for monorepos or large codebases?
Yes. Aikido Security is built for scaling teams and monorepos. It can scan multi-service architectures and high-commit environments without slowing workflows.
Can we customize the rules or severity levels?
Yes. You can define internal coding standards, modify severity levels, suppress specific rules, or set quality/security gates before merges.
Does Aikido Security support compliance requirements like ISO, SOC 2, HIPAA, or GDPR?
Yes. It maps findings to major compliance frameworks and helps maintain audit-ready records for regulated industries like healthcare and finance
You Might Also Like:


