

You haven't got any time to lose.
Secure your software in no time.
Prove to your customers you're secure, gain their trust & sell more.




One Unified Platform to Secure Your Software
From code to cloud to runtime, Aikido covers every layer of modern software security. Start with the module you need, unlock the full platform as you grow.
All the security tools a startup needs
Dependencies, SAST, secrets, containers, infrastructure as code, cloud posture, DAST, malware in packages and AI pentesting.
Fully setup in a few minutes
Connect your repo and start your first scan in minutes. Only see the results that are important and fix them in one click.
SOC 2 and ISO 27001 compliance made easier
Your first big client will expect these from you. Aikido runs the technical checks behind SOC 2, ISO 27001, GDPR and NIS2, generates the evidence and syncs it straight into Vanta or Drata.
One security system,from code to production.
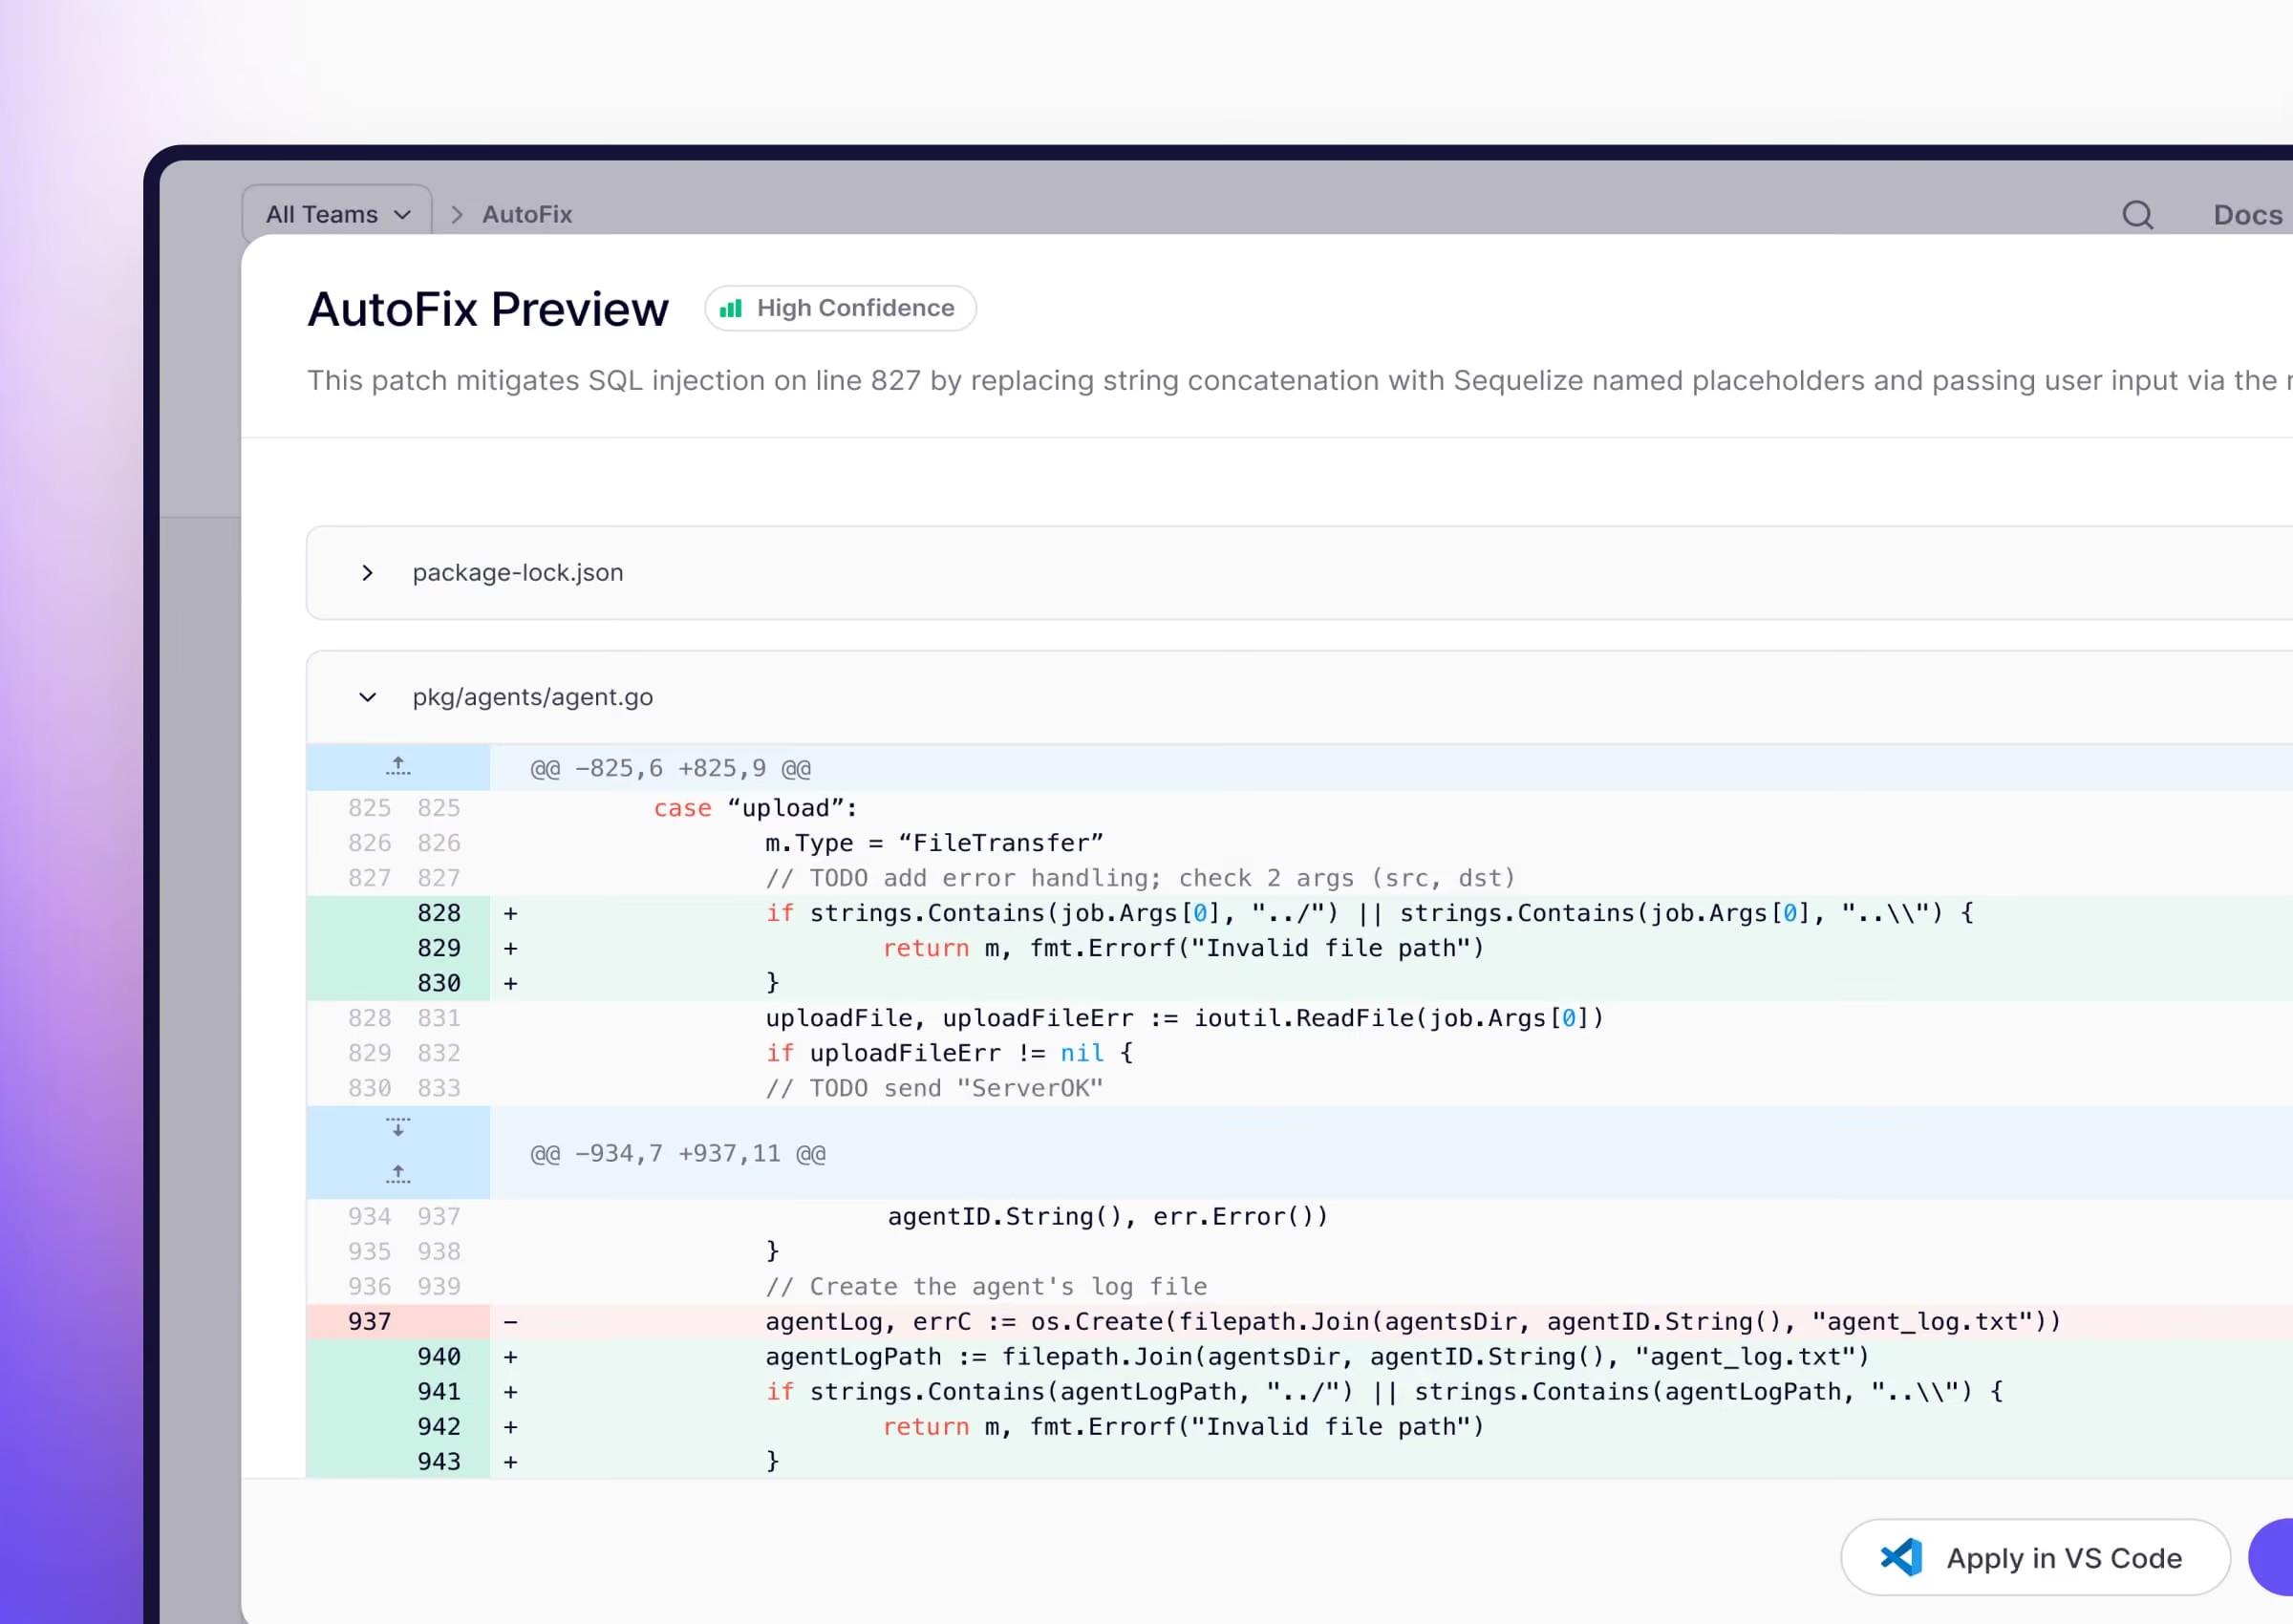
Ship secure code from prompt to production
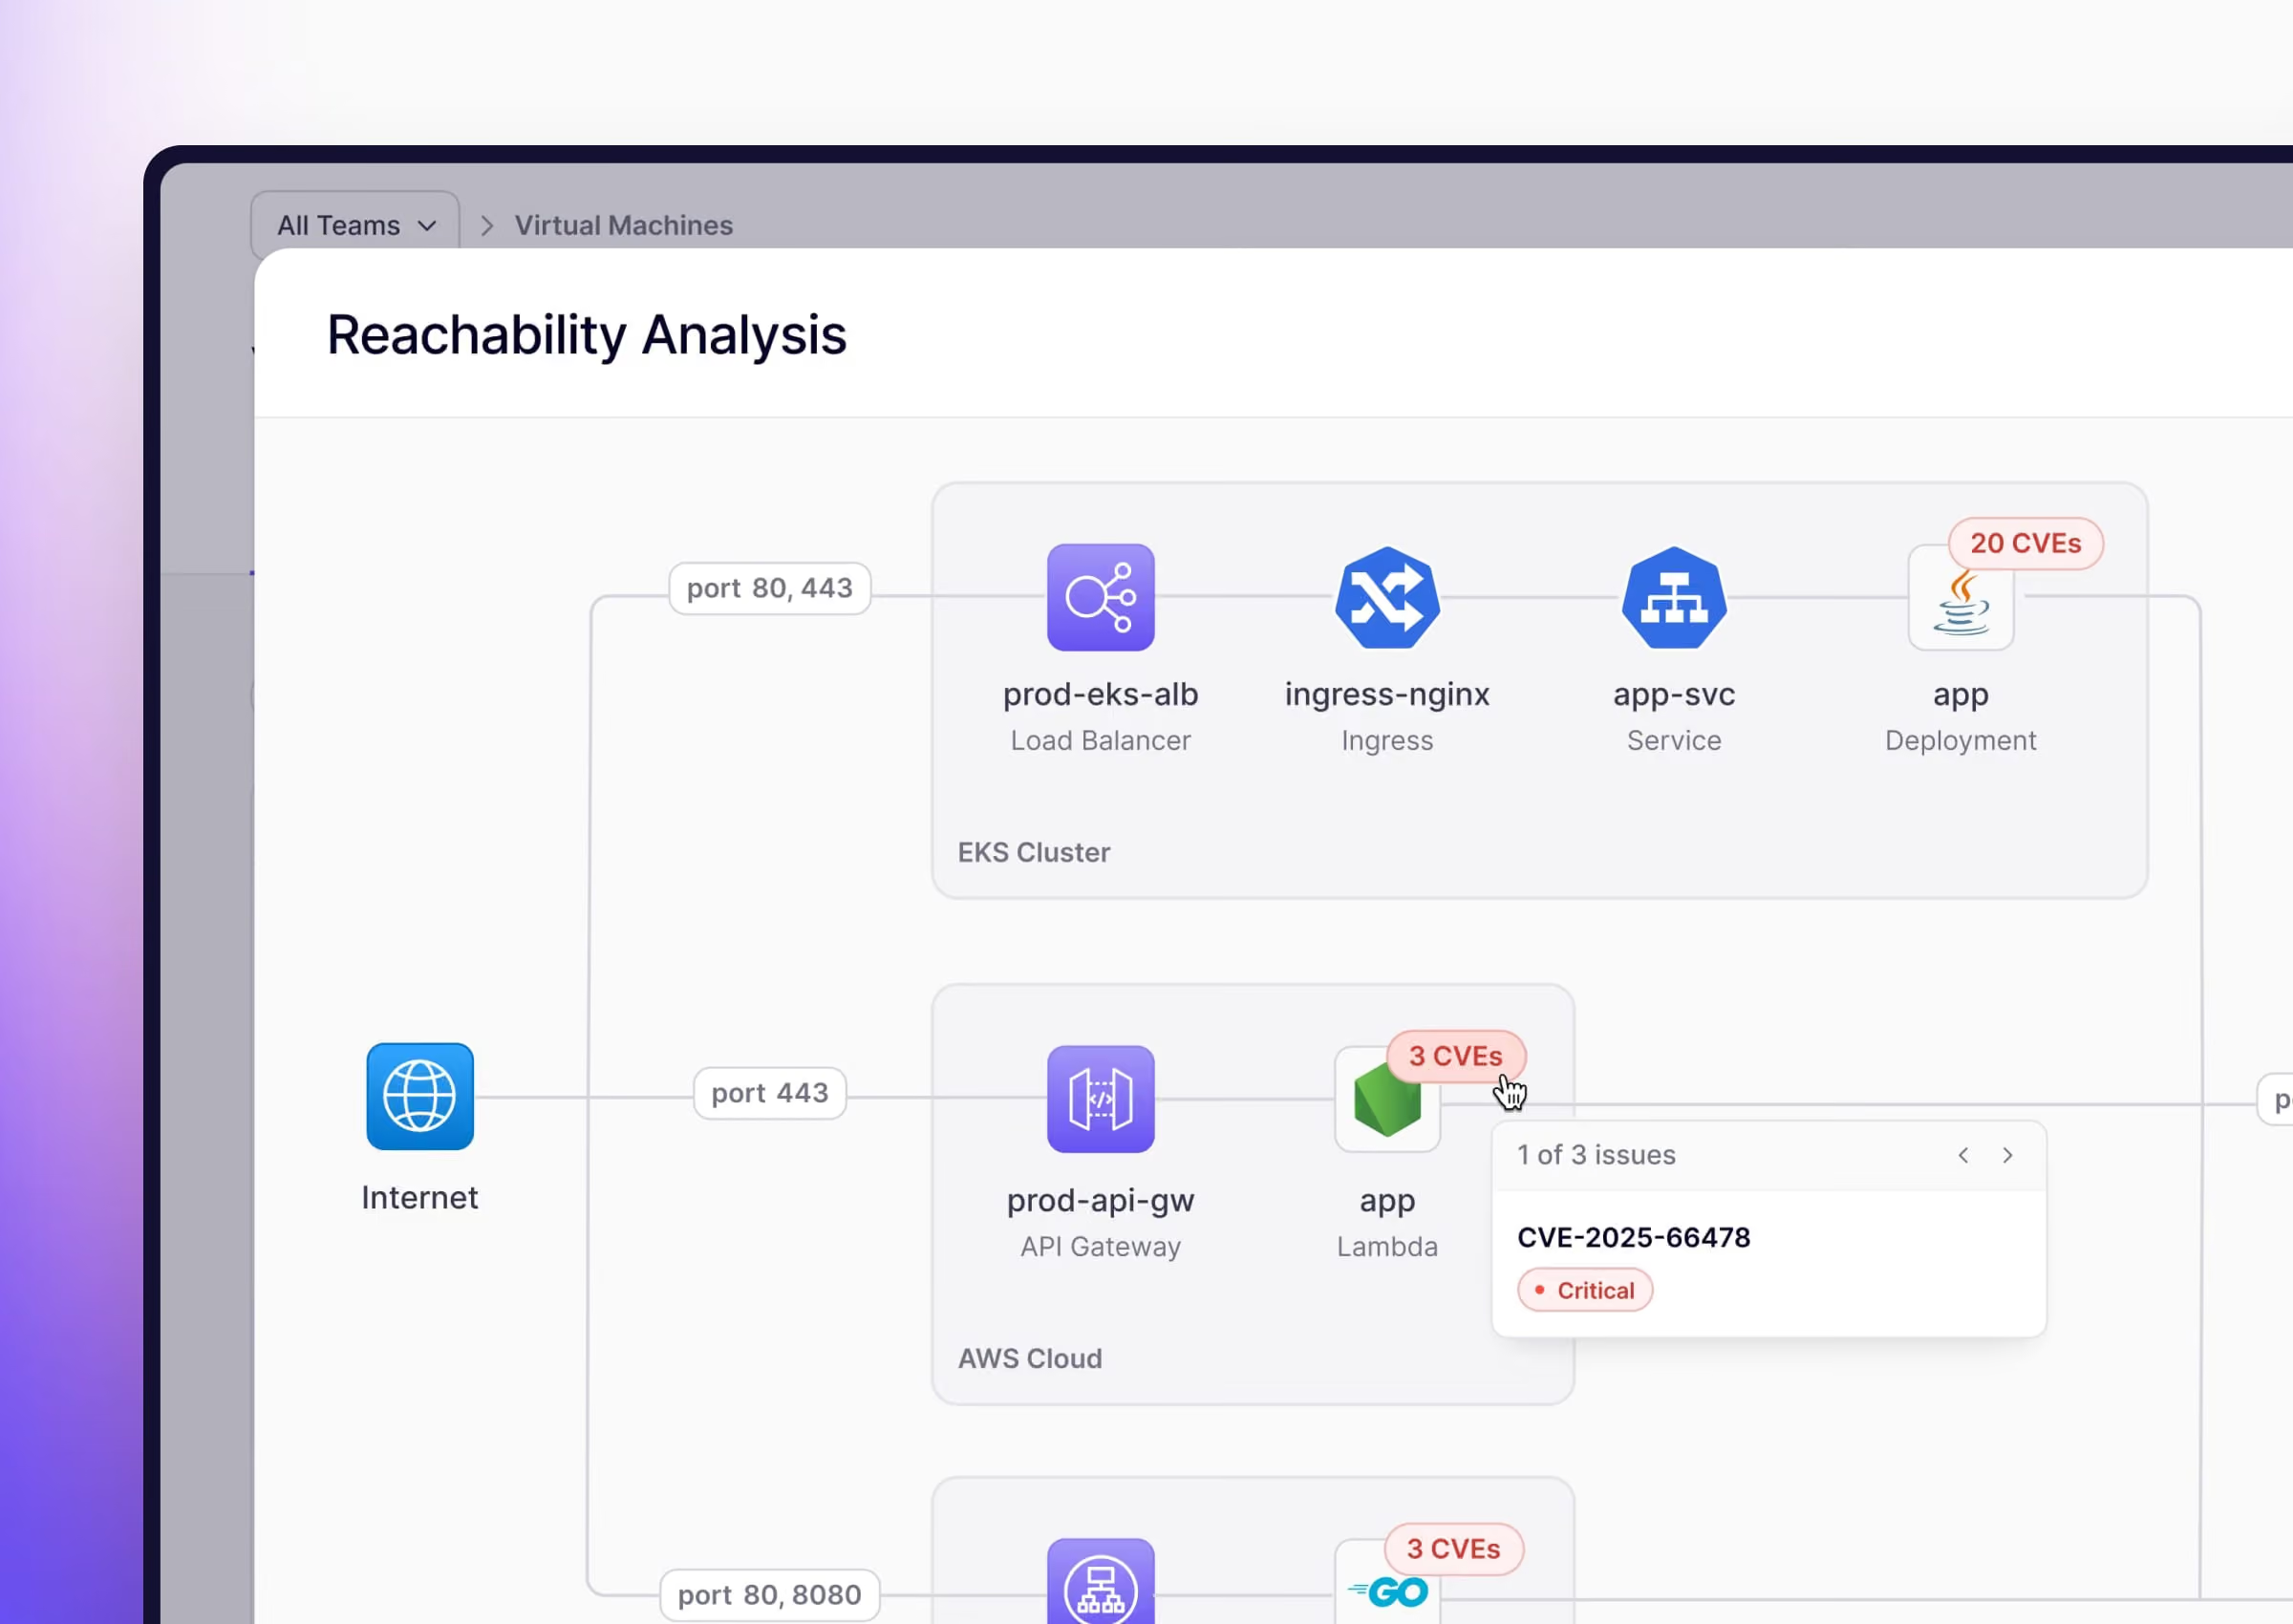
Secure your cloud with real-time visibility
Prove what’s exploitable. Fix what is.
Compliance coverage
Aikido performs checks and generates evidence for technical controls for ISO 27001:2022, SOC 2 Type 2, PCI, HIPAA and DORA.
Automating technical controls is a big step-up towards achieving compliance.
ISO 27001:2022

ISO 27001 is particularly relevant for FinTech companies. This globally recognized standard ensures that you have a systematic approach to managing sensitive company information, ensuring its confidentiality, integrity, and availability. Aikido automates a variety of ISO 27001:2022 technical controls.
DORA

The Digital Operational Resilience Act (DORA) is an EU regulation that requires financial institutions to strengthen their defenses against IT-related risks. Aikido helps with DORA compliance by automating the detection, and remediation of security vulnerabilities, enabling continuous monitoring, incident reporting, and management of 3d-party risks as required by the DORA regulation.
PCI

The Payment Card Industry Data Security Standard (PCI DSS) require a set of security standards designed to protect cardholder data during and after financial transactions. Any organization that handles credit card information must comply with these standards to ensure the secure processing, storage, and transmission of cardholder data. Aikido automates many technical controls.
OWASP Top 10

OWASP Top 10 aligns web application security practices with the most critical security risks identified by the Open Web Application Security Project (OWASP). The OWASP Top 10 is a widely recognized list of common vulnerabilities like injection flaws, broken authentication, and cross-site scripting (XSS), and achieving compliance involves addressing these vulnerabilities to secure web applications from common threats.
Pentest Reports
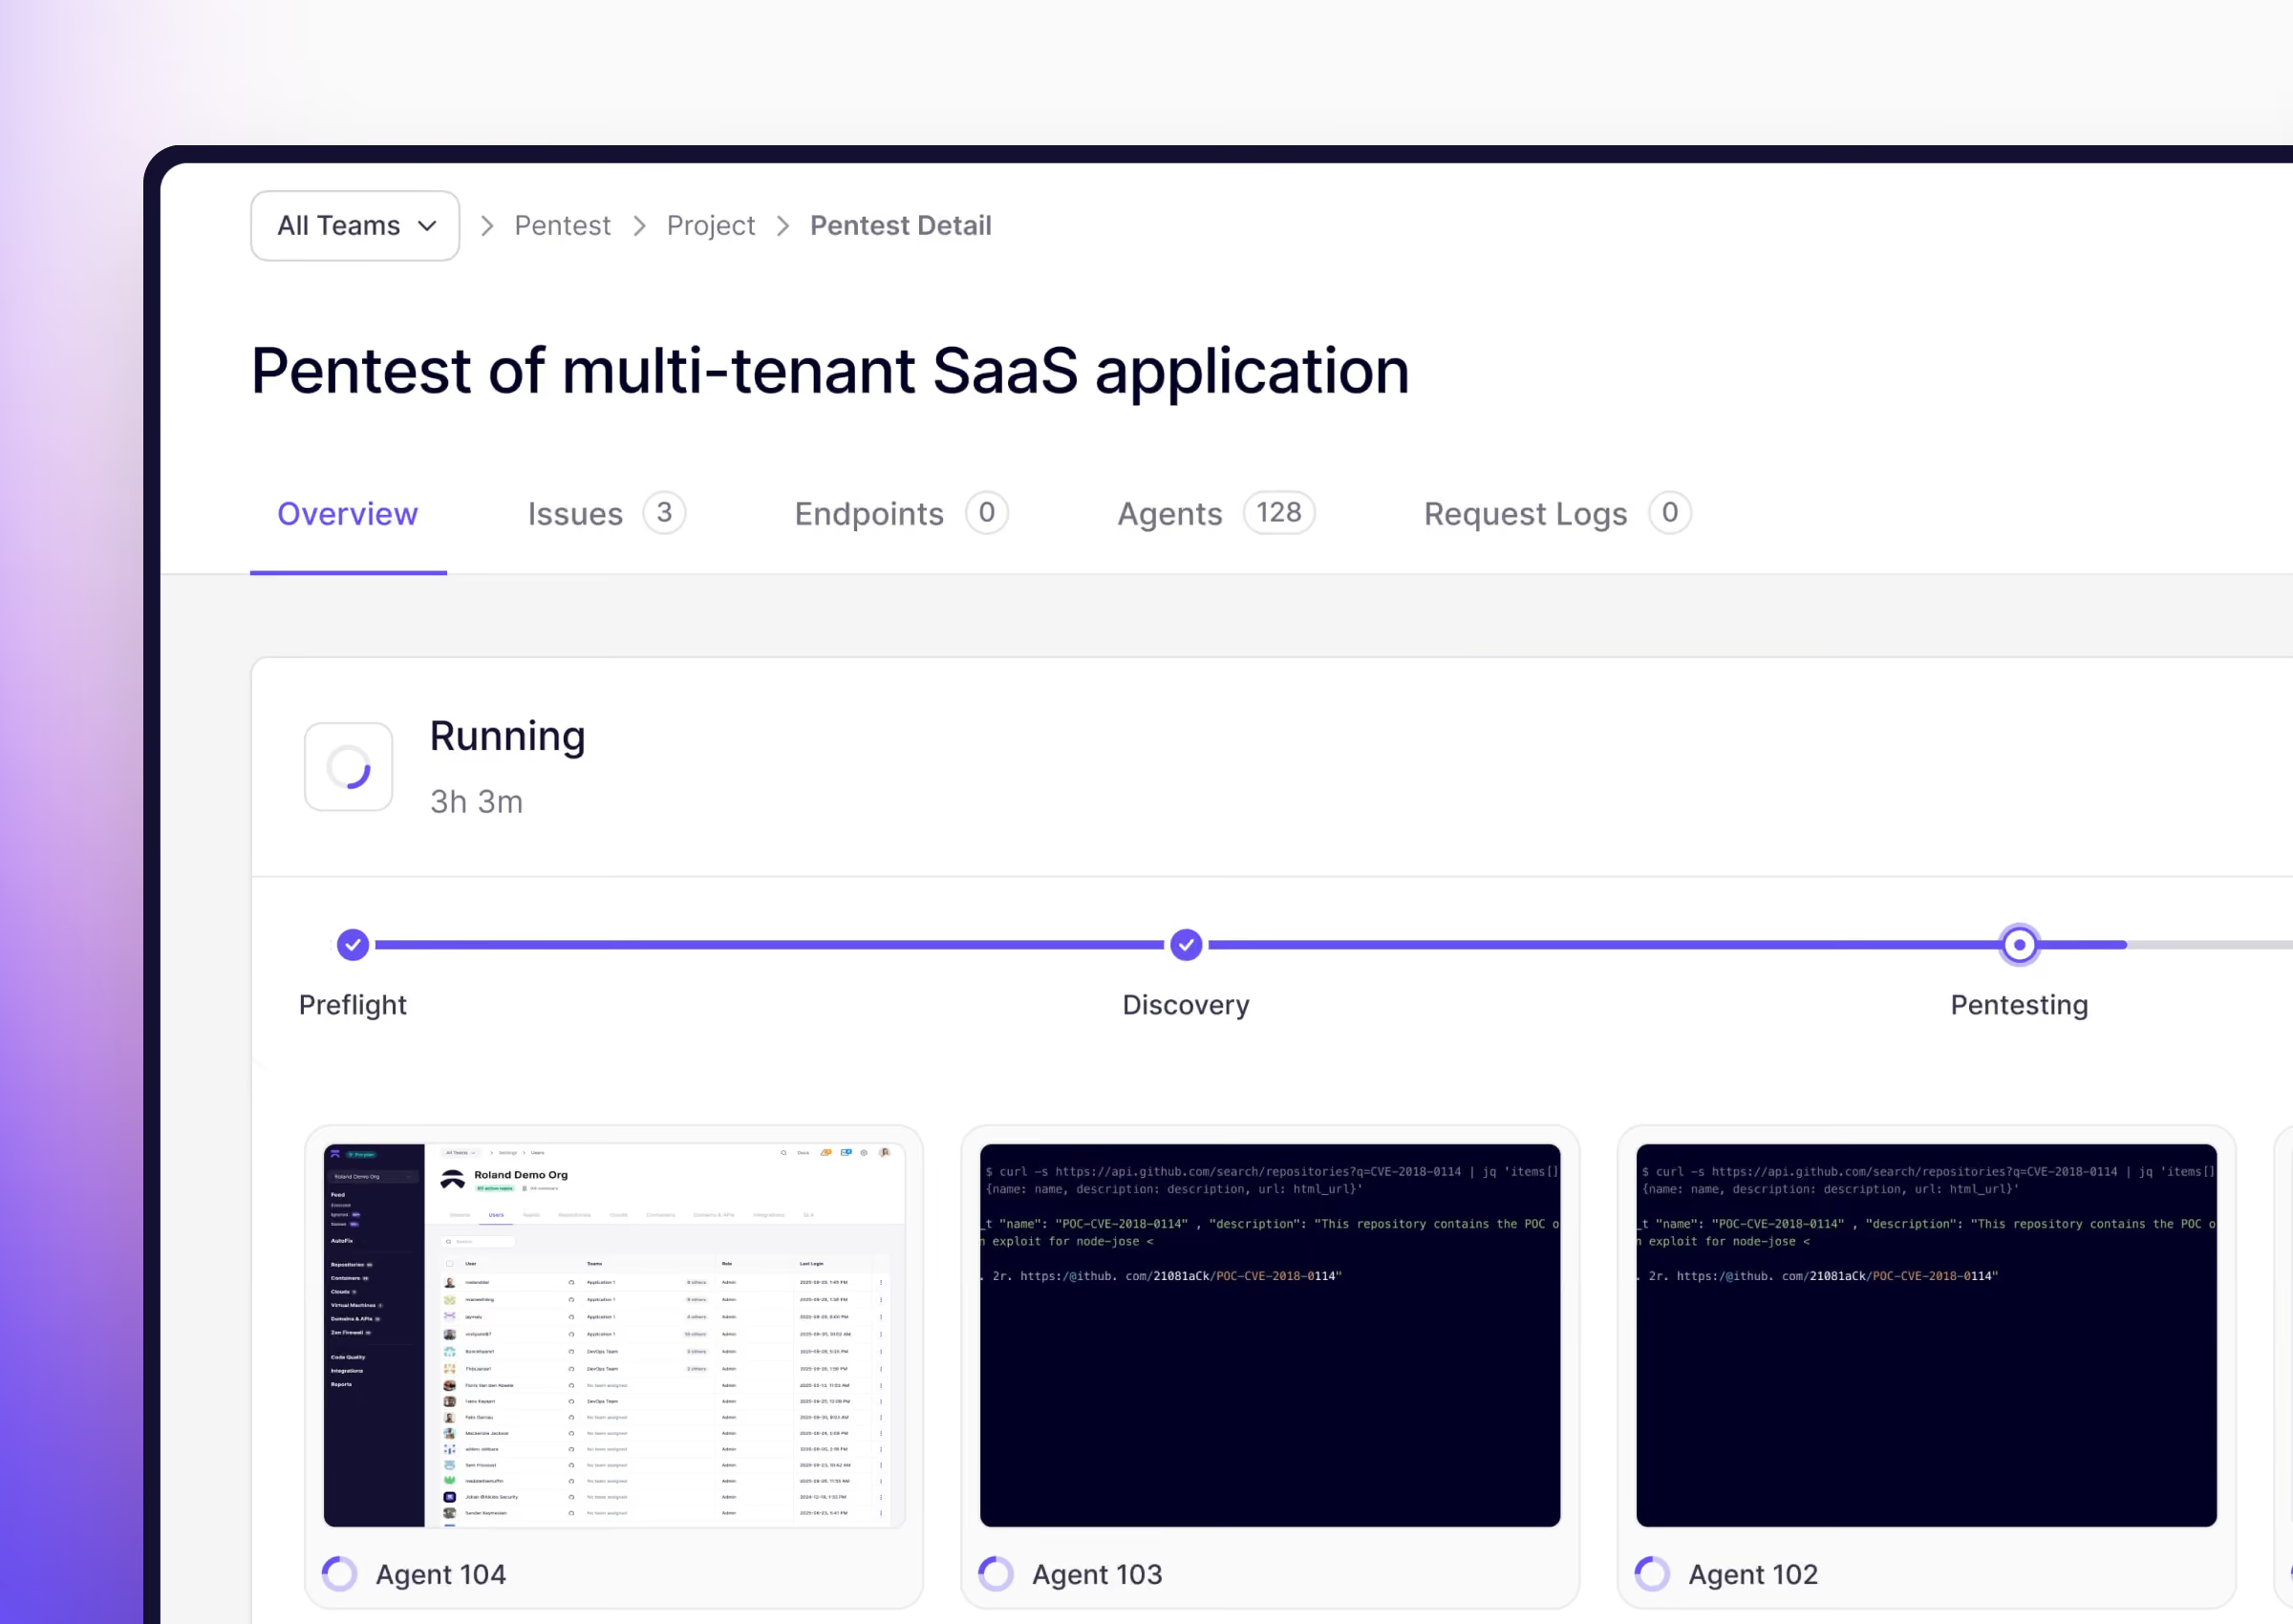
When Aikido Pentest finishes validation, it produces a detailed report that combines an executive overview with developer-first, actionable findings. The report is designed so security, engineering, and compliance teams can act on it immediately. You can also export tailored report types for auditors, management, or external parties in Pentest Reports.
SLA Insights and Issues
SLA Insights gives you visibility into how well your organization meets its remediation targets (MTTR Mean Time to Remediation). It focuses on response time, overdue issues, and overall remediation performance across severities.This report helps you understand whether security issues are being resolved within the timeframes you defined.
GDPR
The General Data Protection Regulation (GDPR) is the EU law that governs how organizations collect and process personal data of people in the EU. Among other requirements, it asks you to protect that data with appropriate technical and organizational measures. Aikido helps with the technical side by flagging security issues that could expose personal data, like leaked secrets or misconfigured cloud storage.
UK Cyber Essentials
Cyber Essentials is a UK government-backed certification, overseen by the National Cyber Security Centre (NCSC). It sets a baseline of protection against common internet attacks, built around five technical controls: firewalls, secure configuration, security update management, user access control, and malware protection. Some UK government contracts require it. Aikido flags code and cloud issues that affect these controls, like outdated packages with known vulnerabilities, so you can fix them before you apply.
SOC 2 Type 2

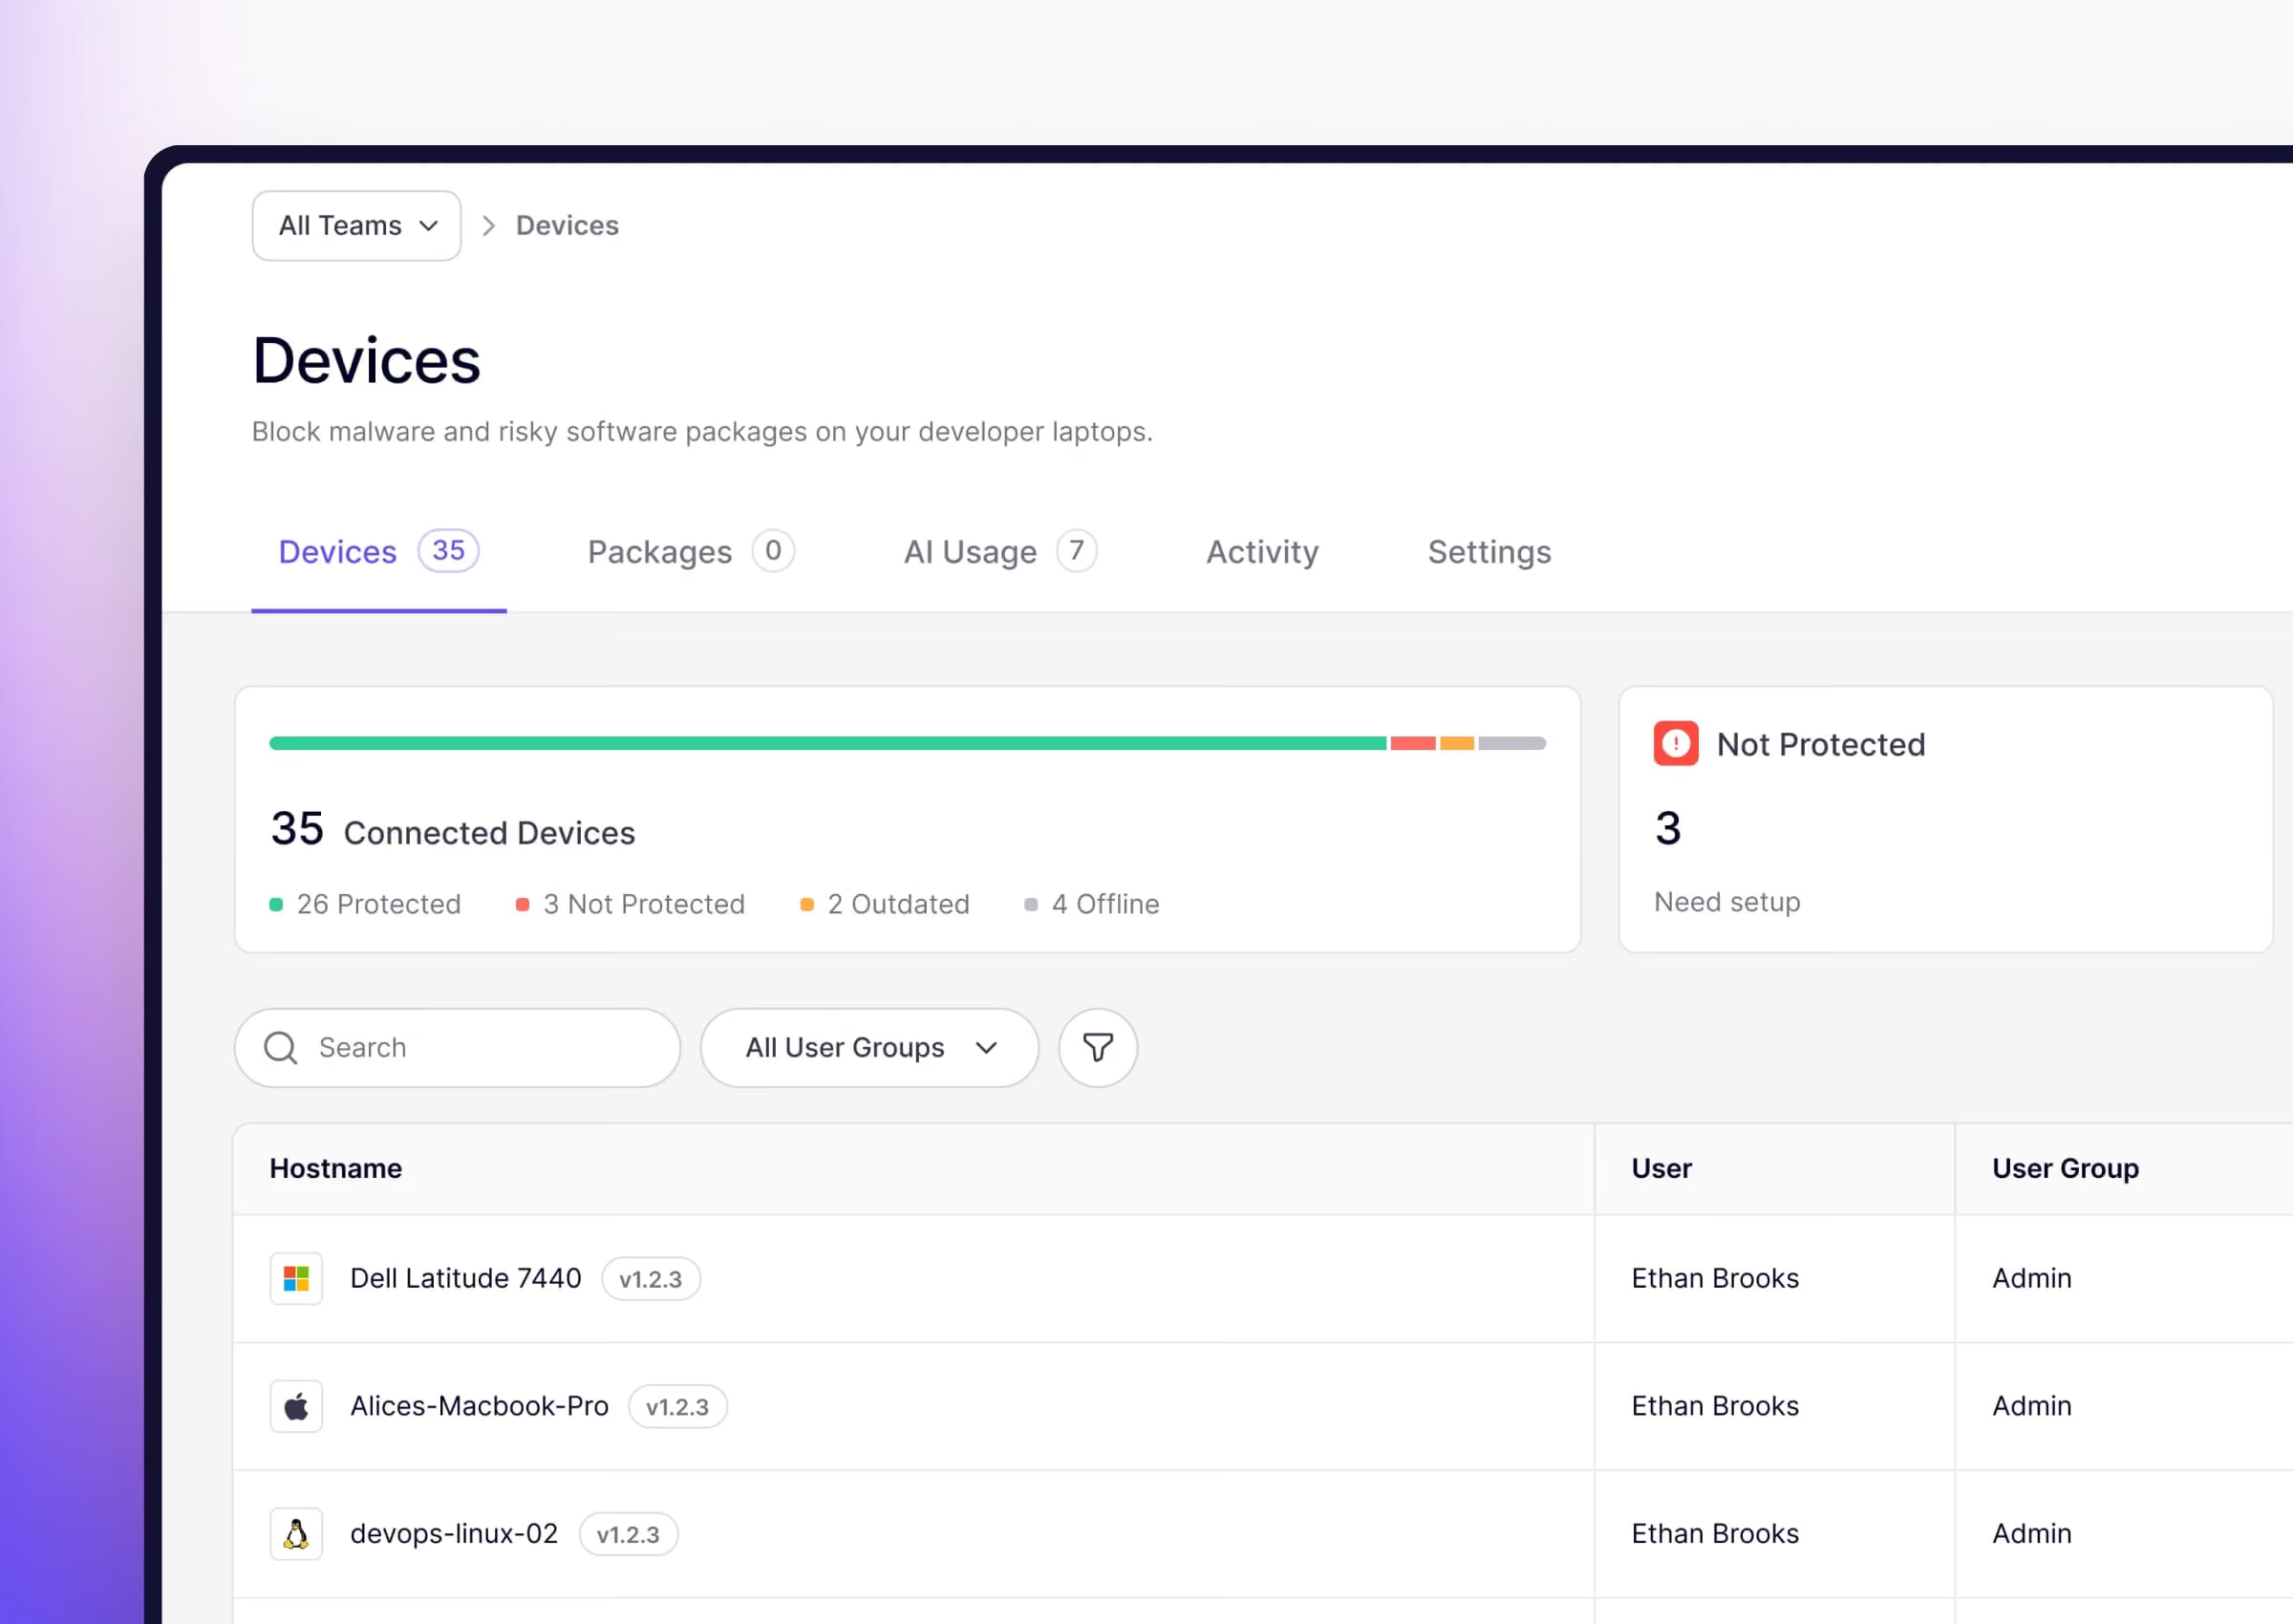
SOC 2 is a procedure that ensures your service providers securely manage your data to protect the interests of your organization and the privacy of its clients. Show your commitment to safeguarding data by complying with SOC2. Aikido automates all technical controls, making the compliance process much easier.
HIPAA

The Health Insurance Portability and Accountability Act sets national standards for protecting sensitive patient information in the healthcare industry. It mandates safeguards for the privacy and security of health data, ensuring that healthcare providers, insurers, and their business associates implement measures to protect patient information from unauthorized access and breaches.
NIS2

The Network and Information Security Directive (NIS2) is a European Union regulation aimed at improving the cybersecurity of critical infrastructure sectors. A wider range of industries must follow cybersecurity rules and it improves teamwork between EU countries to protect against cyber threats. Organizations in sectors like healthcare, energy, and transportation must meet these standards.
CIS

The Center for Internet Security (CIS) sets best practices and security benchmarks to help organizations improve their cybersecurity defenses by offering specific guidelines for securing systems, networks, and applications. Achieving CIS compliance helps reduce security risks and ensures a standardized level of protection against cyber threats. Aikido reports on CIS Controls v8 compliance progress, based on your connected clouds and code repositories.
NIST
NIST 800-53 is a catalog of security and privacy controls from the US National Institute of Standards and Technology. It's required for US federal information systems, and many government contractors and regulated companies use it as their control baseline. Aikido groups your security findings by NIST 800-53 control family, so you can see which areas need the most work.
HITRUST
The HITRUST Common Security Framework (CSF) is a certifiable framework that brings requirements from standards like HIPAA and ISO 27001 into one set of controls. It's common in US healthcare, where hospitals and insurers often ask vendors for HITRUST certification before sharing patient data. Aikido reports on the HITRUST technical controls it can check automatically, which gives you a head start on the evidence your assessor will ask for.
ENS
The Esquema Nacional de Seguridad (ENS) is Spain's National Security Framework. Spanish public sector bodies must comply with it, and so must the companies that provide them with IT services. ENS scales its security measures to how critical each system is. Aikido shows which ENS technical measures your setup already meets and which need work, ahead of your assessment.
Get your exclusive Aikido | Hexa offer
We're offering discounts of up to 50% for the first year.