

Somewhere in your Git history, a credential is hiding that shouldn't be there. GitHub's own data shows more than 39 million secrets leaked across the platform in 2024 alone, and AI-assisted development is only driving that number up. More code is being written, faster, with less review, and developers routinely override AI warnings about hardcoded credentials to keep momentum. Once a credential lands in a public repo, bots can find and exploit it within minutes.
Secret scanning tools exist to find what shouldn't be there, but the category has shifted in the last year. Token efficiency scanning has set a new accuracy bar that entropy-based tools haven't matched, live validation has gone from rare to expected, and there's a new open-source leader. This guide covers what works now and what's been left behind.
TL;DR
Aikido Security is the pick if you want secrets detection as part of a complete security platform. It runs the Betterleaks engine for detection and bundles it alongside best-in-class SAST, SCA, AI Pentesting, container scanning, and cloud security in one console. Betterleaks is the pick if you want the strongest open-source scanner you can run yourself. Built by the original author of Gitleaks, it replaces entropy with token efficiency scanning (98.6% recall vs 70.4% on CredData) and adds configurable validation that confirms whether a credential is actually live.
What are secret scanning tools?
Secret scanning tools search code, configs, Git history, and CI pipelines for passwords, API keys, or other sensitive data that may have been accidentally exposed. They combine pattern matching against known credential formats (e.g., an AWS key has a recognizable prefix) with statistical filtering to catch credentials that don't match a known pattern.
How to choose the right secret scanning tool
A few things actually matter when picking one:
- Validation logic: Does the scanner confirm whether a detected secret is live, or just flag the pattern? The best implementations let you configure validation rules yourself, rather than hardcoding which credential types get checked.
- Filtering: How does the scanner decide which candidate strings are actually secrets? Entropy-based filtering misses around 30% of real secrets and produces more false positives. Token efficiency scanning, AI triage, and provider-specific pattern logic each reduce that gap differently.
- License and cost: Open-source MIT is the lightest. AGPL has redistribution obligations. Commercial pricing varies from per-developer to per-committer to enterprise sales.
Top secret scanning tools for 2026
Here's a quick comparison of the main secret scanning tools by validation, filtering, and cost.
1. Aikido Security
Secrets detection powered by Betterleaks, the Gitleaks successor by the same author, 98.6% recall vs 70.4%
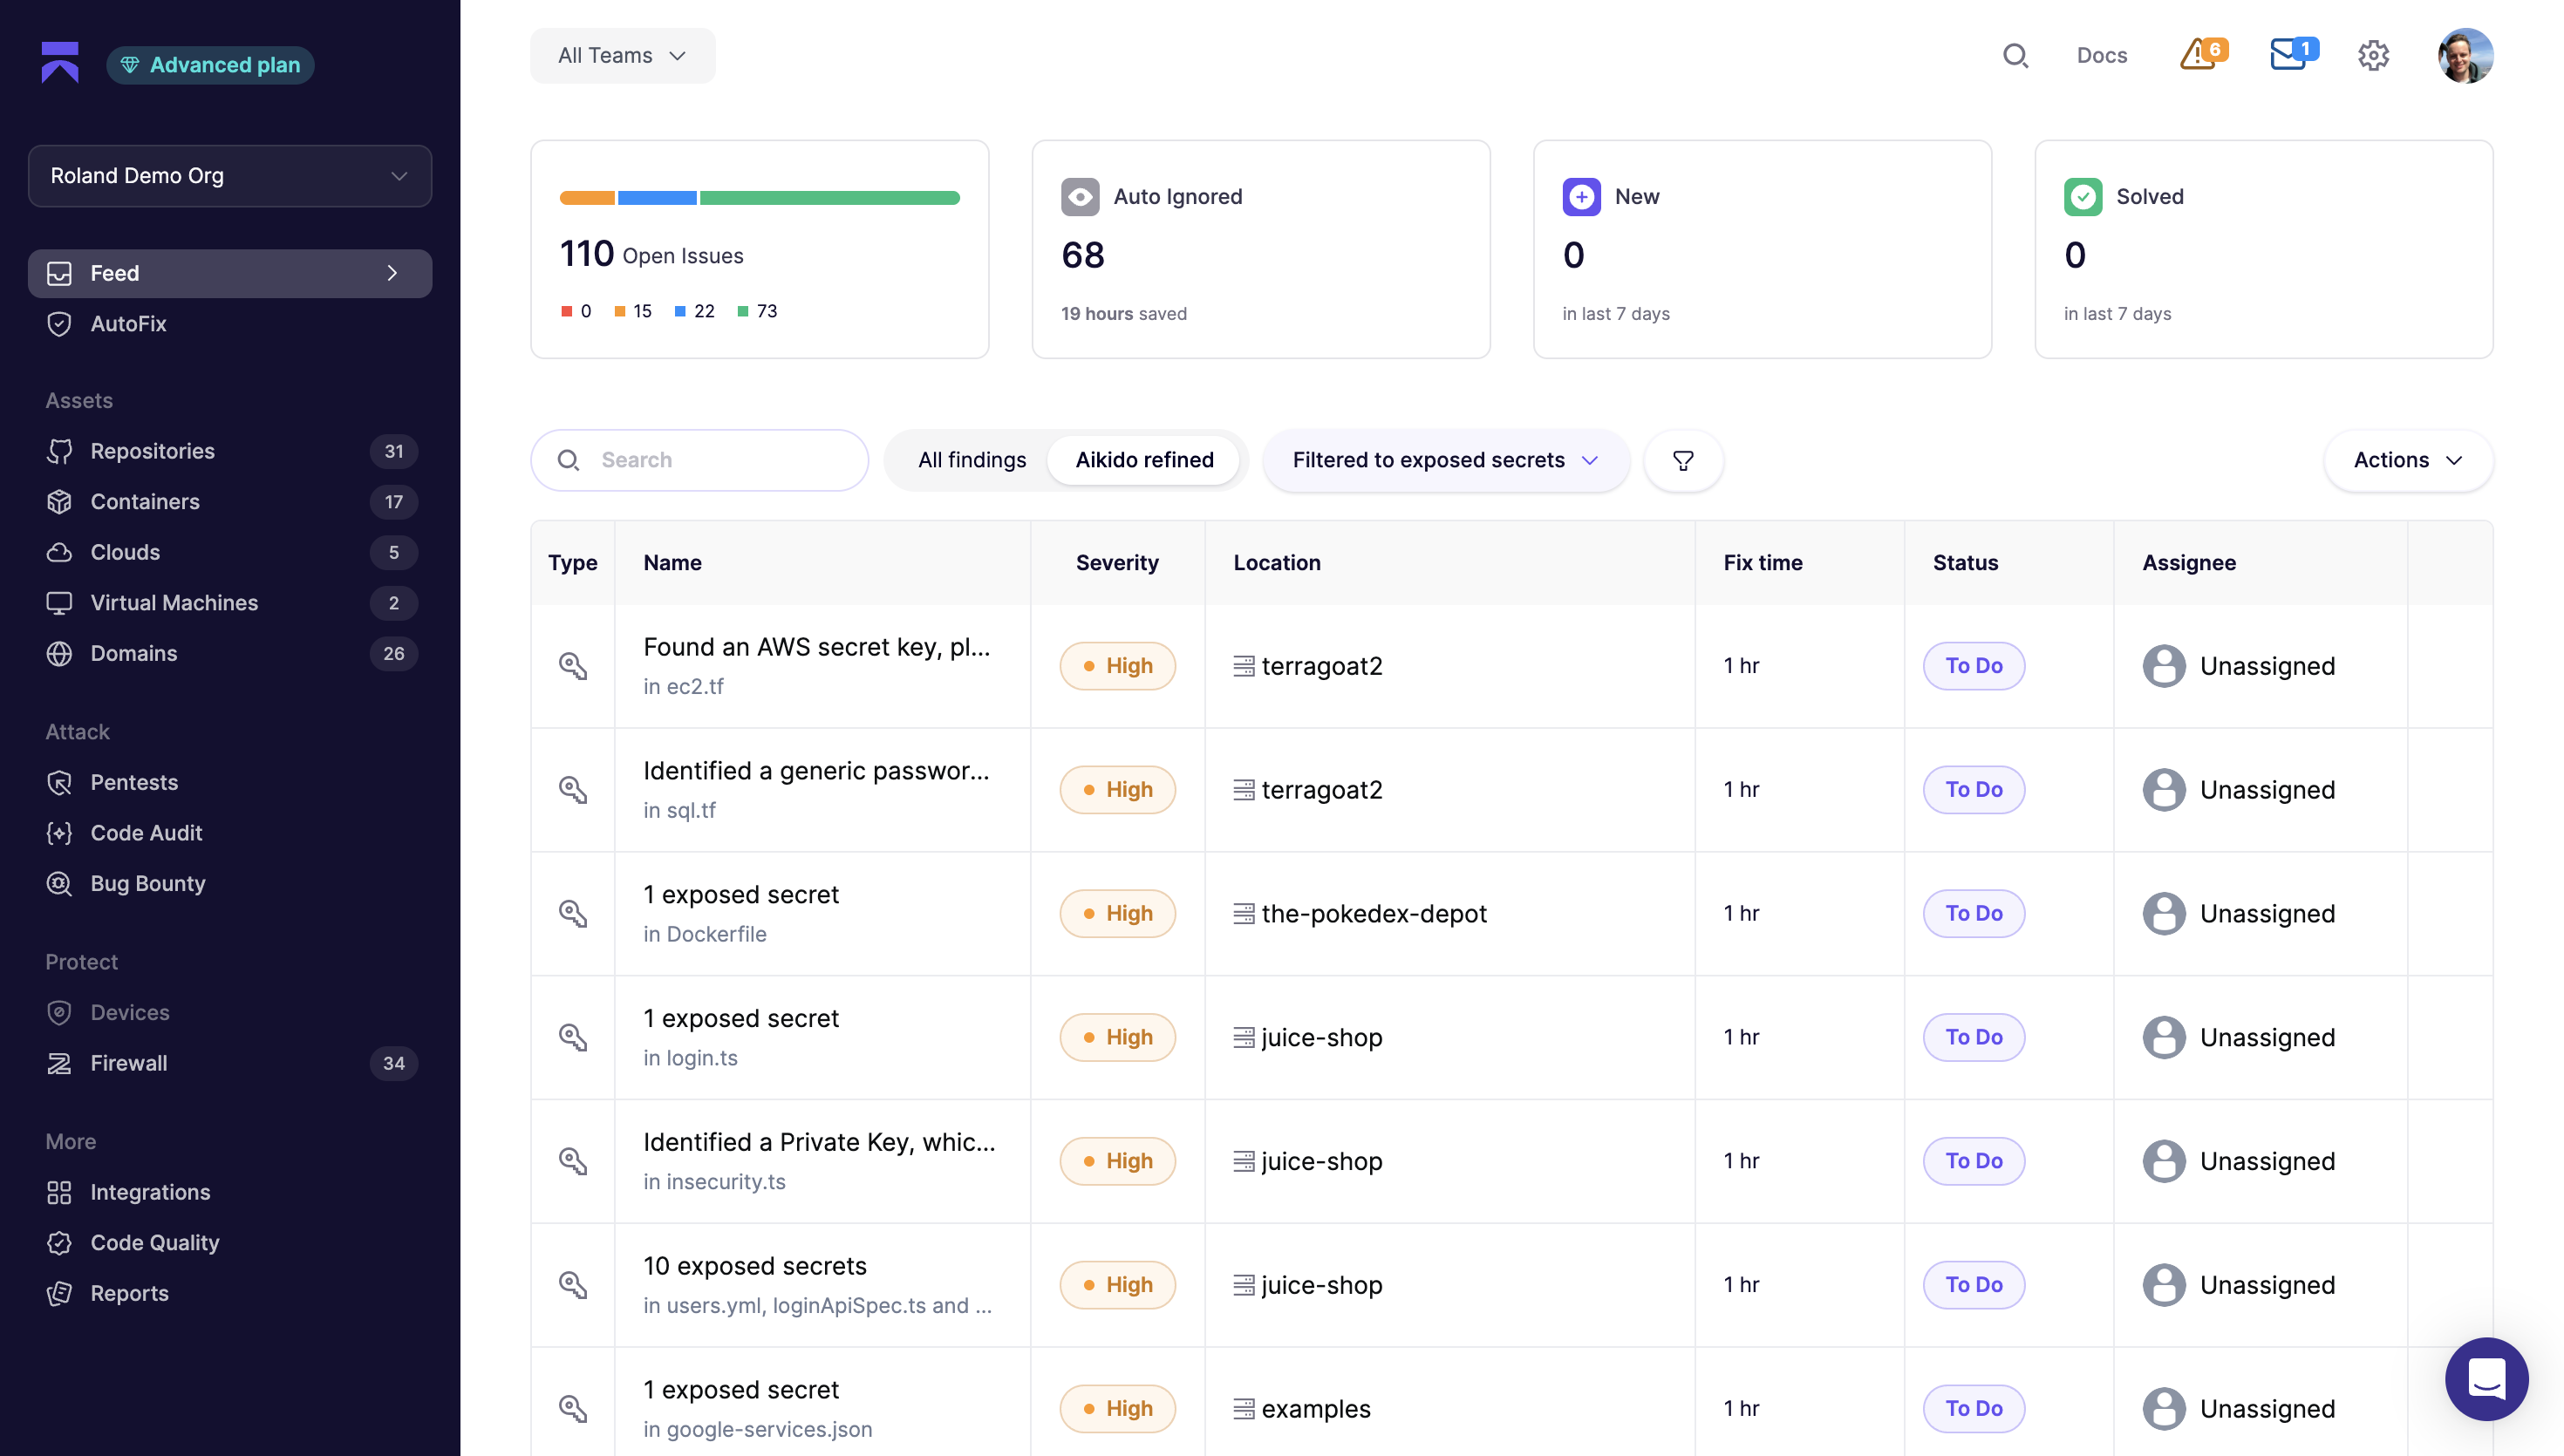
Aikido Security's secrets detection is part of a broader security platform rather than a standalone tool. It checks code repositories and Git history for exposed credentials, surfaces findings directly in the IDE, and integrates into CI pipelines to catch secrets before code is merged or deployed. Liveness detection verifies whether a flagged credential is still active before it reaches a developer. The platform uses the Betterleaks detection engine under the hood, which means Aikido inherits the token efficiency approach (98.6% recall vs 70.4% for entropy on CredData) and configurable validation rather than depending on pattern matching alone.
Where Aikido Security differs from a standalone tool is scope. Secrets detection sits alongside SAST, SCA, AI Pentesting, Device Protection, IaC security, container image security, and cloud security posture management in a complete platform. Consolidation reduces the number of integrations to manage and keeps findings in one place. It also means you're not relying on a single open-source maintainer for uptime or updates.
Key features:
- Betterleaks engine under the hood for token efficiency scanning and configurable validation, managed for you.
- Liveness detection verifies whether exposed credentials are still active, so developers only see findings that matter.
- IDE, CI, and Git integration with pre-commit blocking, so secrets get caught before they're merged.
- Optional Git history scanning to find credentials in old commits, branches, and tags.
- AutoFix opens PRs to remove hardcoded secrets and updates CI/CD variables automatically.
- Coverage across SAST, SCA, IaC, container image scanning, DAST, AI Pentesting, Device Protection, and cloud posture in the same console.
- Compliance-ready reporting for SOC 2, ISO 27001, and other frameworks, with the audit trail in place.
- Secrets AutoTriage filters and ranks findings by real risk. It drops test files and placeholder values before they reach your feed, then checks whether each remaining secret is live and what it can access. Expired or rotated credentials get downgraded, and active keys with write or delete scopes move to the top of the queue. Every verdict is logged in a triage history, so you can see why a finding moved. Available on Pro and Advanced plans.
Best for: Teams wanting comprehensive security with minimal overhead. Aikido is particularly valuable for organizations that need secret scanning as part of a broader security program, not as an isolated tool.
Pricing: Free tier available with generous limits, then transparent per-developer pricing that includes all security features, not just secret scanning.
{{cta}}
2. Betterleaks
Betterleaks is the Gitleaks successor by the same author, 98.6% recall vs 70.4%
Betterleaks is the direct successor to Gitleaks, built by the same author. Zach Rice wrote the first lines of Gitleaks in 2018, watched it grow to tens of millions of downloads and become the default open-source secrets scanner, then lost full control over the repo and name. He started Betterleaks in early 2026 with the ambition of building the best open-source secrets scanner. It's MIT-licensed, governed independently, sponsored by Aikido without being dependent on it, and maintained by Rice alongside three other engineers with backgrounds at Red Hat, Amazon, and RBC.
It's also a drop-in replacement for Gitleaks. Existing CLI flags and config files work without modification, so switching is a binary swap rather than a migration project. What you get for that swap is materially better detection, live validation in the open-source tier, and a project that's actively maintained. The switch costs nothing, and existing Gitleaks configs work unchanged.
Key features:
- Token Efficiency Scanning uses BPE tokenization to measure how "rare" or non-human a string is, enabling it to filter candidate secrets.
- Configurable validation. Rules written in Common Expression Language fire HTTP requests against detected credentials to confirm whether they're still live.
- Drop-in Gitleaks replacement. Existing CLI flags and configs work unchanged.
- Doubly and triply encoded secret detection: a common obfuscation technique most scanners miss.
Best for: Developers and small teams that need fast, accurate prevention at commit and CI time, and teams already using Gitleaks that want better detection without changing their workflow.
Pricing: Free, MIT.
3. Gitleaks
Zach Rice launched Gitleaks in 2018 as a side project, watched it grow to tens of millions of downloads, the most-starred secrets scanner on GitHub, and the default choice in security programs at companies like GitLab and Red Hat. For a long time, it was simply what you ran.
The honest update for 2026 is that active development has largely moved on. Security patches still ship for Gitleaks, but new features and detector updates have shifted to Betterleaks. Rice joined Truffle Security in 2023, where his focus shifted to TruffleHog, and he has been open about no longer having full control over the Gitleaks repo and name. He started Betterleaks in early 2026 as the direct successor, and it is the natural choice for people looking to migrate. It has the same author, backwards-compatible CLI and configs, materially better detection, and live validation in the open-source tier.
Key features:
- Git repository and history scanning with rules for hundreds of credential types.
- Entropy-based detection for credentials that don't match known patterns.
- CLI and CI integration including GitHub Actions, GitLab CI, and pre-commit hooks.
- Configurable detection rules via TOML config files.
- Wide ecosystem adoption with tens of millions of downloads and existing playbooks across the industry.
Pain points: Entropy-based filtering achieves around 70.4% recall against the CredData benchmark, meaning roughly a third of real secrets slip through. There's no validation, so every finding requires manual triage to determine whether the credential is actually live. Project development has slowed, and the original author now maintains Betterleaks as the active successor.
Best for: Existing Gitleaks installs that work and don't need to change yet.
Pricing: Free, MIT.
4. GitGuardian
GitGuardian is a dedicated secrets security platform with mature non-human identity (NHI) governance alongside it. Detection quality is high, the NHI workflows are well-developed, and the remediation flows are built for teams running secrets as a security program in its own right rather than as one finding type among many.
Key features:
- Deep Git history analysis can scan your entire repository history to find secrets in old commits.
- Advanced secret classification goes beyond simple detection to categorize secrets by type, sensitivity level, and potential impact.
- Automated incident response workflows can trigger secret rotation, send alerts to security teams, and create tickets with detailed remediation steps. For certain services, GitGuardian can automatically revoke exposed credentials.
- Compliance dashboard provides audit-ready reports showing secret detection coverage, incident response times, and policy compliance metrics. This is particularly valuable for enterprises that need to demonstrate security controls.
- Developer education features help teams understand why certain patterns are flagged as secrets and provide training to prevent future exposures.
Pain points: GitGuardian doesn't cover SAST, SCA, IaC, container scanning, or cloud posture in the same platform, so teams that need those capabilities end up running multiple tools alongside it. Pricing is free under 25 developers but moves to a per-developer model above that, which can be hard to justify on top of the rest of an AppSec stack as teams grow. Detection is also still entropy-driven rather than token-efficiency-based, which means more tuning to keep false positives down than a tool like Betterleaks requires out of the box.
Best for: Security teams running secrets and NHI governance as a dedicated program with its own owners and budget.
Pricing: Freemium model with limited scanning, paid tiers based on repository count and advanced features.
5. GitHub Advanced Security
GitHub Advanced Security provides native secret scanning for GitHub repositories, making it the natural choice for teams heavily invested in the GitHub ecosystem. The integration depth is a selling point since it's built directly into the platform.
Key features:
- Native GitHub integration means secret scanning results appear directly in your repository's security tab, pull requests, and can trigger GitHub Actions workflows. No external tools or additional authentication required.
- Push protection blocks commits containing known secrets before they land, including base64-encoded secrets by default since October 2025.
- Validity checks for supported providers confirm whether a detected credential is still live. Partner integrations with AWS, Google Cloud, Microsoft Azure, and dozens of others mean providers get notified automatically and can revoke exposed credentials.
Pain points: GitHub Secret Protection only works on GitHub-hosted repositories. If you host code in GitLab, Bitbucket, Azure DevOps, or any non-GitHub system, it doesn't apply. Remediation is campaign-based with no autofix for secrets. Broader code security requires GitHub Code Security as a separate paid add-on, and since April 2025 both are billed as per-committer subscriptions on top of an existing GitHub plan, which adds up for teams that need both.
Best for: Teams using GitHub Enterprise that want comprehensive security features with zero external dependencies. Particularly valuable for organizations that prioritize keeping their security tools within their existing platform ecosystem.
Pricing: Included with GitHub Enterprise subscriptions, pay-per-repository for individual features on other plans.
6. Spectral
Spectral started as an independent developer security startup before Check Point acquired it in 2022 and folded it into the CloudGuard platform. It covers secrets scanning alongside IaC and SCA, and ships SPEQL, a YAML-based query language for writing and sharing custom detectors without modifying the core engine.
Key features:
- SPEQL custom detectors let teams define their own secret patterns and detection rules in YAML, with 2,000+ built-in detectors shipping out of the box.
- Multi-environment scanning covers code repositories, CI/CD pipelines, container registries, cloud configurations, and even runtime environments.
- Policy-as-code lets teams define custom rules for secret handling, including exceptions for specific contexts, severity levels based on environment, and automated remediation workflows.
- DevOps integration includes plugins for popular tools like Jenkins, GitLab CI, Azure DevOps, and Kubernetes. Spectral can scan container images, Helm charts, and infrastructure-as-code templates.
- Collaborative triage features help security and development teams work together on secret remediation, with clear ownership assignment and progress tracking.
Pain points: Spectral focuses on detection rather than validation, so confirming whether a flagged credential is still live needs a separate step in the workflow. Filtering relies on pattern matching and custom SPEQL rules rather than the kind of statistical approach that meaningfully reduces noise. Pricing and support go through Check Point's enterprise sales process, which is a different buying experience than the self-serve models offered by most other tools in this list. And since the acquisition, the pace of developer-facing innovation has reflected Check Point's broader focus on network security, which raises a fair question about whether the roadmap will keep pace with the rest of the category.
Best for: DevOps teams that need sophisticated policy management and want to reduce the operational overhead of managing secrets across complex, multi-environment deployments.
Pricing: Contact-based pricing focused on enterprise customers with significant infrastructure complexity.
7. TruffleHog
TruffleHog is an open-source secret scanner that offers live credential verification across 800+ detector types. It calls the provider's API to confirm whether a flagged secret still works, which matters because most credentials in old commits are already expired. TruffleHog tells you which ones aren't, narrowing the remediation queue significantly.
Key features:
- Live credential verification across 800+ supported types. API calls confirm whether a detected secret is still active before it reaches a developer.
- Multi-source scanning beyond Git. TruffleHog covers S3 buckets, Docker images, Slack, Jira, Confluence, and GitHub and GitLab orgs including PR comments and issues.
- Entropy-based detection catches credentials that don't match known patterns.
- Git history analysis can scan through entire repository histories to find secrets in old commits, branches, and tags.
- Custom integrations are possible since the source code is available. Organizations can extend TruffleHog to handle proprietary secret formats or integrate with internal systems.
Pain points: Entropy-based filtering produces more noise than token efficiency approaches like Betterleaks, which means more tuning to keep false positives manageable. Generic and custom credential types aren't detected by default, which is a gap for teams with internal services. There are no dashboards, suppression workflows, or audit trails without TruffleHog Enterprise. And the AGPL-3.0 license creates redistribution obligations if you modify and distribute the tool, which is worth checking with legal before going to production.
Best for: Teams that want live credential verification across sources beyond Git, including collaboration tools and cloud storage, and are comfortable with the AGPL license.
Pricing: Free and open-source under AGPL-3.0. TruffleHog Enterprise is quote-based.
8. Cycode
Cycode is an application security posture management (ASPM) platform, and secrets detection is one engine inside it. The pitch is reach. Beyond source code, Cycode scans the places credentials end up after someone pastes them into a thread, including Slack, Microsoft Teams, Jira, Confluence, and S3 buckets. It runs alongside Cycode's own SAST, SCA, IaC, and container scanning.
Key features:
- Validity checks on detected secrets, so findings arrive marked active or inactive.
- An in-house ML model for unstructured secrets that don't match a known provider pattern.
- A classifier agent that works through findings labeled generic and feeds what it learns back into detection. Cycode says its training data comes from public sources, not customer code.
- Pull request blocking to stop new secrets before merge, with remediation surfaced in developers' existing tools.
- Risk-based prioritization so the most exposed secrets get fixed first.
Pain points: There's no public pricing, so evaluating it starts with a sales call. Generic-secret detection runs on a proprietary model, which makes a disputed false positive hard to reason about. The product is also built for org-wide ASPM rollouts, which is a lot of platform to adopt if secrets scanning is the job you're hiring for.
Best for: Enterprises consolidating AppSec under an ASPM platform that want secrets coverage extended into collaboration tools.
Pricing: Quote-based through sales.
9. Nightfall
Nightfall is a data loss prevention (DLP) platform, and it treats secrets as one class of sensitive data alongside PII, PHI, and payment card data. It connects to SaaS apps directly by API with no agents or proxies, applying the same detection rules across GitHub, Slack, Google Drive, Jira, and Confluence. If the credential you're worried about is an AWS key in a Slack DM rather than a config file, that's the gap Nightfall was built for.
Key features:
- LLM and computer vision detectors that catch credentials inside screenshots and attachments, not just plain text.
- Active-key validation for supported vendors, with each finding returned as active, expired, or unverified.
- Real-time scanning on push plus full commit-history scans for GitHub repos.
- Alerts to Slack or a SIEM, and Jira tickets for remediation.
- Developer APIs for scanning text and files inside your own applications.
Pain points: Nightfall is a DLP product first, and its GitHub integration shows it. Nightfall describes the interface as built for security admins, and detection triggers on push, so findings reach the security team before they reach the developer who committed the key. There's no SAST or SCA, so it runs alongside an AppSec stack rather than replacing any of it. Validation only covers supported vendors, and everything else comes back unverified.
Best for: Security and compliance teams whose secrets problem lives as much in Slack and Google Drive as in Git, and who need PII and PHI coverage in the same apps.
Pricing: A free plan for the GitHub app with a monthly scan cap. The broader platform is quote-based.
Best secret scanning tools for developers
Developers need secret scanning tools that fit naturally into their coding workflow without creating friction or slowing down development. The best developer-focused tools provide immediate feedback, clear guidance, and can be easily integrated into daily development practices.
What developers should look for:
- IDE integration for real-time feedback as you code
- Pre-commit hooks to catch secrets before they're committed
- Clear, actionable error messages that explain what was found and how to fix it
- Low false positive rates to avoid alert fatigue
- Easy setup that doesn't require extensive configuration
Top picks for developers:
Aikido Security is the best choice if you want secrets detection in the IDE and CI pipeline without managing it separately from the rest of your security coverage. The Betterleaks engine handles detection, AutoTriage filters noise before it reaches a developer, and each alert includes context explaining why a finding matters.
Betterleaks is the best option for a drop-in Gitleaks replacement. Get materially better detection, and run it on directories, files, repos, and archives without extra config. One Go binary, no dependencies, no setup gymnastics.
Best secret scanning tools for enterprises
Enterprise environments add a layer of requirements that small-team tools don't always handle, such as thousands of repos, role-based access control, audit logs for compliance, policy enforcement at the org level, and integrations with SIEM and ticketing systems. Detection accuracy still matters, but governance is where the buying decision gets made.
Enterprise requirements:
- Scalability to handle thousands of repositories and millions of commits
- Role-based access control to manage who can see and respond to different types of secrets
- Audit logging for compliance demonstrations and incident investigation
- Policy enforcement to automatically block or remediate certain types of secret exposures
- Integration with existing security tools, SIEM systems, and ticketing platforms
Top enterprise picks:
Aikido Security for complete visibility across repos with development teams owning remediation in their own context. Automated risk scoring, batch remediation, and compliance reporting against SOC 2, ISO 27001, and other frameworks. The Betterleaks engine handles detection, with the broader security posture in the same console.
GitGuardian when secrets and non-human identity (NHI) governance is its own program with dedicated owners and audit demands. The incident response workflows and identity provider integrations were built for that buyer.
TruffleHog Enterprise for security teams that need live credential verification across the broadest set of sources, including non-Git ones like S3, Slack, Jira, and Confluence.
Best open source secret detection tools
Open-source scanners give you the ability to audit detection logic, extend it for your own systems, and run it anywhere without negotiating a contract. They also tend to be the engines inside commercial products, which is exactly the case with Betterleaks running under the hood at Aikido.
Leading projects:
Betterleaks is where to start in 2026. Independent governance, MIT license, maintained by four security engineers, sponsored by Aikido without being dependent on it. Token Efficiency Scanning hits 98.6% recall on CredData (versus 70.4% for entropy), CEL-based validation confirms whether findings are live, and it's a drop-in replacement for Gitleaks. The same detection engine runs inside Aikido Security in production, which means the open-source code gets serious real-world usage.
TruffleHog is a workhorse for live verification and source coverage beyond Git. 800+ supported credential types with API verification, plus scanning across S3, Docker, Slack, Jira, and Confluence. AGPL-3.0, which is worth checking with legal if you plan to modify and redistribute.
Gitleaks still runs in countless CI pipelines and works fine for what it does. Just know that its original author has moved on to building Betterleaks, and the project has slowed.
Kingfisher is MongoDB's secret scanner, written in Rust and open-sourced under Apache 2.0 in June 2025. It began as a fork of Praetorian's Nosey Parker and has grown past detection. It validates findings against provider APIs, maps each live credential's blast radius (identity, permissions, and reachable resources) across 43 providers, and can revoke supported credentials from the same CLI. Source coverage extends beyond Git to Docker images, S3, GCS, Slack, Jira, Confluence, Teams, and Postman. Its main rule catalog is Betterleaks, with selected Veles detectors filling gaps, so Kingfisher users are already running Betterleaks rules under the hood. There's no paid tier. Validation and blast-radius mapping make authorized calls to provider APIs, so point it only at accounts you're allowed to inspect.
detect-secrets is Yelp's Python-based scanner, Apache 2.0, and it takes a different approach from everything else on this list. Instead of combing through history, it records the secrets already in a repo in a baseline file, then blocks anything new at commit time through a pre-commit hook. An audit command lets reviewers label baseline entries as real or false positives. Regex plugins cover known credential formats, and some can verify a hit over the network. Entropy and keyword detectors catch the rest, at the cost of more tuning. It skips Git history by design, and its own README concedes it won't catch multi-line secrets. Maintenance has slowed too, with the last release (1.5.0) shipping in May 2024. It's a reasonable guardrail for teams that already have it wired into pre-commit, and a harder sell as a new pick in 2026.


