

Pentesting that starts where Pentera stops.
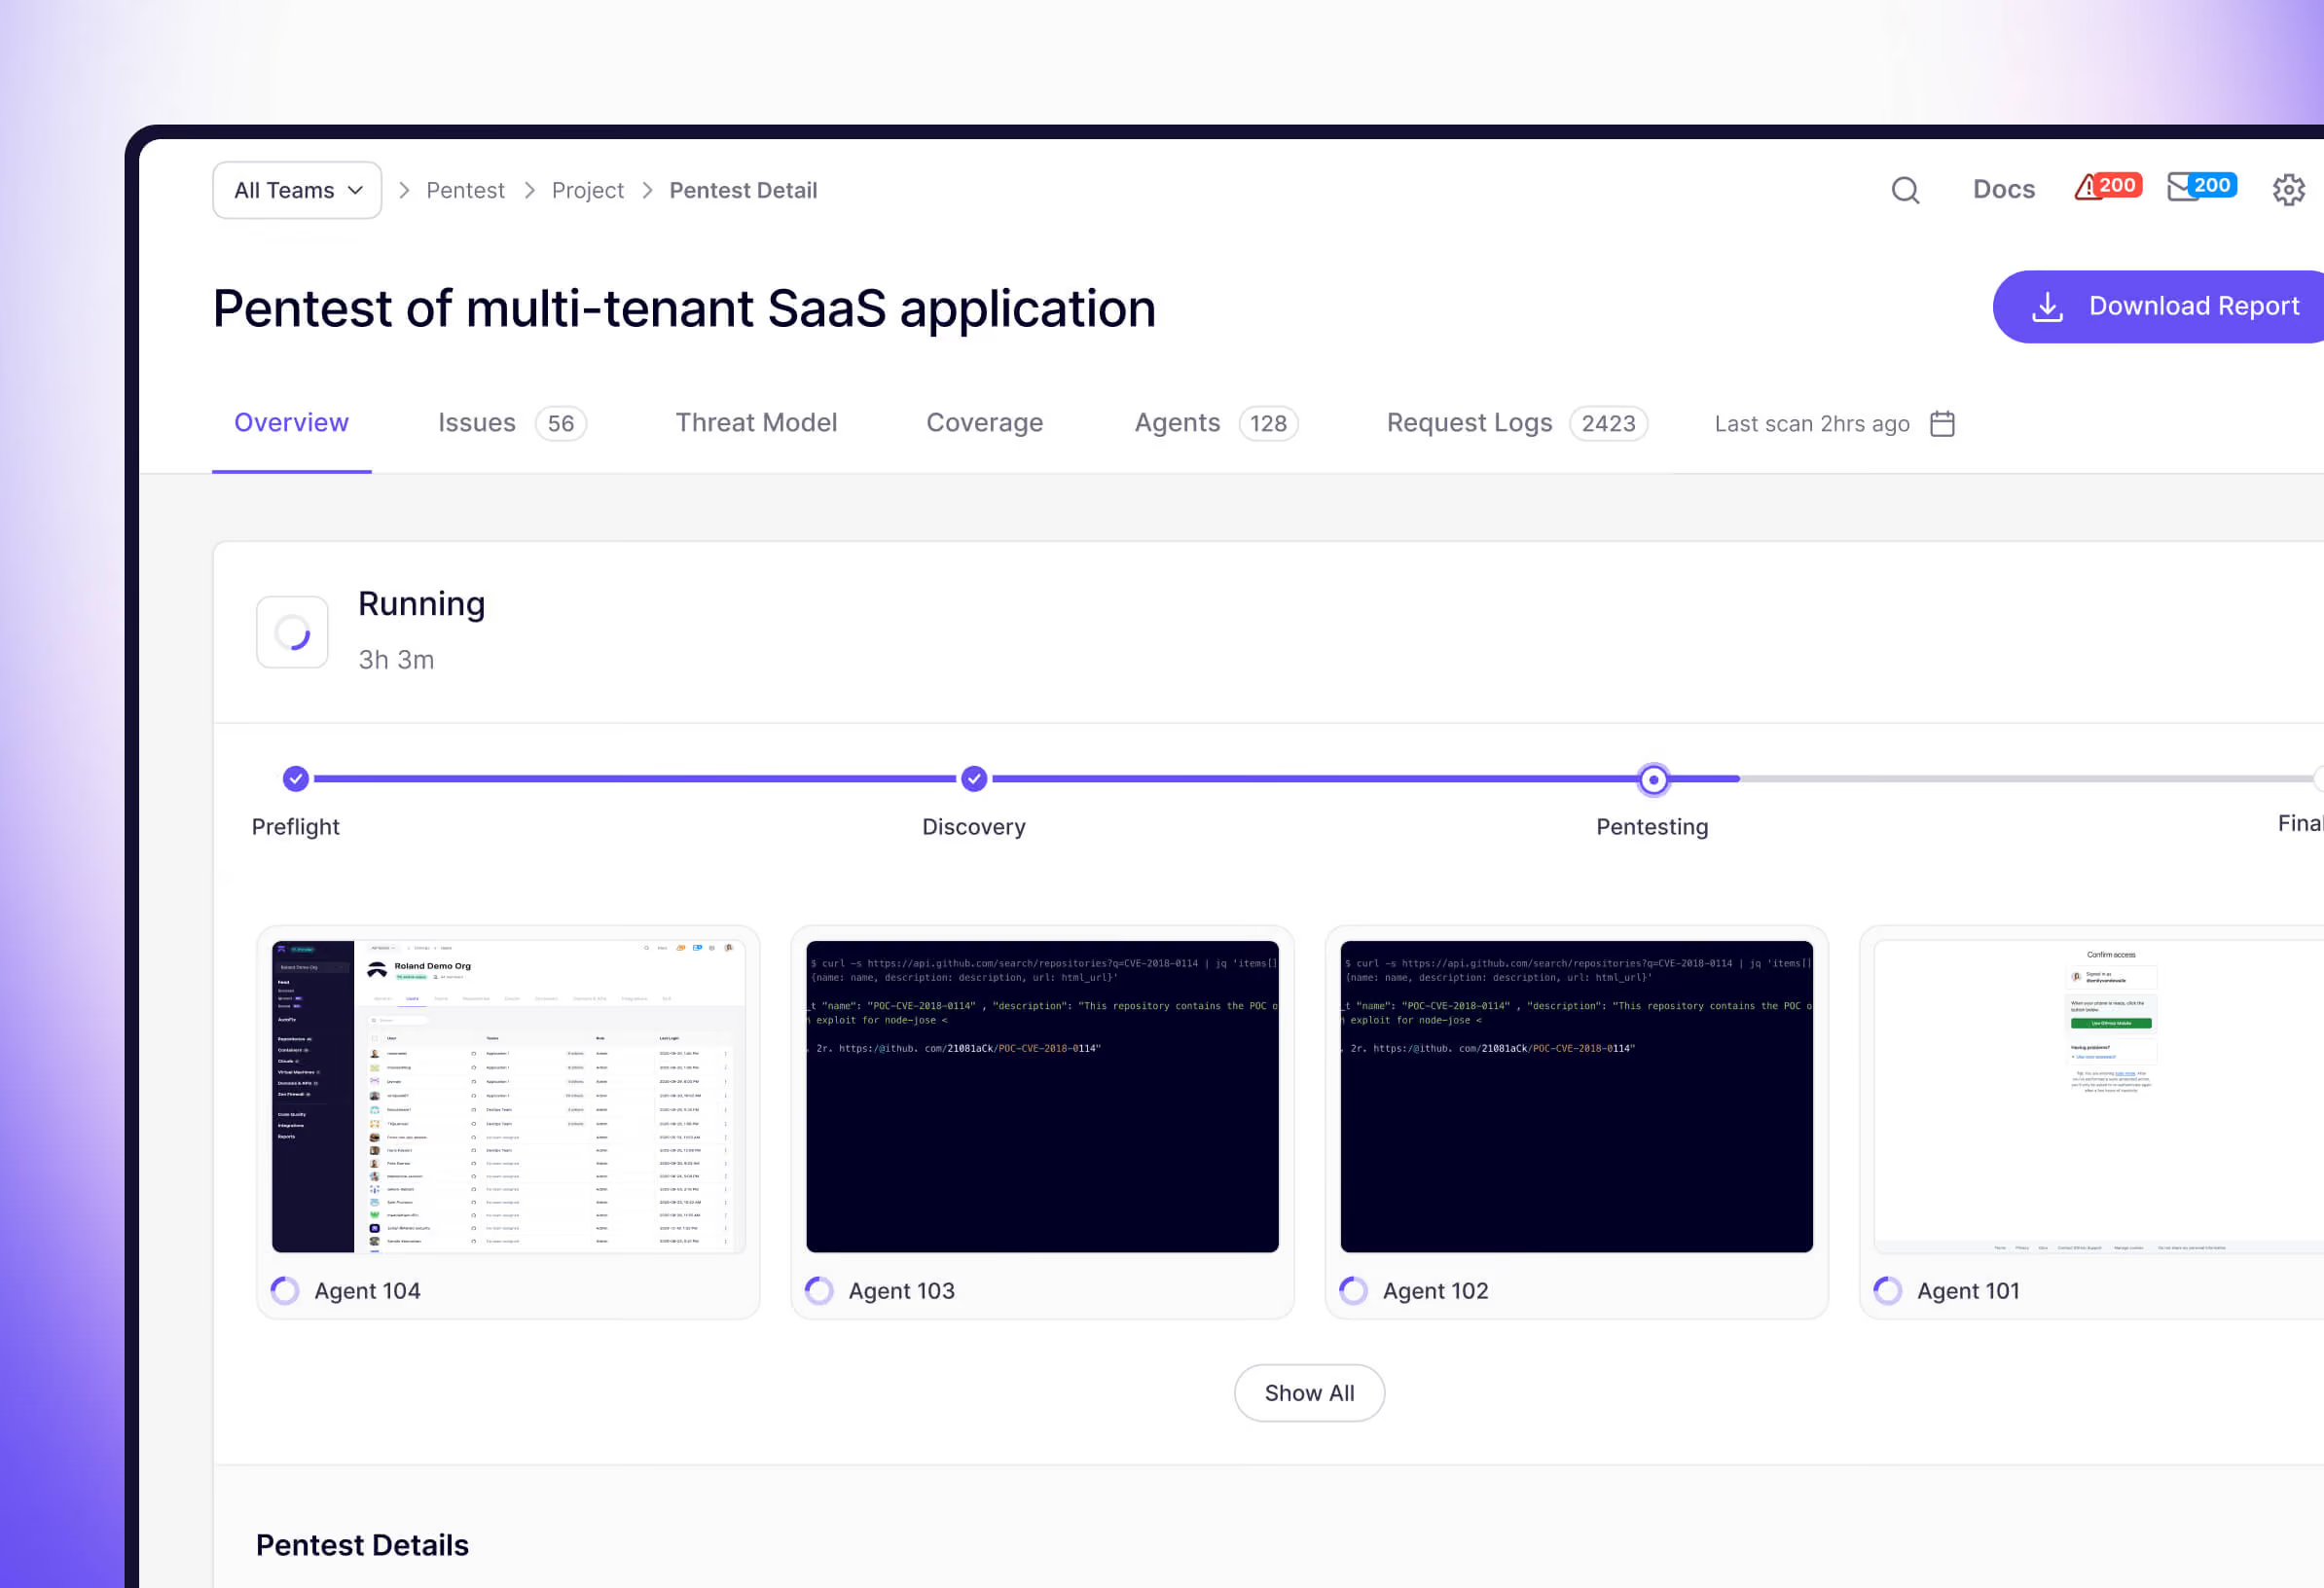
Aikido's AI agents are white-box by default. That context surfaces access-control and business-logic flaws that never show up from the outside.


Where Aikido goes further than Pentera
Pentera is black/grey-box only
Pentera tests your app from the outside, working with whatever it can see. Aikido's agents read the source code first, so they can see who's allowed to do what and catch broken access controls.
Pentera only runs attacks someone wrote in advance.
Pentera's AI varies the payloads, but the techniques come from its own library. Aikido's agents reason through your app, then exploit every finding before it reaches the report.
Air-gapped pentesting, within your premises
Most AI pentesting sends your code to a cloud model. Aikido Machine is an air-gapped GPU server in your data center that can run continuous pentests all year-round.

“We had Snyk, Wiz Code, Black Duck and Sonar in different parts of the estate. Every one of them was a good tool on its own. Together they were a mess.”
Chris HolmanDevSecOps Engineer Team Lead
Aikido vs Pentera


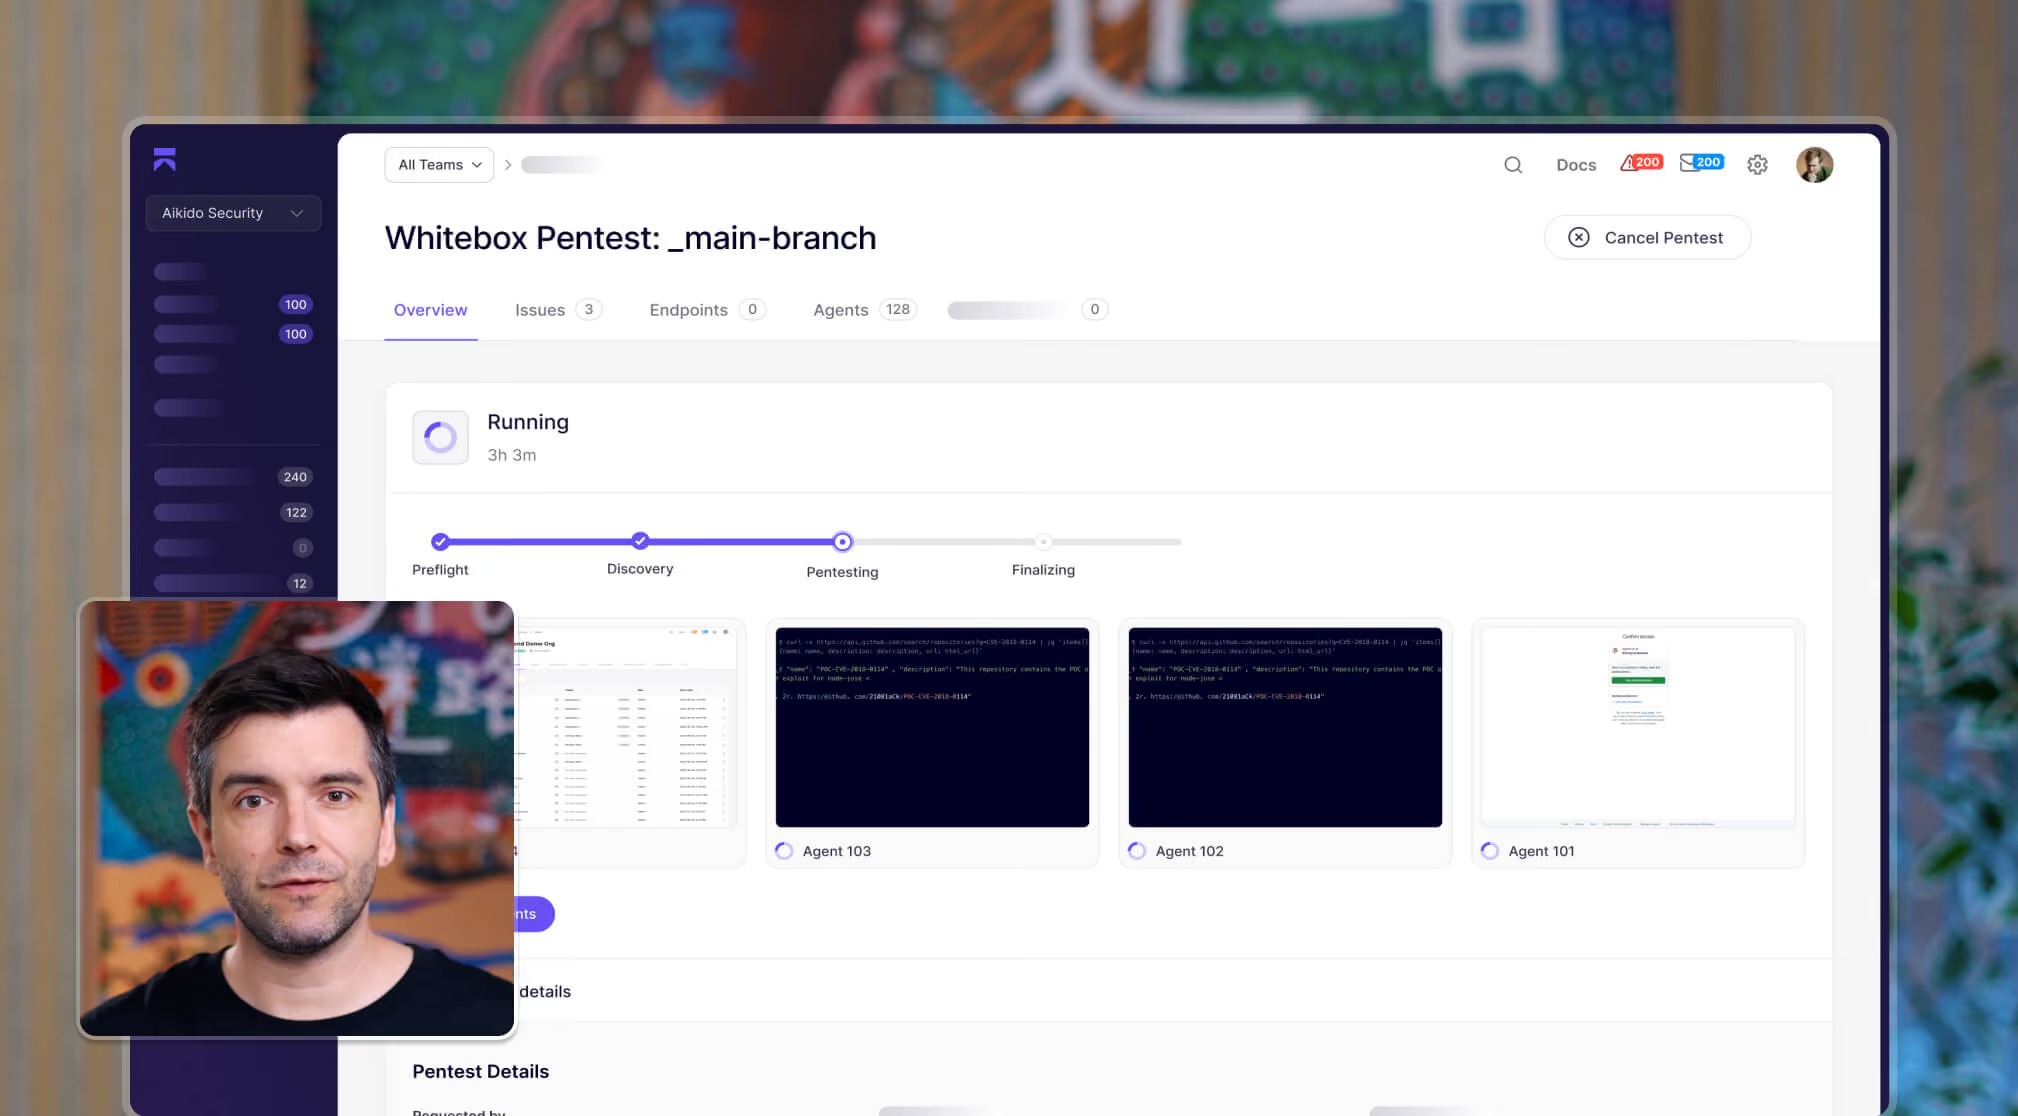

A pentest that finishes the job
Aikido doesn't stop at the finding. Hundreds of agents test your apps like a red team, then prove, fix, and retest what they find, with an audit-ready report the same day.
More context than an attacker
Reading your source, the agents catch more IDORs, broken access controls, and business logic flaws.
Prove what is exploitable
Separate agents exploit every finding to confirm it. Unproven issues are dropped, so each report features a working proof of concept.
Fixes that fit your code
Because the agents already understand your code, AutoFix opens a high-confidence PR for confirmed findings.
Human-in-the-loop
You stay in control. Aikido verifies findings but won't chain exploits or dig deeper unless you approve it first.
“I believe the effectiveness lies in Aikido’s LLM pentests utilizing far more context than a manual pentester ever could, specifically by analyzing the source code.”
KilianSecurity Operations Engineer, TechWolf

"I spent less than 15 minutes on the setup. Within a few hours, the agents had already surfaced something interesting."
Kilian J.Security Operations Engineer
Top-tier pentest, flat-rate price.
Full PDF report for SOC 2 & ISO 27001
One application, one set of APIs


Full PDF report for SOC 2 & ISO 27001
Coverage scales with your application
How a rightsized pentest is calculated

Continuous reports & real-time findings
Always-on, scales with your releases
Start your Pentest in 5min
Automated penetration testing that matches human creativity with machine speed.
Detect, exploit, and validate vulnerabilities across your entire attack surface, on demand.
