

Picking between SonarQube and Semgrep usually comes down to whether you want the tool that grades your whole codebase for quality, or the one that hunts for insecure patterns with rules you can actually read. Choose wrong and you inherit coverage gaps, a second tool to bolt on later, or an alert queue nobody has time to triage.
This article compares SonarQube and Semgrep across what decides it in practice, how they find issues, how they fit into CI, how fast they run, what they cover, and what they cost, so you can see which one suits the way your team ships.
Short answer. SonarQube is strongest at code quality with security attached. Semgrep is strongest at fast, rule-based security you can customise. Neither one covers much beyond your source code on its own, which is where a platform like Aikido Security comes in.
TL;DR
Aikido Security brings SonarQube’s code-quality analysis and Semgrep’s pattern-based detection together in one software security platform, then adds an AI and reachability engine that tells you which findings are truly exploitable.
That combination closes the gaps each tool leaves on its own, the partial coverage and the manual, noisy triage. You get coverage from code to cloud, with fewer false positives and faster triage for developers.
Aikido is modular, so you can start with one product, whether that is SAST, SCA, IaC, or code quality, and switch on more as your needs grow. Its SAST engine runs on Opengrep, the open-source engine Aikido created by forking Semgrep after Semgrep’s 2024 license change, so the open-source community kept a freely licensed static analysis engine.
Quick Feature Comparison: SonarQube vs Semgrep vs Aikido Security
What is SonarQube?
SonarQube is a continuous code-quality platform that also does static application security testing. It began as a way to catch bugs and code smells, and over time it added security coverage for common issues such as the OWASP Top 10 and hardcoded secrets. Developers like its clean web interface and the way it fits into existing workflows.
In late 2024 Sonar renamed its products, so you will now see SonarQube Server for the self-hosted analysis server, SonarQube Cloud for the hosted service, SonarQube Community Build for the free self-hosted edition, and SonarQube for IDE for the editor plugin that used to be called SonarLint.
Sonar has also extended its security coverage. The paid Advanced Security add-on, built on Sonar’s acquisition of Tidelift, adds software composition analysis along with an advanced SAST mode that follows data flow into and out of third-party libraries to catch issues that cross dependency boundaries.
What SonarQube does well
- Combines static security analysis with code-quality checks
- Gives real-time feedback in the editor through SonarQube for IDE
- Supports a wide range of languages
- Integrates with common CI/CD platforms such as Jenkins and GitHub Actions
- Has strong community support and documentation
Where it falls short
- Can produce false positives that need review
- Is still centered on code quality, with security as a second layer
- Has security rule depth that varies by language
- Covers dependencies (SCA) only through the paid Advanced Security add-on
- Offers no dynamic testing (DAST) and no runtime protection
- Needs infrastructure to run and maintain when self-hosted
- Uses lines-of-code licensing that gets expensive for large codebases
What is Semgrep?
Semgrep is an open-source static analysis tool focused on code security. Nicknamed semantic grep, it looks for vulnerable patterns using rules that read like the source code itself rather than dense regex. Teams reach for it to catch issues such as SQL injection and hardcoded credentials, and they like how far they can extend it with their own rules.
Semgrep has grown from a single open-source engine into a modular platform. The commercial side is organized into Semgrep Code for SAST, Semgrep Supply Chain for dependency risk with reachability analysis, and Semgrep Secrets for credential detection, with Semgrep Assistant adding AI triage and suggested fixes on top. The free engine still runs from the command line, while the Pro Engine adds cross-file analysis on the paid tiers.
What Semgrep does well
- Ships with community rules and lets you write your own quickly
- Fits cleanly into CI/CD and git workflows
- Uses a rule syntax that reads like the code you want to match
- Starts free, so teams can begin improving security right away
Where it falls short
- Can surface a high volume of alerts that need tuning
- Has a learning curve once you start writing custom rules
- Limits the free engine to single-file analysis, with cross-file data flow reserved for the Pro Engine
- Centers on source code, so deeper coverage and dashboards sit behind paid products
- Offers no dynamic testing (DAST) and no cloud posture monitoring (CSPM)
- Keeps team collaboration and centralized management on the paid plans
Feature-by-Feature Comparison
Security analysis capabilities
Both SonarQube and Semgrep are mainly static analyzers that read source code for bugs and security issues, and neither runs dynamic testing. With SonarQube, the security work covers the OWASP Top 10 and secret detection, and it reviews infrastructure-as-code too, all alongside its code-quality checks. It flags issues like SQL injection and cross-site scripting in source code, and it marks many findings as Security Hotspots for a person to review rather than calling them outright vulnerabilities. Semgrep relies on its rule patterns, so it detects a wide range of issues when a rule exists and its community rule set is broad, but anything no rule covers goes unreported unless you write the rule yourself. Both secure source code well and need extra tooling for full coverage, which is what pushes many teams toward a platform like Aikido Security.
Integration and CI/CD workflow
Both tools fit development workflows well. SonarQube offers CI/CD plugins for Jenkins, Azure DevOps, GitHub Actions, and GitLab CI, and teams often wire its quality gate into the pipeline so a build fails when new critical issues appear, with a web dashboard for reviewing findings. Semgrep provides a lightweight CLI that scripts into pipelines easily, with ready-to-use GitHub Actions and CI guides, so developers see security feedback next to the code they are reviewing. Both plug into the editor for real-time feedback, SonarQube through SonarQube for IDE and Semgrep through its editor extensions. SonarQube leans toward a centralized interface, while Semgrep leans toward the command line and git.
Accuracy and performance
Semgrep is fast. Its pattern-matching engine analyzes code at roughly 20,000 to 100,000 lines per second per rule, far quicker than SonarQube, which is reported closer to 400 lines per second for typical rule sets. The trade-off is volume, since Semgrep’s broad rule set can produce a lot of alerts out of the box, not all of them exploitable, so teams spend time tuning the signal. SonarQube analysis tends to be slower and heavier, and a full run can take several minutes depending on codebase size, partly because of its deeper quality metrics and the overhead of sending results to the server. On accuracy, SonarQube ships a more curated rule set built to limit noise and separates confirmed vulnerabilities from Security Hotspots, which means fewer total issues reported but a chance of missing something outside its rules. In short, SonarQube leans toward precision while Semgrep leans toward recall, and the right pick depends on whether you would rather tune down a noisy tool or risk gaps in a quieter one. Aikido Security works the other side of that trade-off, using its AI and reachability engine to surface the findings that are truly exploitable.
Coverage and scope
- Language support. Both cover a wide range of languages. SonarQube supports a broad set across its editions, including Java, C#, JavaScript, and Python, and Semgrep supports a broad and growing set too, including Go, Rust, Kotlin, Swift, and configuration formats like Dockerfiles. (Editor note: the live article says “over 10” and “over 15,” both understated. Drop in each vendor’s current published count from their own site.)
- Issue types and depth. Beyond languages, SonarQube reaches past security into code quality for a fuller picture of code health, while Semgrep stays focused on security and bug-finding and does not measure maintainability or technical debt. On its own, neither does the deep inter-procedural data-flow analysis of heavyweight enterprise SAST.
- Beyond source code. Both aim at application source code first, and their free and open versions do not natively cover container images, dependencies, or runtime. On the paid side, Semgrep’s Supply Chain product adds dependency coverage and SonarQube’s Advanced Security add-on adds SCA.
Developer experience
- User interface. SonarQube ships a polished web dashboard where developers and leads browse issues by severity and type and track metrics over time, with quality-gate status and fix guidance attached to each finding. Semgrep’s open-source tool runs from the command line and prints results or JSON, which suits individual developers and small teams, though larger teams usually want the central dashboard that comes with the paid platform.
- Workflow integration. Both aim to be developer-friendly. Each plugs into the editor, and both annotate pull requests, with SonarQube adding comments and summaries and Semgrep leaving comments on code diffs for rule violations. That inline feedback keeps security and quality checks in context during review rather than as an afterthought.
- Customization and tuning. Semgrep makes custom rules straightforward, with rules written in YAML whose patterns resemble the code you want to find, so a team can encode a house pattern or a company-specific flaw in minutes, and it supports user-defined autofix for some patterns. SonarQube is harder to extend, since writing custom rules often means Java and abstract syntax trees, so most teams toggle Sonar’s built-in rules rather than writing their own. SonarQube does let teams adjust rule severities and quality-gate thresholds and suppress false positives, but it does not auto-fix code and instead gives remediation guidance.
- Onboarding and maintenance. SonarQube setup can be heavier when self-hosted, since it means running a server and often a separate database, with cloud options to cut operational overhead at a higher cost. Maintenance covers server upgrades, access management, and keeping analyzers current, and Sonar provides extensive documentation and a large knowledge base. Semgrep is quick to start, installs as a single CLI binary, and runs locally or in CI, with an optional server component only if you use the Semgrep platform. Its maintenance is mostly keeping rule sets current, which is simple because rules are versioned and distributed through the registry.
Compliance and reporting
SonarQube’s Enterprise tier offers portfolio reports and governance features, and you can map its rules to compliance requirements and generate reports for auditors. Semgrep does not provide compliance reporting out of the box, though you can apply rules mapped to standards such as the OWASP Top 10 or secure-coding guidelines.
Release cadence and updates
Semgrep ships quickly, often several times a month, and its rules update frequently and ship independently of the tool, so teams can adopt new checks fast and respond to newly disclosed vulnerabilities. SonarQube follows a slower, more structured cycle, with major versions a few times a year and rule updates generally bundled into releases, which can delay access to new checks.
Pricing
With SonarQube, the Community Build is free and self-hosted, but much of the advanced security work, the deeper analysis, the extra language support, and the enterprise governance sits in the paid editions, including the Advanced Security add-on. Sonar prices on the lines of code analyzed, which can be hard to predict and gets expensive for large codebases.
Semgrep keeps a free, open command-line engine and community rules at no cost whatever the size of the codebase. Its paid platform now runs on tiered pricing, with a Teams tier that bundles its Code, Supply Chain, and Secrets products along with the AI Assistant and starts at roughly 30 to 40 dollars per contributor per month, and an Enterprise tier with custom pricing. The free tier caps usage at a small number of contributors and repositories, so growing teams tend to move onto Teams.
In short, SonarQube costs can climb as codebases grow and it carries infrastructure to maintain, while Semgrep starts low or free and shifts cost to a per-contributor model for its advanced products.
Aikido offers a flatter, more predictable pricing model, with a free tier and pricing that stays easier to forecast as your codebase grows.
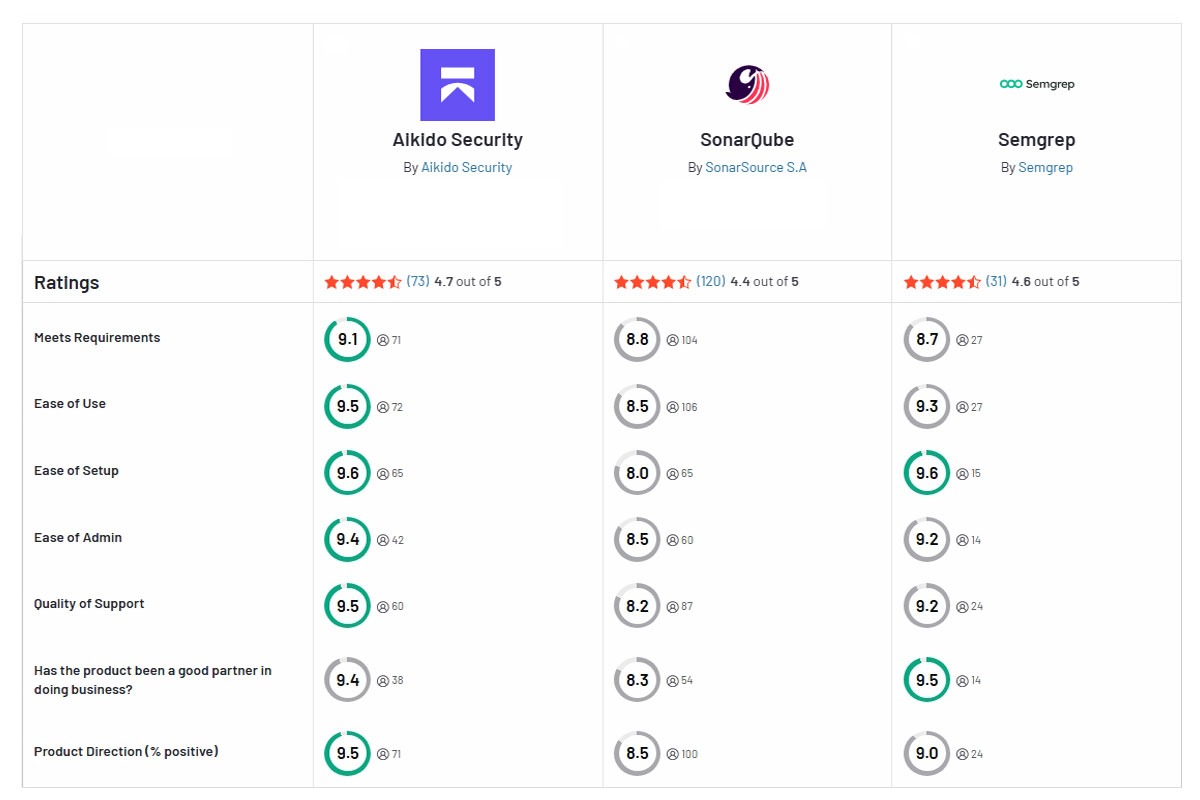
To help you compare the features of both tools, the table below summarizes it for you.
Aikido Security
The complete platform

Aikido Security is a software security platform that brings SonarQube’s code-quality strengths and Semgrep’s pattern-based detection together, then correlates what it finds across code, dependencies, cloud, and runtime so security and engineering teams work from one source of truth.
For teams that have to answer to a security review, that consolidation is the point. Aikido gives you role-based access control and single sign-on, with audit trails across the platform and compliance reporting mapped to frameworks like SOC 2 and ISO 27001, and it connects to the governance tooling teams already run, such as Drata and Vanta. Replacing several point tools with one platform cuts the consoles and contracts a security team has to manage and keeps findings in one place for policy and reporting.
The coverage spans source code, dependencies, container images, infrastructure-as-code, cloud configuration, and APIs, all in one workflow. Its SAST runs on Opengrep, the open-source engine Aikido created by forking Semgrep after the 2024 license change. The AI and reachability engine correlates findings across those layers, flags the ones that are truly exploitable, and gives developers automated remediation through pull requests and one-click fixes.
Because it is modular, teams can start with one product, whether SAST, SCA, IaC, DAST, secrets detection, or container image scanning, and switch on more as they grow, without stacking up separate tools.
Developers get the workflow they want on top of that enterprise base, feedback in the pull request, fixes they can accept in a click, and far less noise to wade through, so the governance a security team needs does not come at the cost of developer speed.
Want full visibility across everything your team builds, ships, and runs? Start your free trial or book a demo with Aikido Security.
FAQ
Which is better, SonarQube or Semgrep?
There is no universal winner. SonarQube fits teams that care most about long-term code quality and technical-debt tracking, and Semgrep fits security-focused teams that want fast, customizable rules inside a developer workflow. If you need to cover more than source code, a platform like Aikido Security combines both approaches and adds dependency, cloud, and runtime coverage.
What are the main limitations of SonarQube compared to Semgrep?
SonarQube is heavier to run and less flexible on rules, while Semgrep is lighter but asks you to invest in tuning. SonarQube leans on centralized analysis and quality gates, which can feel rigid for fast-moving teams or less common languages. Semgrep is lighter and more flexible, though that flexibility means choosing, writing, and maintaining rules to keep the noise down.
How do SonarQube and Semgrep detect code issues?
They take different routes to the same goal. SonarQube uses traditional static analysis, parsing the code and following its control and data flow to surface bugs and security issues. Semgrep matches readable rules against the code to spot insecure patterns, which makes each finding easy to trace back to a specific line.
Can you customize Semgrep rules as easily as SonarQube rules?
Yes, more easily. Semgrep rules are written in a readable YAML format that developers can create and change quickly. SonarQube supports custom rules too, but it usually calls for deeper platform knowledge or Java, which is a higher bar for most teams.
What do you gain from Semgrep’s pattern-based approach over SonarQube’s traditional analysis?
Speed and control. Semgrep’s patterns let a team write and enforce security or code-quality practices specific to their stack, which works well for catching known insecure patterns and responding quickly to newly disclosed vulnerabilities. SonarQube’s traditional analysis is stronger for general code quality and maintainability.
You Might Also Like:




